9 Best Data Breach Detection Tools (2026)
Quick Summary
The best data breach detection tools are Breachsense for credential alerts and search inside vendors’ leaked files, SpyCloud for catching work passwords reused on personal accounts and UpGuard for scoring your vendors’ security.
| Tool | Type | Best for | Rating |
|---|---|---|---|
| Breachsense | Credential and dark web monitoring | Teams that want credential alerts from stealer logs, combo lists, phishing kits and third-party breaches, plus search inside vendors’ leaked files | 4.8/5 (G2) |
| SpyCloud | Infostealer intelligence | Identity teams that want to catch work passwords employees reused on personal accounts | 4.7/5 (G2) |
| UpGuard | Attack surface and vendor risk | Lean security teams that want their own attack surface and their vendors’ security ratings from one vendor | 4.5/5 (G2, Vendor Risk) |
Looking for the best breach detection tools?
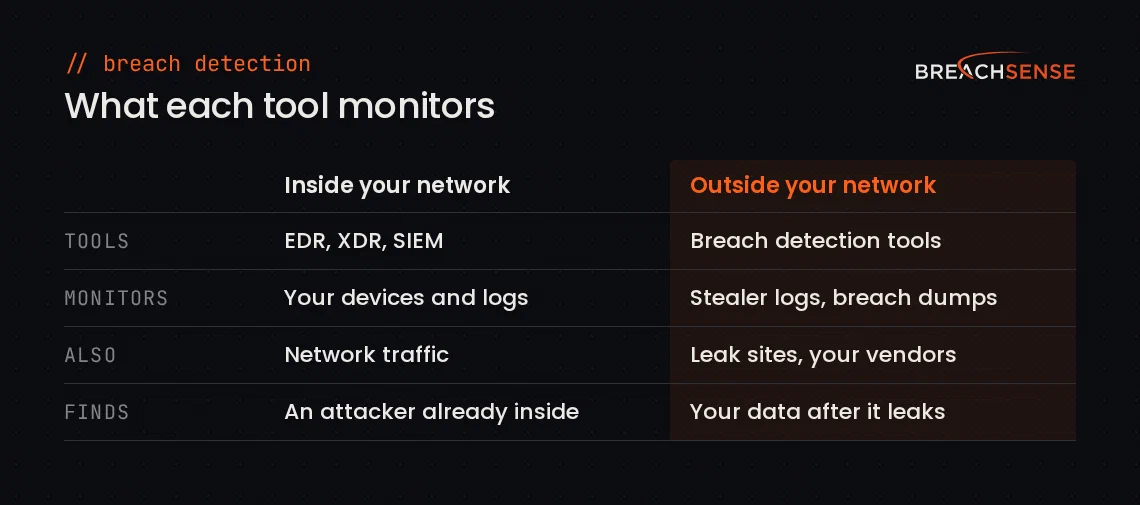
Your security tools watch what happens inside your network. They can’t see an employee’s password stolen from a home laptop, or your customer list in a vendor’s leaked files. Stolen data like this gets posted or sold on criminal forums and Telegram channels.
For the password stolen from the home laptop, a data breach detection tool alerts you when the employee’s credentials appear in a stealer log. For the customer list, the tool has to index the vendor’s leaked files themselves. Some tools only tell you the vendor was breached. Our guide on how to detect a data breach covers the wider process.
Why listen to us?
Breachsense is a dark web monitoring API with over 42 billion leaked credentials indexed. Our ransomware research has been cited by TechTarget and The Register.
What are data breach detection tools?
Data breach detection tools watch the places where stolen data ends up and alert you when your company’s data appears there. Those places include hacker forums, Telegram channels, stealer logs, breach dumps and ransomware leak sites.
A stealer log is the file infostealer malware sends back to the attacker. It holds the saved passwords and session cookies copied from an infected device’s browser. Our glossary entry on stealer logs covers what else they contain.
A breach detection system watches your own network. EDR (endpoint detection and response) and XDR (extended detection and response) watch your devices, and a SIEM (security information and event management) collects your security logs. All three look for an attacker who’s already inside.
The tools on this list fall into four types:
- Credential and dark web monitoring. Finds leaked employee and customer credentials and company data on forums and markets, and in third-party breaches. Also alerts you when one of your vendors is breached.
- Infostealer intelligence. Focuses on stealer logs and the infected devices they come from.
- Threat intelligence. Tracks attackers, malware and vulnerabilities, with dark web monitoring as one module.
- Attack surface and vendor risk. Maps your internet-facing assets, including subdomains your IT team doesn’t know about (shadow IT). Tracks breaches at your vendors too. Some tools also score your company’s security and each vendor’s.
For how monitoring fits into a wider program, see data breach monitoring.
Why is data breach detection important?
- Breaches cost more than ever. IBM’s Cost of a Data Breach Report 2026 puts the global average cost of a data breach at $4.99 million, up 12% on last year and a record high.
- A third party is involved in about half of breaches. Verizon’s 2026 Data Breach Investigations Report (DBIR) found third-party involvement in 48% of breaches, up from 30% the year before (p.20). When a vendor holding your data is breached, your data leaks with theirs.
- Stolen session cookies bypass multi-factor authentication (MFA). Infostealer malware copies session cookies from the browser. An attacker who loads a valid cookie is already signed in, so there’s no password or MFA prompt to stop them.
- Reused passwords leak in other sites’ breaches. When an employee uses a work password on another site and that site is breached, the password lands in the breach dump. Because the breach happens on another company’s systems, none of your own security logs record it.
- Tools inside your network only see an attack once it starts. EDR and a SIEM flag an attacker who signs in or runs malware. A leaked password for sale on a forum triggers neither until someone uses it.
9 best data breach detection tools
- Breachsense
- SpyCloud
- UpGuard
- Recorded Future
- Cyble
- SOCRadar
- CrowdStrike Falcon Adversary Intelligence
- Google Threat Intelligence
- Hudson Rock
| Tool | Type | Best for | Rating |
|---|---|---|---|
| Breachsense | Credential and dark web monitoring | Teams that want credential alerts from stealer logs, combo lists, phishing kits and third-party breaches, plus search inside vendors’ leaked files | 4.8/5 (G2) |
| SpyCloud | Infostealer intelligence | Identity teams that want to catch work passwords employees reused on personal accounts | 4.7/5 (G2) |
| UpGuard | Attack surface and vendor risk | Lean security teams that want their own attack surface and their vendors’ security ratings from one vendor | 4.5/5 (G2, Vendor Risk) |
| Recorded Future | Threat intelligence | Enterprises with a threat intelligence team that also want credential monitoring | 4.5/5 (G2) |
| Cyble | Credential and dark web monitoring | Enterprises and governments that want dark web monitoring and third-party breach analysis in one platform | 4.8/5 (G2) |
| SOCRadar | Threat intelligence | Small and mid-sized companies that want dark web monitoring at a published price | 4.7/5 (G2) |
| CrowdStrike Falcon Adversary Intelligence | Threat intelligence | SOC (security operations center) teams already running CrowdStrike Falcon | 4.7/5 (Gartner Peer Insights) |
| Google Threat Intelligence | Threat intelligence | Threat intelligence teams that want Mandiant research and VirusTotal data | 10/10 (TrustRadius) |
| Hudson Rock | Infostealer intelligence | Teams that only need infostealer data, with free lookups to start | Not enough reviews |
1. Breachsense
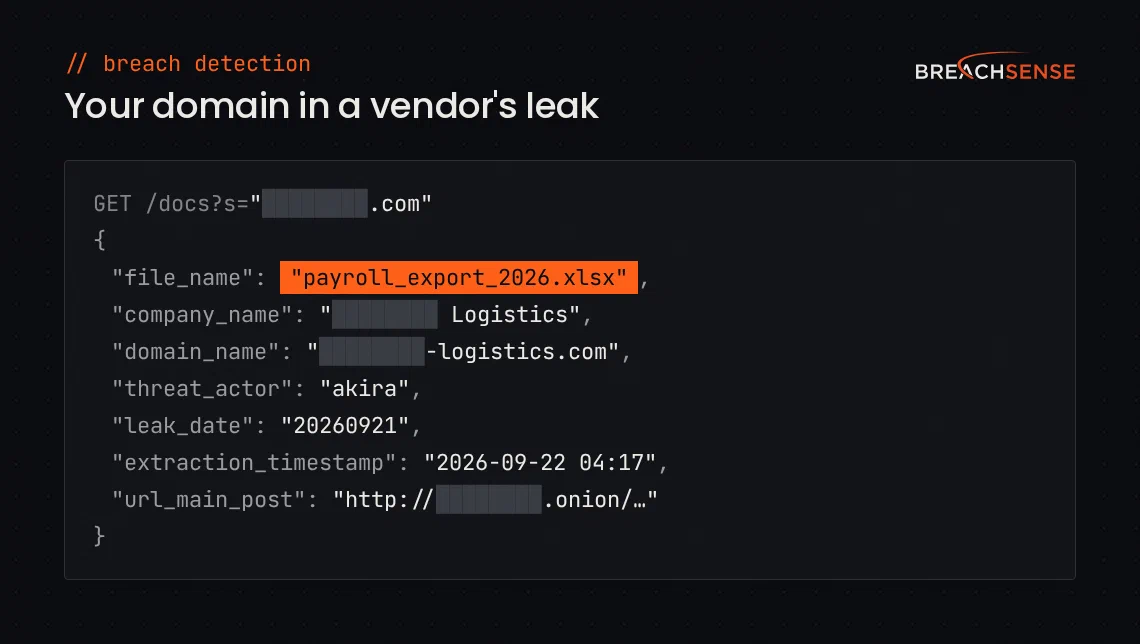
Breachsense lets you find your company’s data in other companies’ breaches. Our index covers the files that ransomware groups publish when a victim won’t pay. The index also covers vendor breach dumps and data left in unsecured databases. You can search inside the indexed files for your domains, employee names or project names. If a ransomware group publishes a vendor’s files, you can check which of your records were in them before the vendor discloses the breach. Our page on vendor breach detection covers how the search works.
For credentials, we collect from stealer logs, combo lists (lists of email and password pairs recirculated from older breaches), phishing kits and third-party breaches. Each alert shows where the credential came from and the date we first found it.
Breachsense is an API, with no dashboard to log in to. A webhook sends each alert to your SIEM or SOAR tool (the system that runs response steps automatically). Your SOAR tool can then open a ticket or force a password reset.
Key features
- Leaked file search. Indexes files published by 100+ ransomware groups and in vendor breach dumps, so you can search them for your company’s data.
- Vendor breach alerts. Alerts you when a vendor’s domain you monitor is named on a ransomware leak site.
- Stealer log monitoring. Finds employee and customer credentials taken by infostealer malware. Alerts also show the infected machine’s name and the malware’s file path when the stealer log records them. On a company device, the path gives your team a file to search for with EDR, on that machine and on your other endpoints.
- Plaintext passwords. Cracks many password hashes in weak formats back to plaintext. Passwords stored with strong hashing are practically impossible to crack.
- Leaked session tokens. Flags stolen session cookies that bypass MFA.
- Phishing-harvested credentials. Catches passwords employees typed into phishing pages.
- Leaked API keys. Finds API keys and OAuth tokens in stealer logs and leaked ransomware files.
Pricing: Not published. On a demo call, we learn your requirements, then put together a package that covers only what you need. A trial is available after the demo.
Rating: 4.8/5 on G2
Pros
- Lets you search inside vendors’ leaked files for any term, such as a domain or a project name.
- Nothing to install. You get a license key and example API queries. Most teams are up and running within an hour.
- Pricing doesn’t depend on how many employees you have.
Cons
- No dashboard. Alerts arrive by webhook or email, so you need a tool or inbox to route them to.
- Doesn’t monitor social media for fake profiles impersonating your company or executives.
- No published prices.
2. SpyCloud
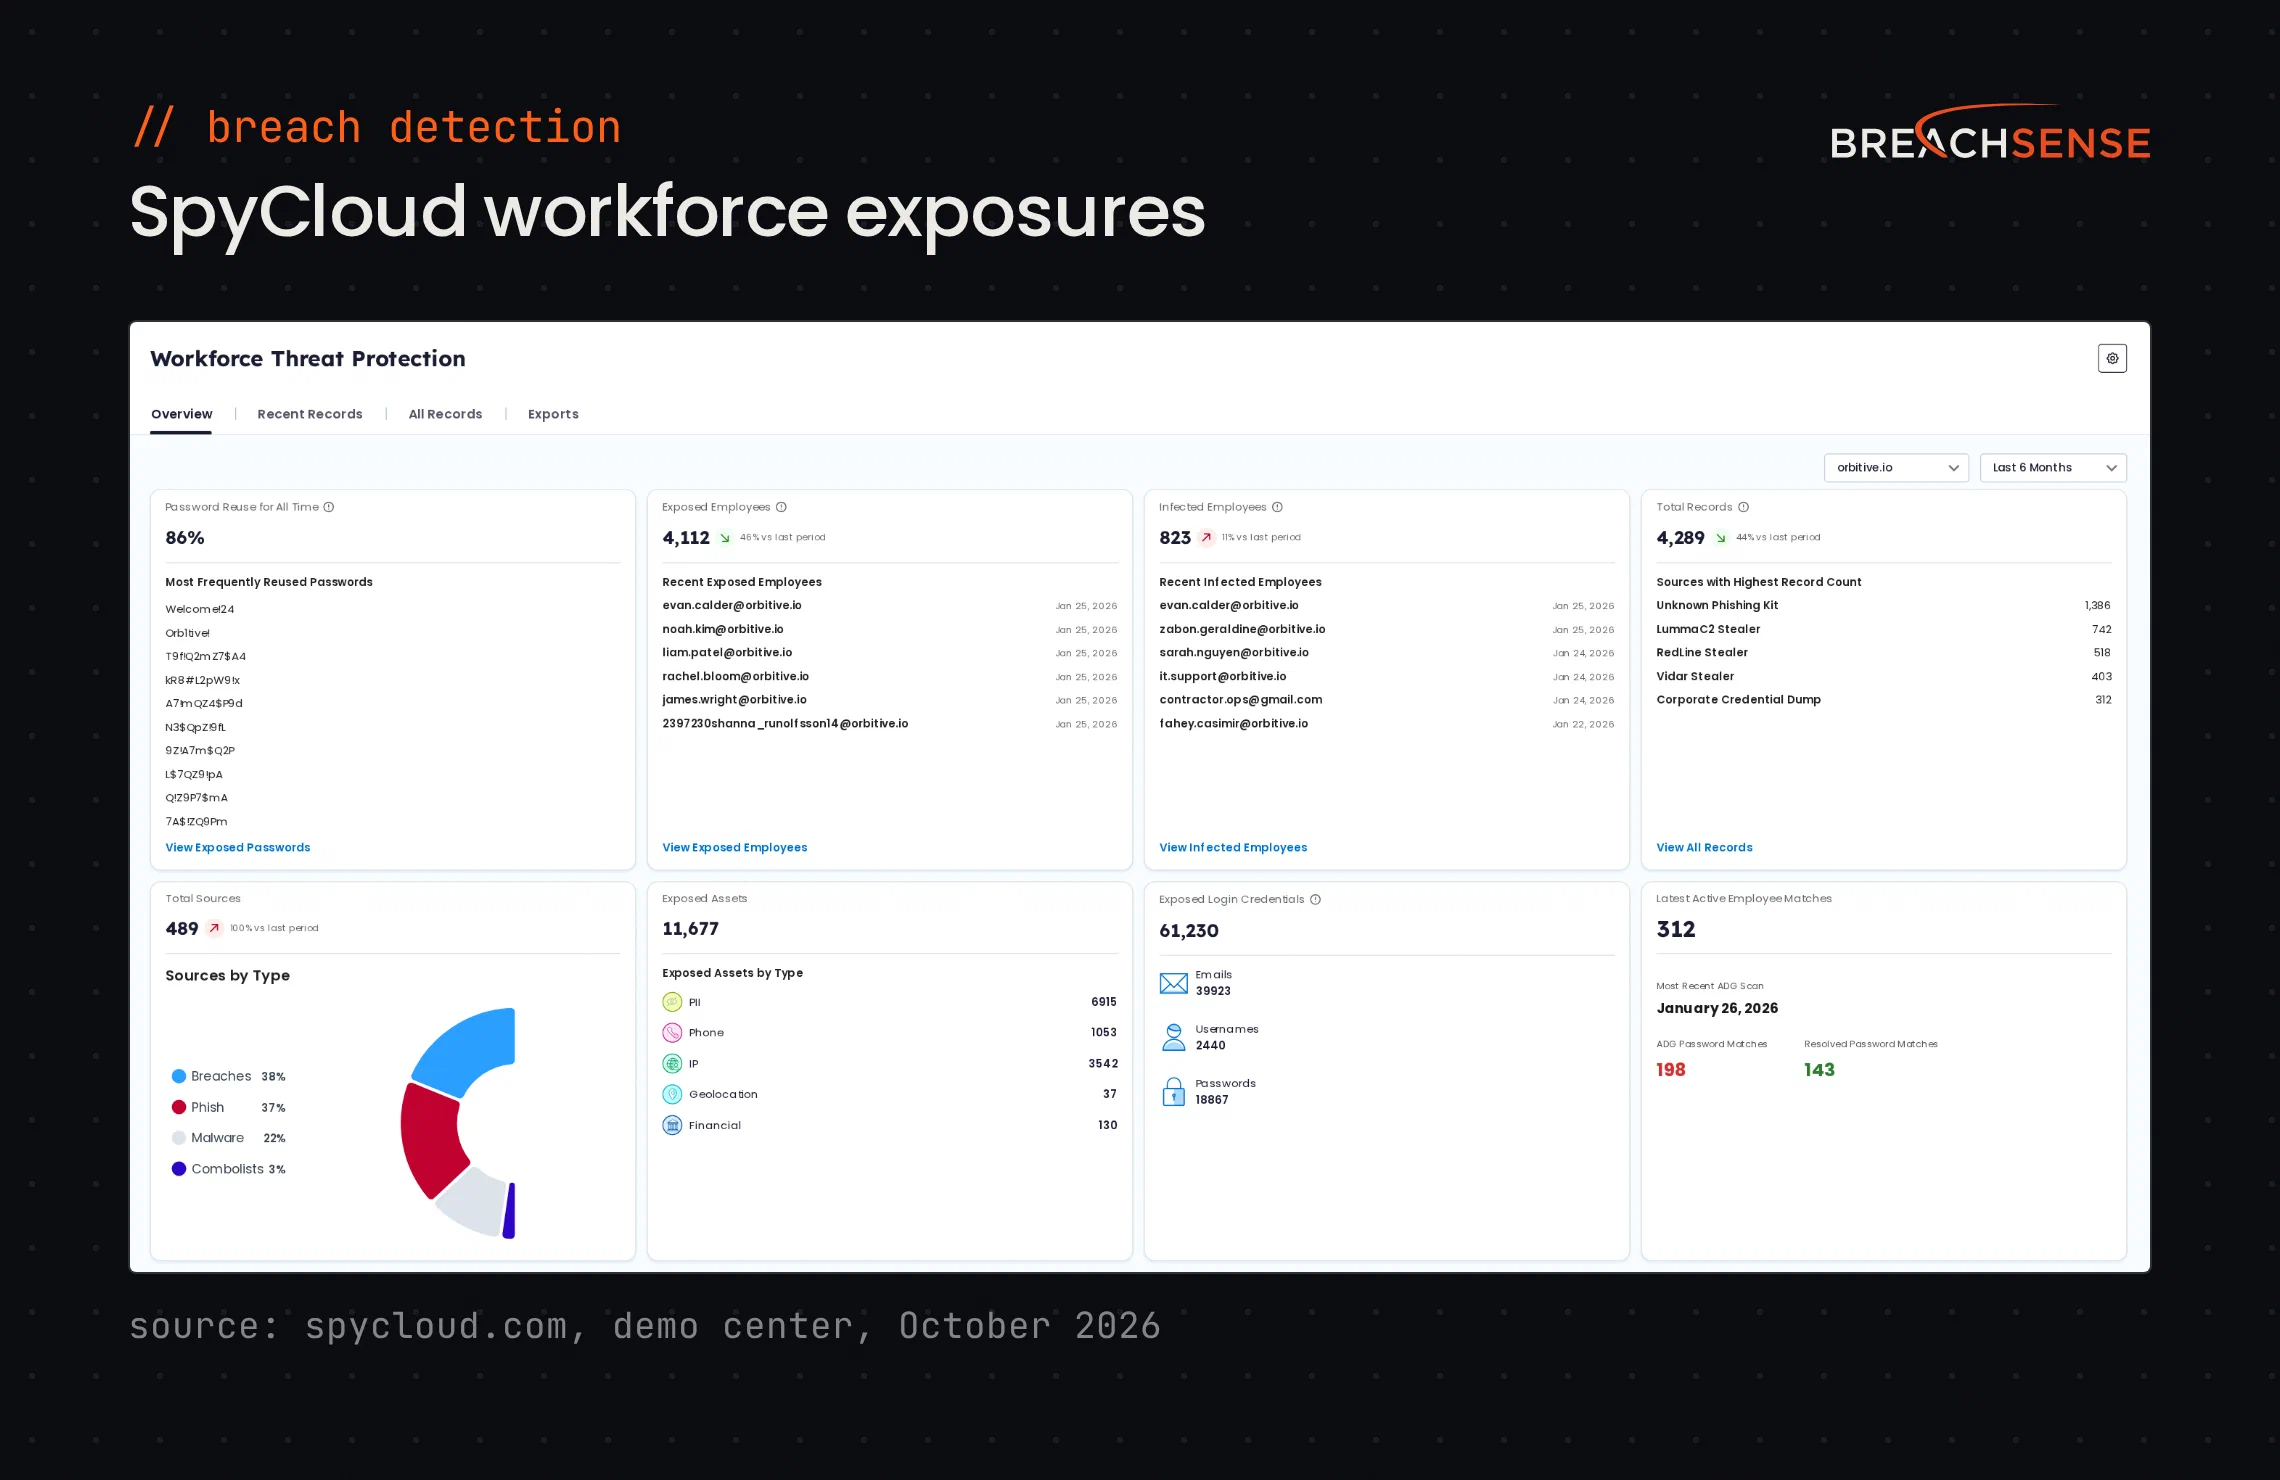
SpyCloud is built for security and identity teams protecting employee and contractor accounts. SpyCloud matches stolen passwords and session cookies to your workforce, including passwords employees reused on personal accounts. Your team can then reset the affected work passwords in Active Directory, Okta or Entra ID.
SpyCloud says its data lake holds 65.7 billion distinct identity records, 23% more than in 2025. See our Breachsense vs SpyCloud comparison.
Key features
- Four exposure sources. Collects credentials and session cookies from malware logs, phishing kits, combo lists and breaches.
- Session revocation. Revokes stolen sessions in Active Directory, Okta Workforce or Entra ID.
- Personal account matching. Links employees’ personal accounts to their work identity. SpyCloud says personal account matching finds 14 times more plaintext passwords per user than matching on the company domain alone.
- Vendor exposure scores. Rates vendors by how many of their employees were exposed through malware, phishing or breaches.
Pricing: Not published. SpyCloud tiers its Enterprise Protection pricing by the number of employee accounts protected. SpyCloud offers a free exposure check but no free trial.
Rating: 4.7/5 on G2
Pros
- The interface is simple to use day to day.
- New breach data shows up fast, sometimes before the breach makes the news.
- The Active Directory integration flags employees whose current password matches a leaked one, with little upkeep.
Cons
- As more companies deploy MFA, smaller organizations find the price harder to justify.
- Rolling out several SpyCloud modules at once is hard, so plan to add them in stages.
3. UpGuard
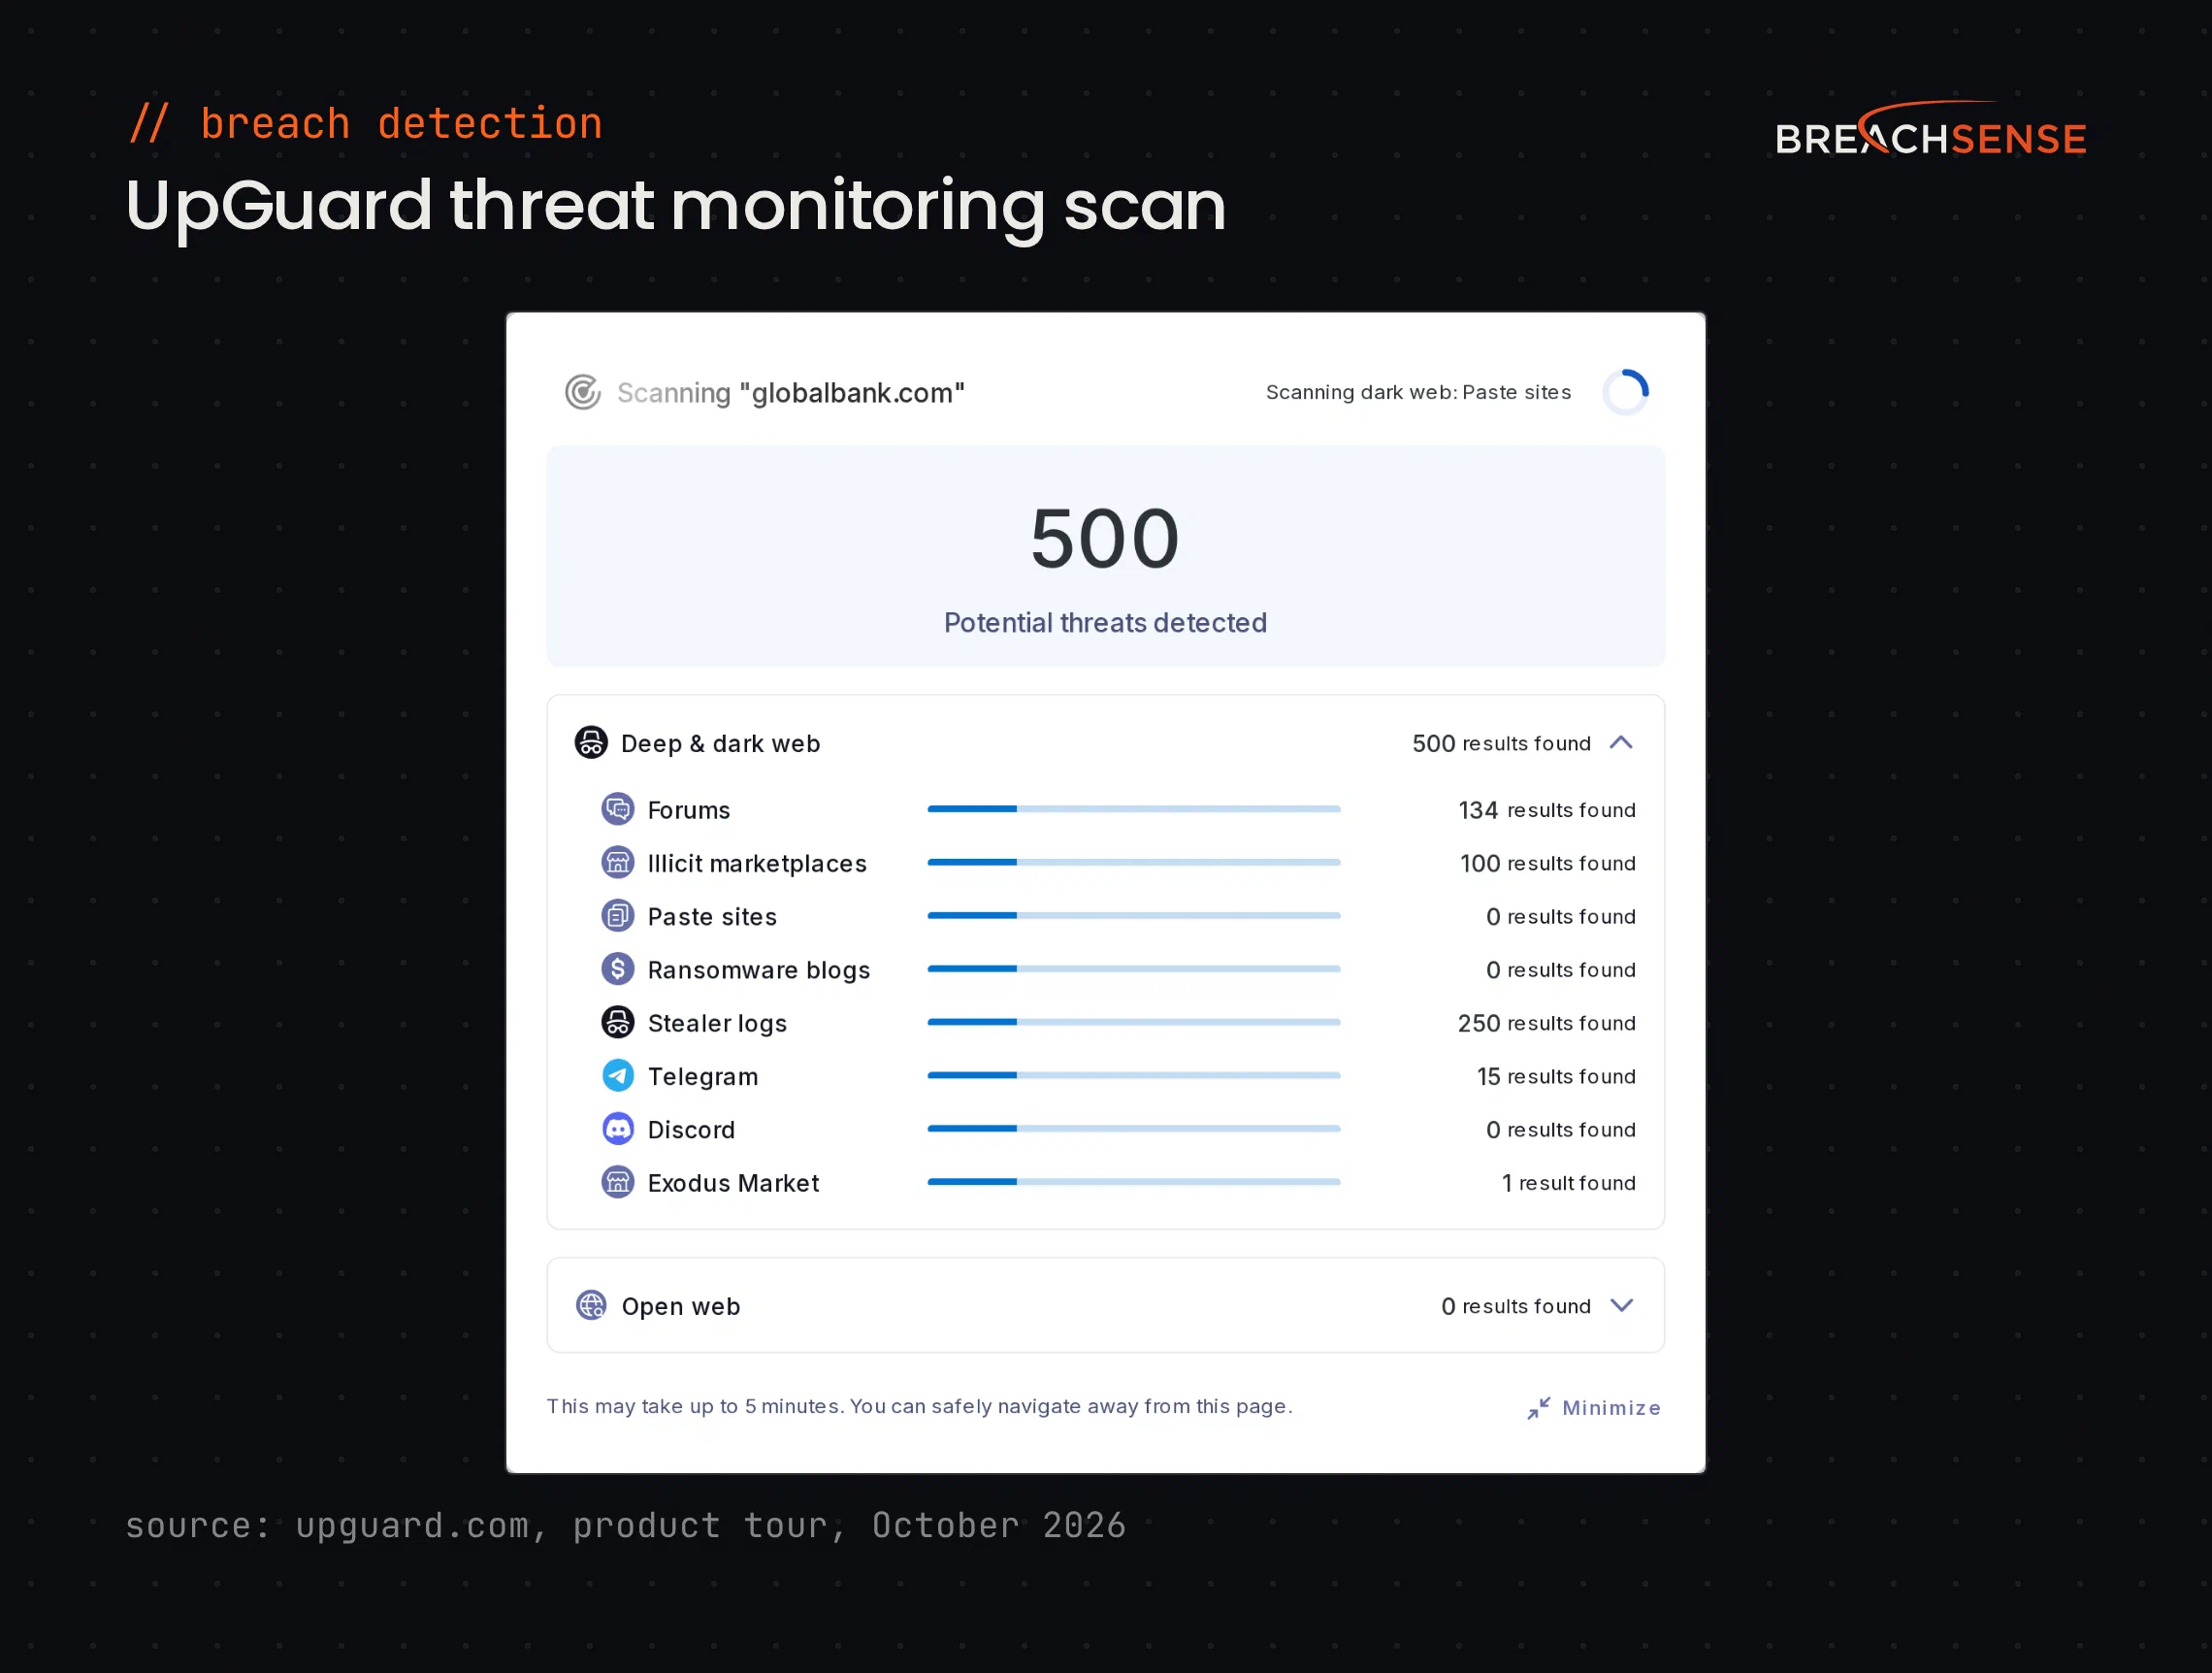
UpGuard Breach Risk combines attack surface management with dark web monitoring. UpGuard markets Breach Risk to lean security teams. UpGuard’s separate Vendor Risk product scores your vendors’ security and alerts you when one of your vendors is breached.
UpGuard says its vendor scores draw on more than 15 million organizations, each scanned across 400+ risk signals. Breach Risk was previously called BreachSight.
Key features
- Dark web monitoring. Collects from ransomware leak sites, dark web forums, infostealer logs and Telegram channels.
- Data leak detection. Scans for exposed personal data and internal documents belonging to your company.
- AI triage. Filters dark web findings and ranks the leaked credentials, malware logs and ransomware mentions that matter most.
- Vendor breach alerts. Vendor Risk alerts you when a vendor has a breach or a major security event.
Pricing: UpGuard’s help center lists a self-service Breach Risk plan from $250 a month, but self-service doesn’t include dark web monitoring. Plans with dark web monitoring start at $19,999 a year. UpGuard offers a 14-day free trial.
Rating: 4.5/5 on G2, from reviews of UpGuard Vendor Risk.
Pros
- The interface is easy to navigate, so new users pick it up quickly.
- Vendor assessments, questionnaires and evidence sit in one place instead of spreadsheets and email threads.
- Continuous monitoring flags a vendor’s security issues between scheduled reviews.
Cons
- The price is high for smaller teams. Some features, including Breach Risk, need a higher-priced plan.
- Questionnaire scoring and assessment workflows are hard to customize.
- Findings can feel dense or generic. Some findings need manual checking before you share them with the vendor.
4. Recorded Future
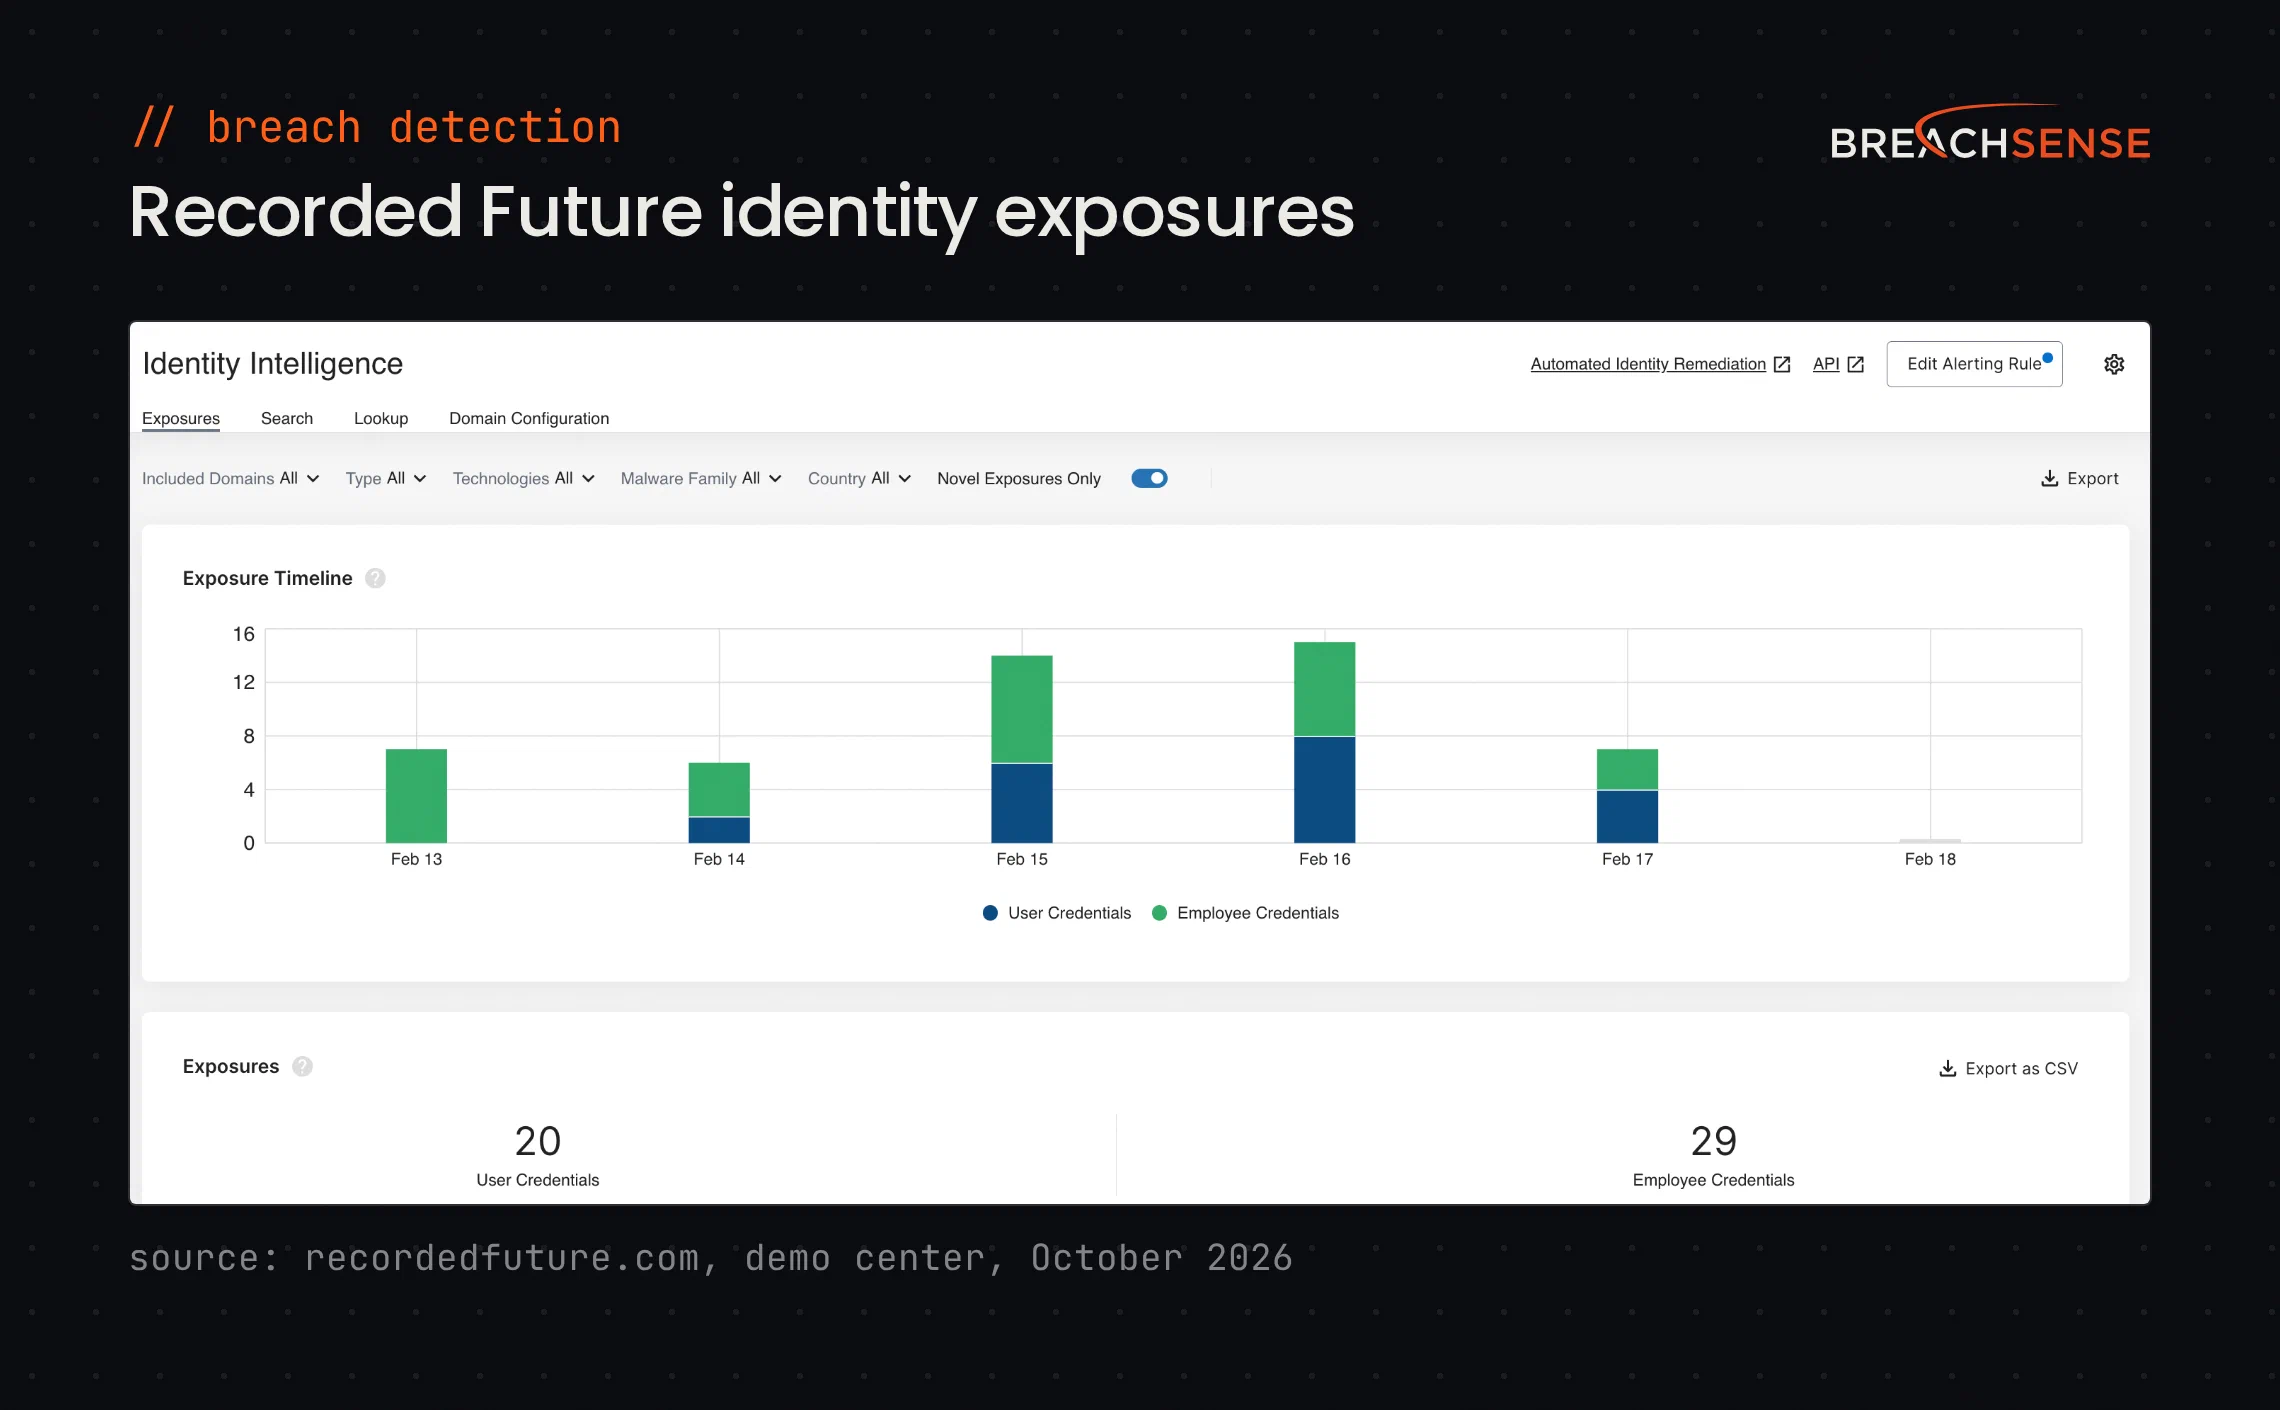
Recorded Future is a threat intelligence platform owned by Mastercard. Credential monitoring sits in its Digital Risk Protection solution and its Identity Intelligence module. Recorded Future suits enterprises whose threat intelligence team will also use the platform’s vulnerability and third-party risk data.
Recorded Future says its platform collects from more than a million sources. Recorded Future’s compromised host reports list every credential stolen from an infected machine. Recorded Future says the average infected machine in 2025 held 87 credentials. See our guide to Recorded Future alternatives.
Key features
- Credential exposures. Finds exposed credentials in infostealer logs, combo lists and database dumps.
- Exposure context. Adds the malware family, host details, password complexity and the login URL to each exposure.
- Automated response. Triggers password resets and MFA challenges through IAM (identity and access management) and SOAR tools such as Okta and Cortex XSOAR.
- Vendor event alerts. Flags vendor breaches, extortion site mentions and credential leaks, in the Elite package or the Third-Party Risk solution.
Pricing: Not published. Recorded Future prices its Core, Professional and Elite packages mainly by organization size, which it measures in unique workforce credentials. There’s no free trial, but Recorded Future offers a free report on your domain’s credential exposure.
Rating: 4.5/5 on G2
Pros
- An analyst can look up an IP address, domain or CVE (a published vulnerability ID) and see a risk score with the evidence behind it.
- Integrations with SIEM and SOAR tools add Recorded Future’s risk scores to alerts the team already handles.
- Monitoring of forums and Telegram channels replaces work analysts would otherwise do by hand.
Cons
- The price is high, and capabilities like identity intelligence and third-party risk are sold as separate modules.
- The amount of data and the query language take a long time to learn, especially for analysts who don’t use the platform every day.
- Alerts need tuning. Some alerts still need manual checking before anyone acts on them.
5. Cyble
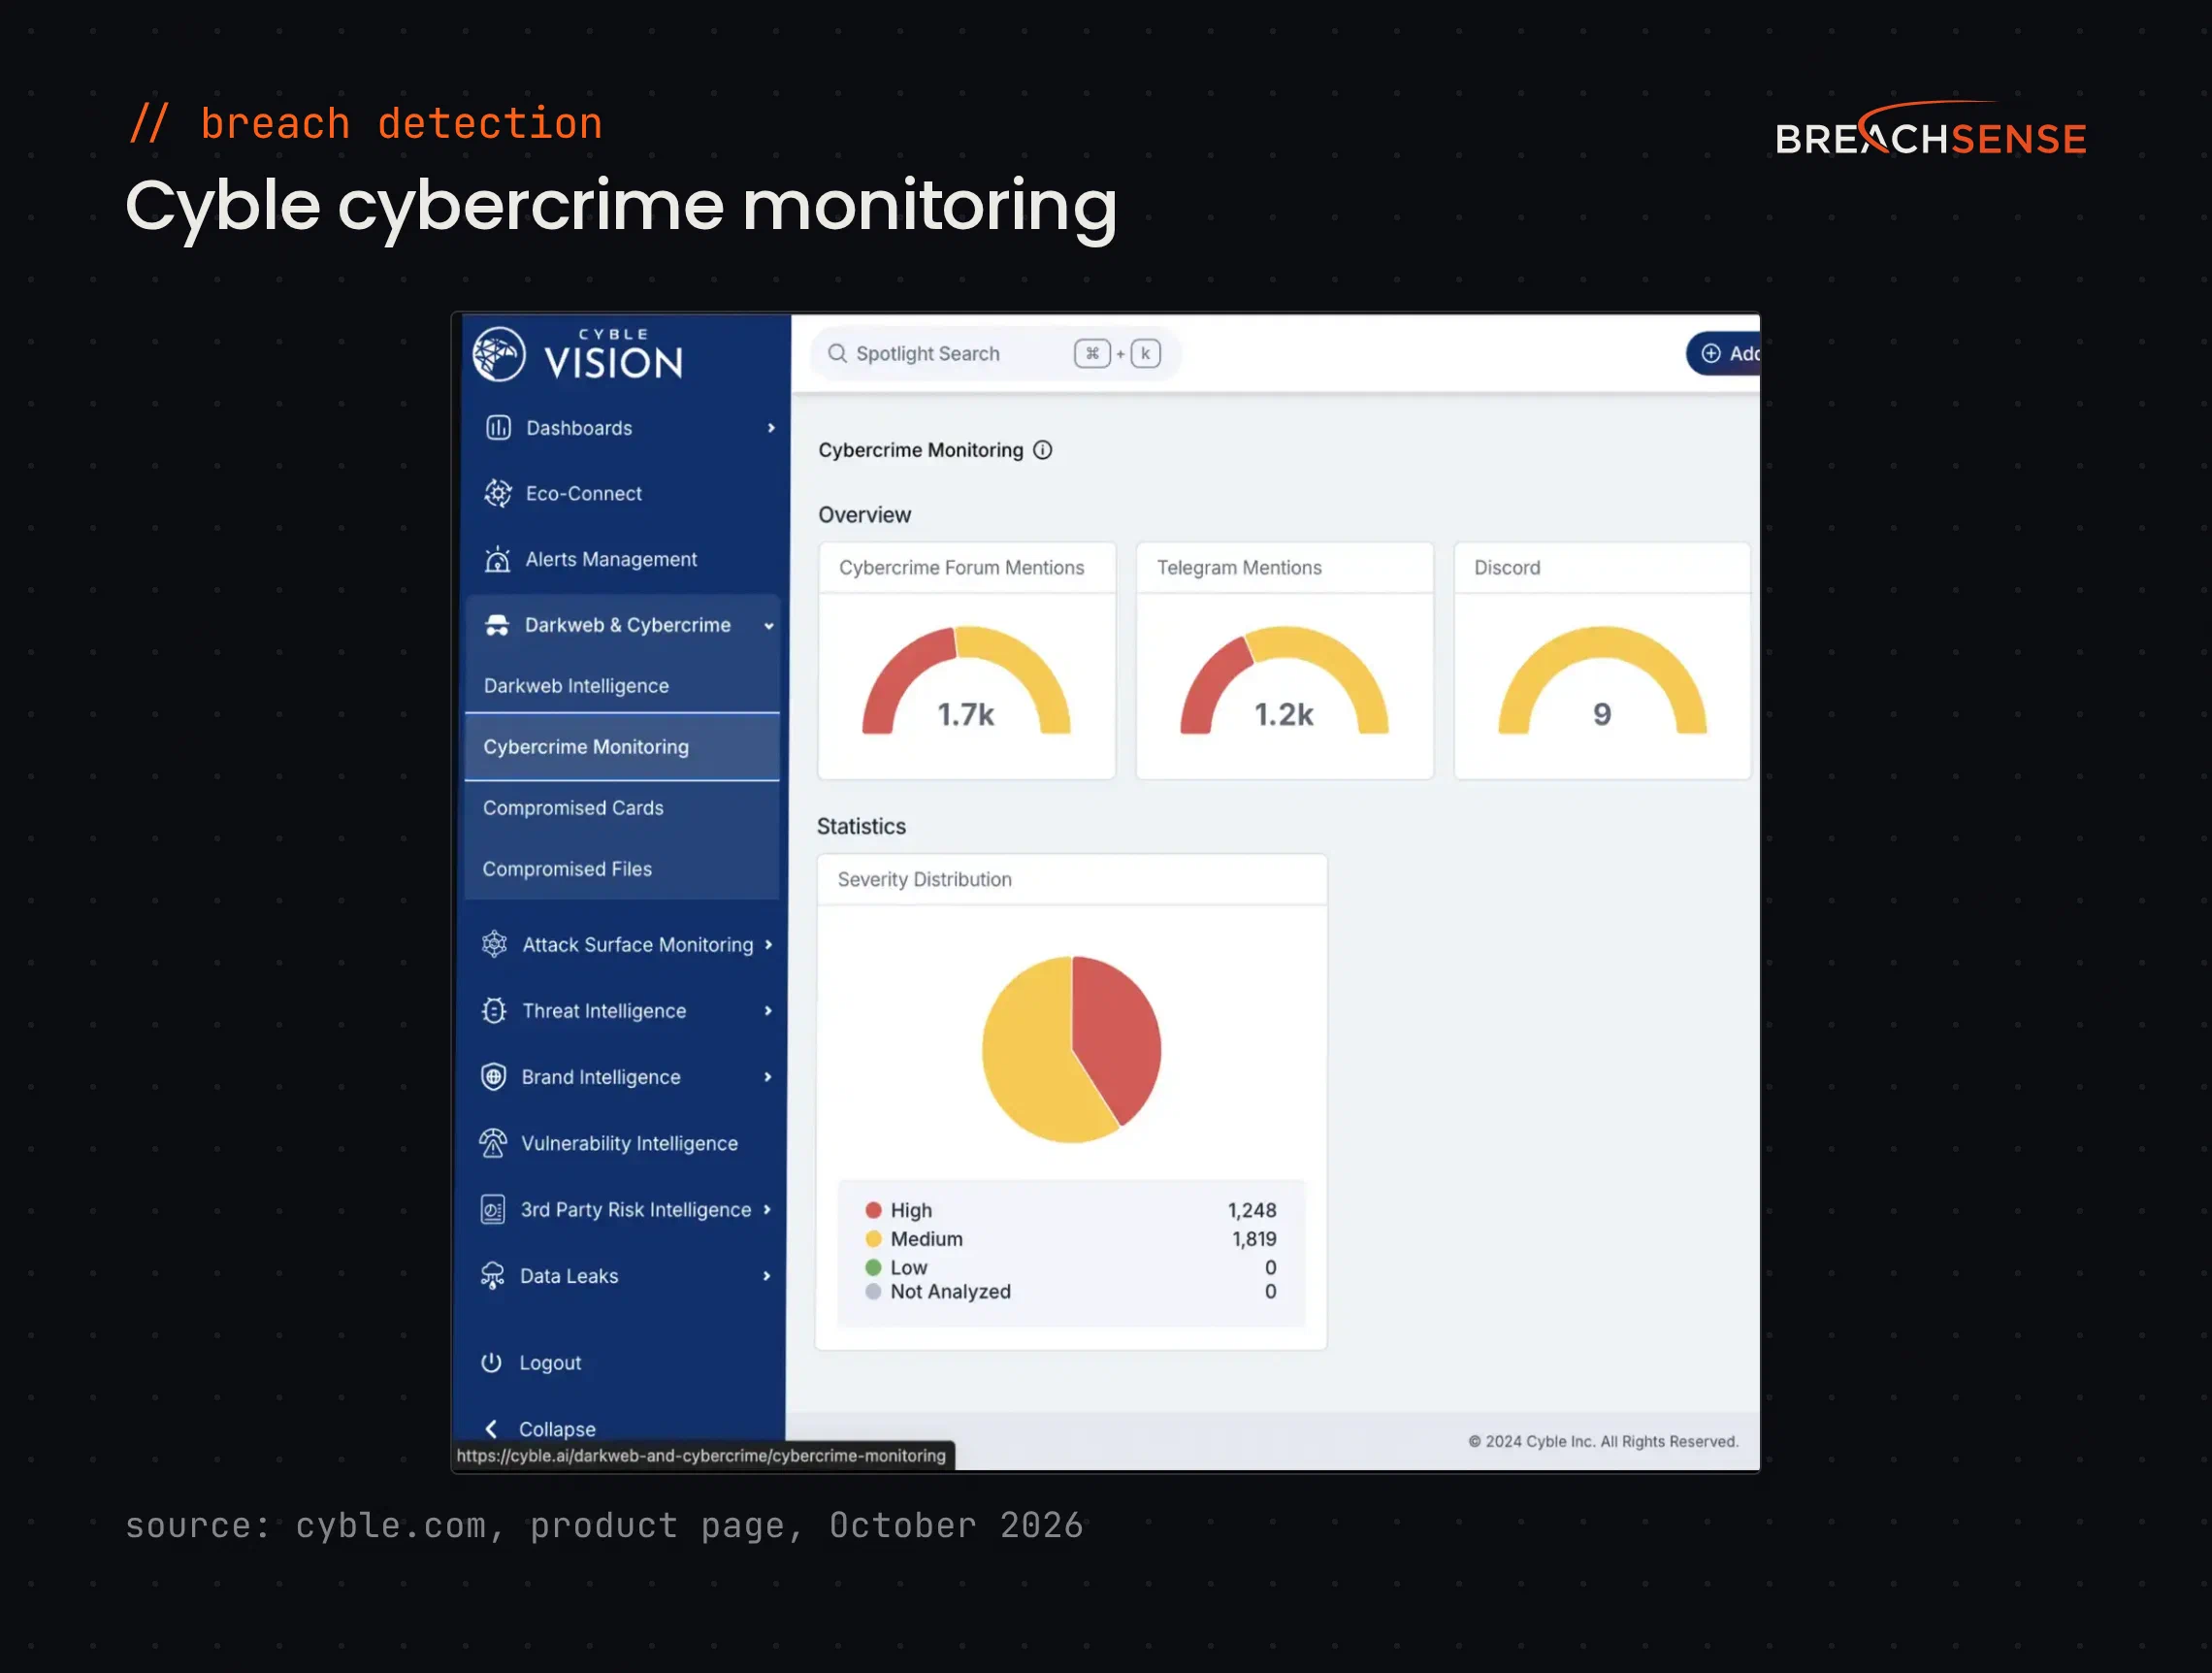
Cyble Vision is Cyble’s threat intelligence and digital risk platform, built for enterprises, governments and critical infrastructure. Cyble Vision covers dark web and credential monitoring, along with impact analysis when a third party is breached.
Cyble says Vision indexes more than 15 billion dark web records a month, and that Cyble monitored 6,046 confirmed breaches worldwide in 2025. See our Breachsense vs Cyble comparison.
Key features
- Credential alerts. Alerts you when your company’s credentials, passwords or API keys appear online.
- Ransomware leak site tracking. Monitors ransomware leak sites, cybercrime forums and credential markets.
- Third-party breach analysis. Flags breaches at your vendors and partners.
Pricing: Not published. Cyble offers a free external threat assessment report.
Rating: 4.8/5 on G2
Pros
- Dark web, deep web and social media monitoring sit in one view, alongside attack surface and brand alerts.
- The support team responds quickly and has added features customers asked for.
- The API and integrations send alerts into SIEM and SOAR tools.
Cons
- Some alerts are partial matches or false positives that an analyst has to verify.
- The interface and advanced features take time to learn.
- Reports and dashboards have limited filtering and customization.
6. SOCRadar
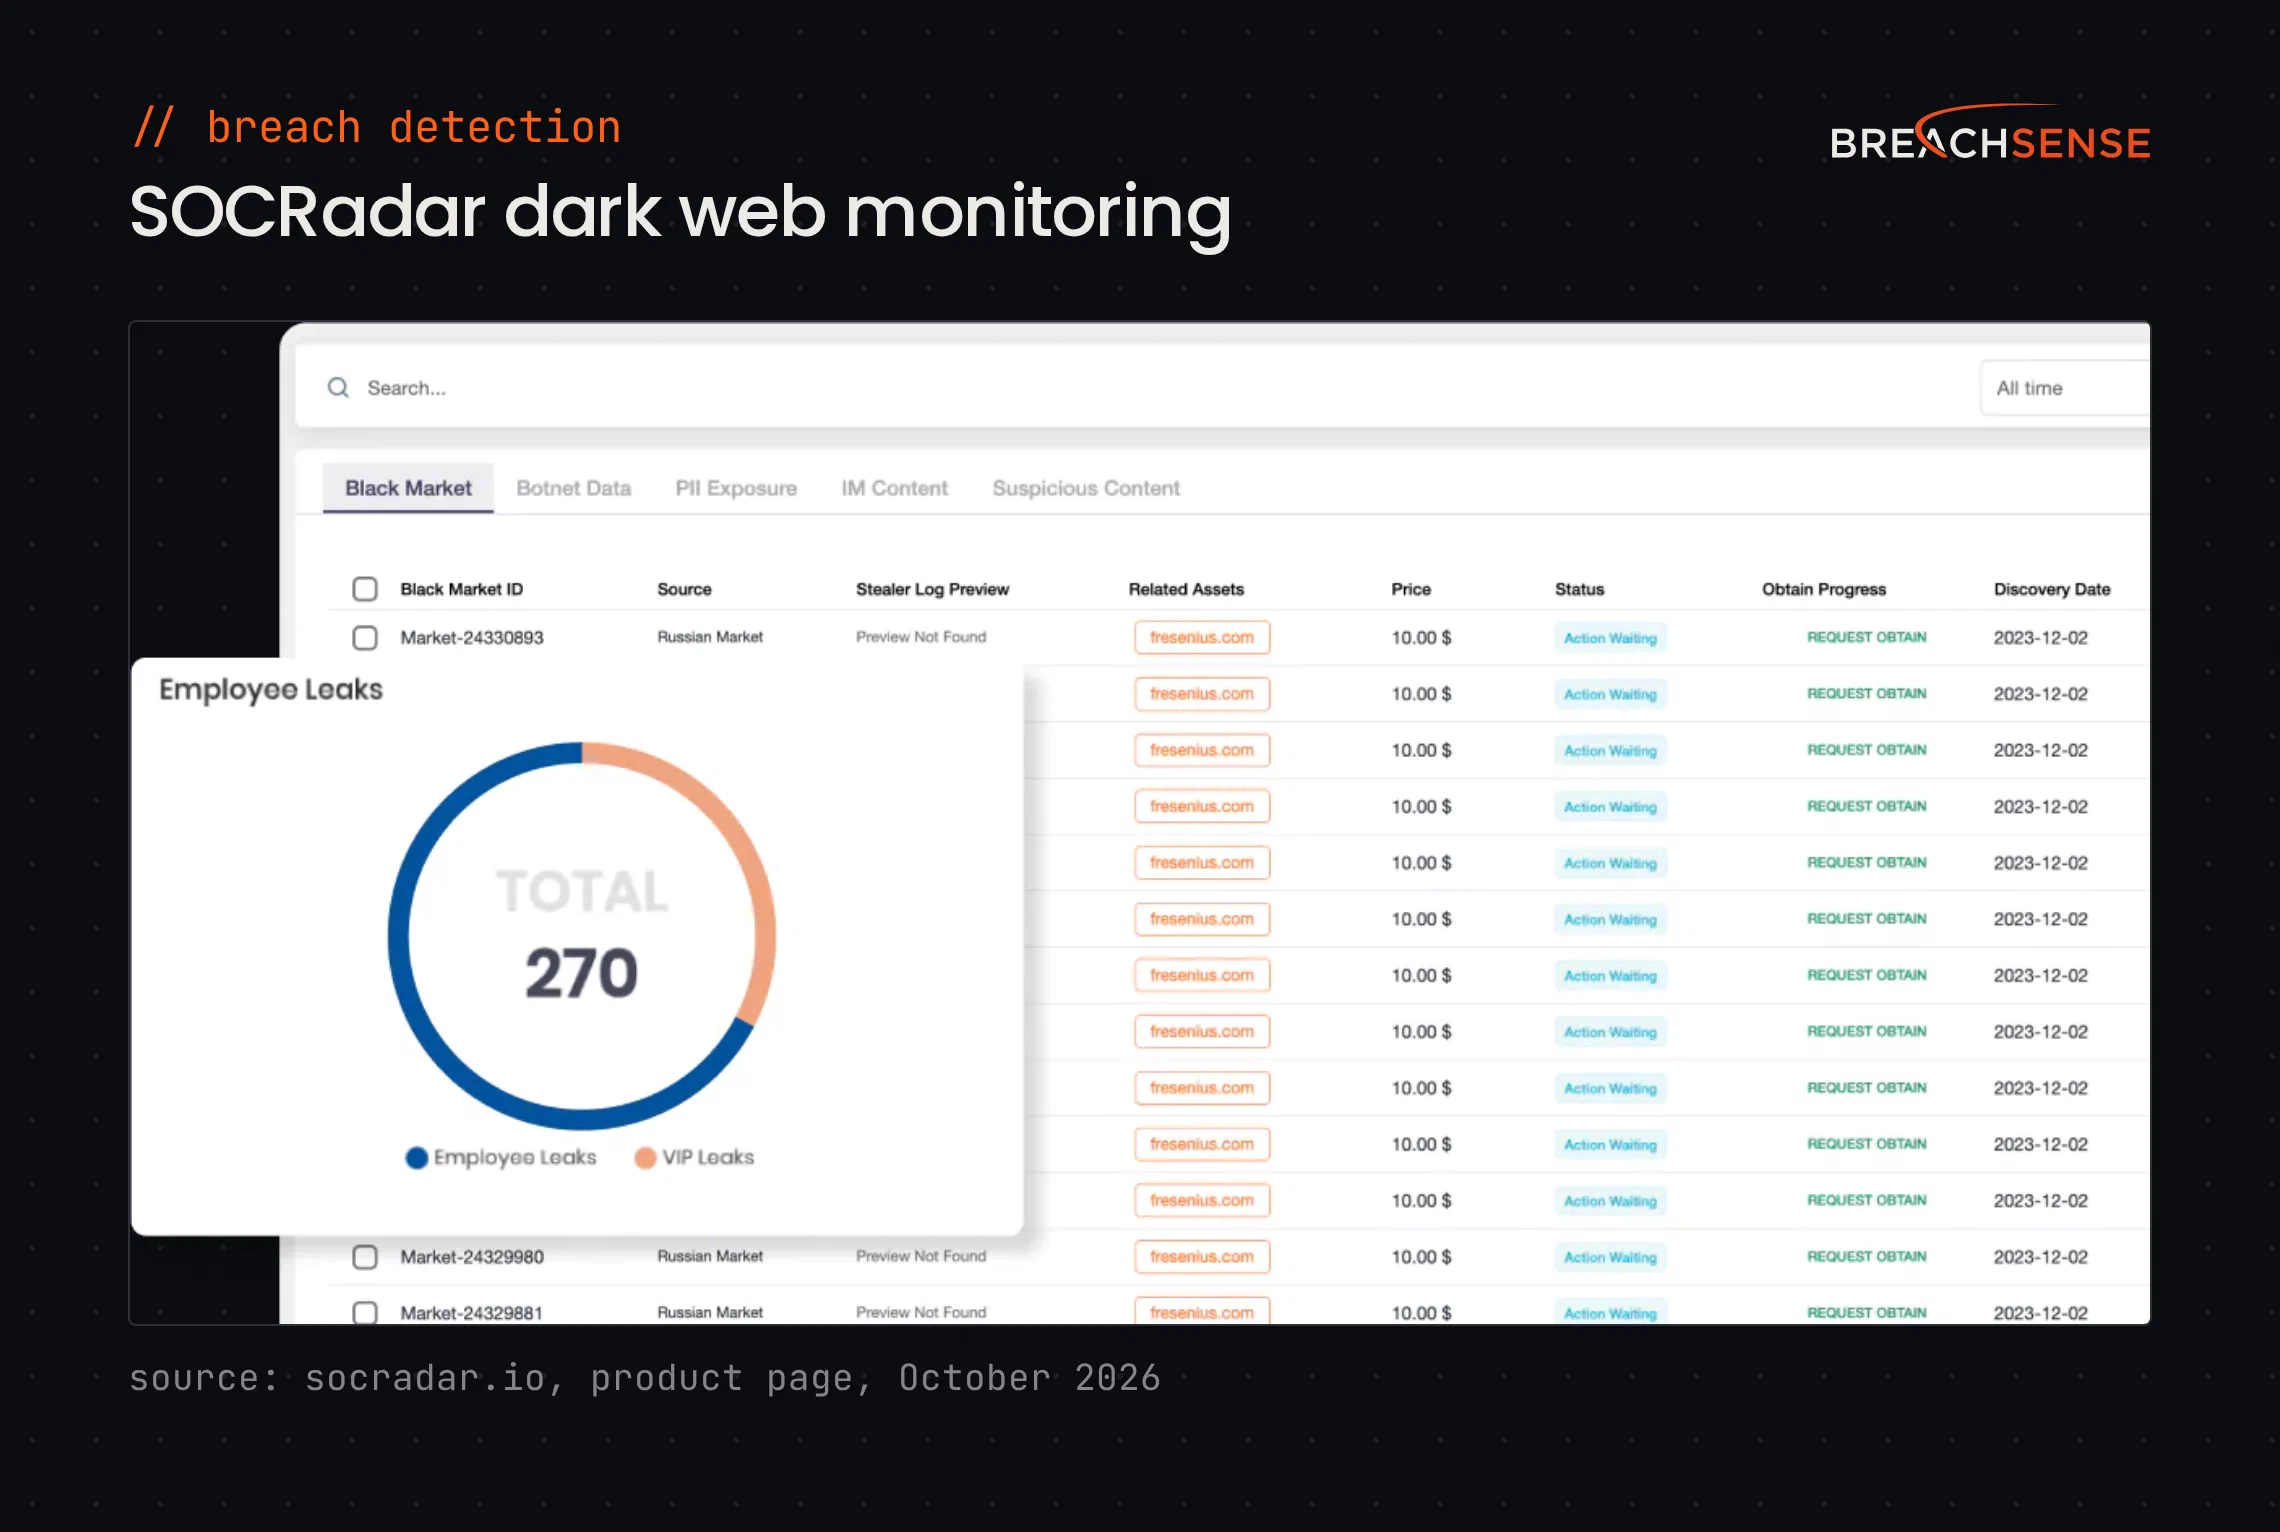
SOCRadar sells threat intelligence in modules, and its Advanced Dark Web Monitoring product is aimed at small and mid-sized companies. SOCRadar’s Essential tier is “ideal for businesses under 100 employees”, and its Business tier for 100 to 500 employees.
SOCRadar says its Supply Chain Intelligence module covers nearly 50 million vendor organizations, each assessed against 133 check items. See our Breachsense vs SOCRadar comparison.
Key features
- Stealer log tracking. Alerts you when stealer logs contain your company’s credentials.
- Personal data alerts. Alerts you when employees’ or customers’ personal data is compromised.
- Dark web search. Lets you search dark web sources by keyword, IP address, email, domain or URL.
- Vendor risk monitoring. Reports changes in your vendors’ risk scores through the Supply Chain Intelligence module.
Pricing: SOCRadar publishes prices for two of its three plans. Advanced Dark Web Monitoring costs $4,550 a year on the Essential plan and $9,100 a year on the Business plan. For an Ultimate-Flex quote, you have to contact SOCRadar’s sales team. SOCRadar offers a one-week free trial of the Business tier.
Rating: 4.7/5 on G2
Pros
- Alerts cover leaked employee and customer credentials and lookalike domains copying your brand.
- Setup is quick, and SIEM integrations are easy to connect.
- Support answers tickets fast.
Cons
- False positives and repeat alerts for credentials already reported add noise, so alert rules need manual tuning.
- Alerts are hard to work through one at a time. Related findings arrive as separate tickets, and closing an incident means leaving the alert view.
- The dashboard feels technical to new users until they learn where each module sits.
7. CrowdStrike Falcon Adversary Intelligence
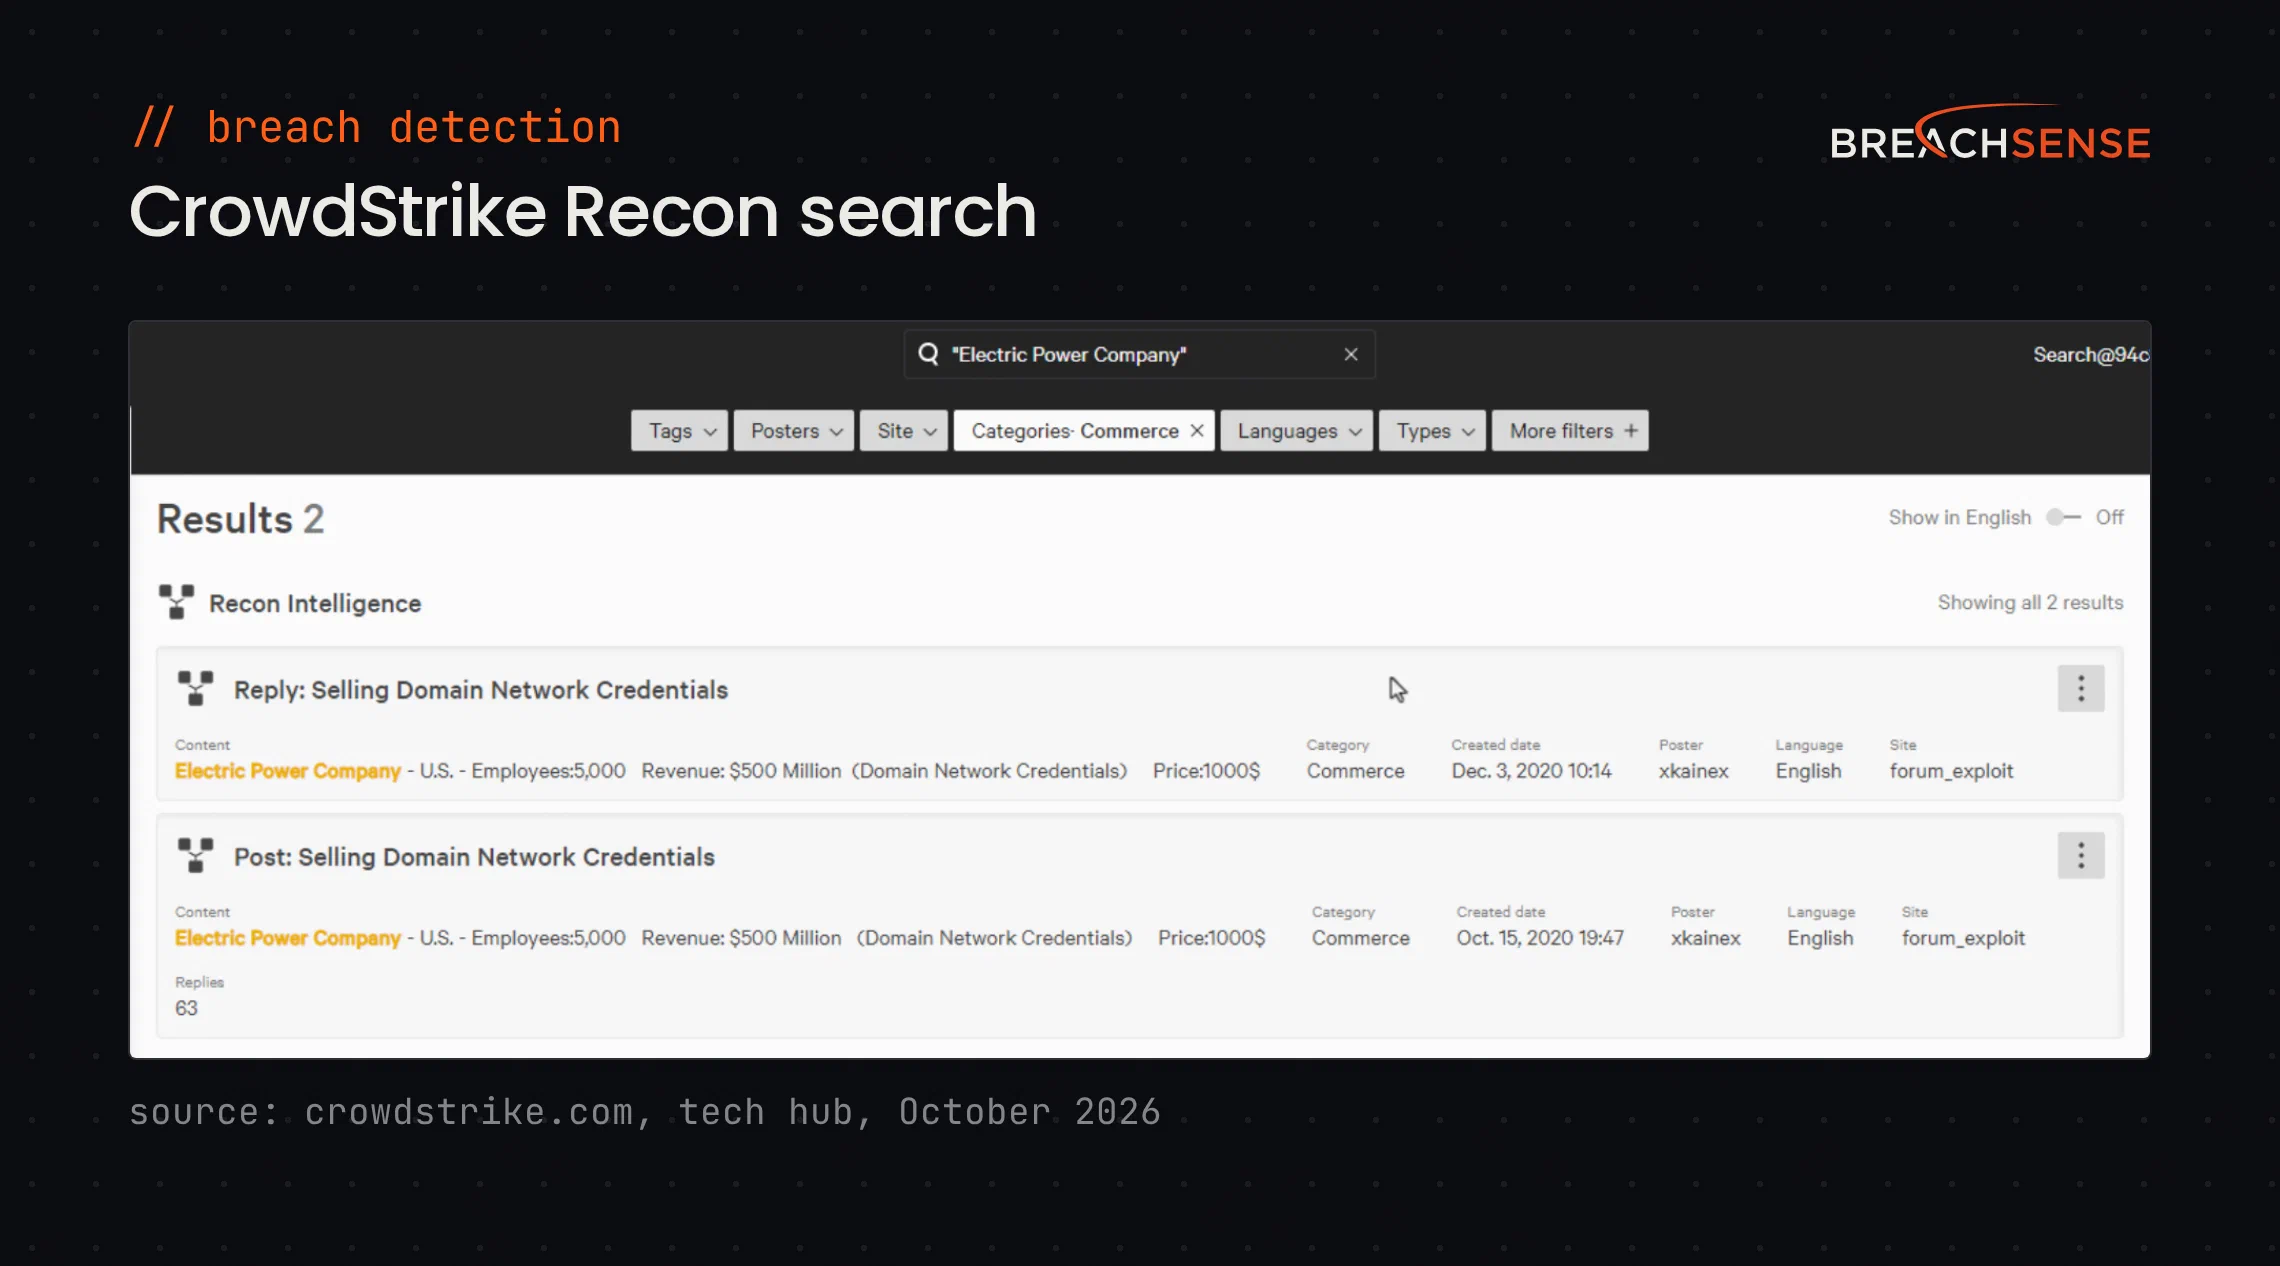
Falcon Adversary Intelligence is CrowdStrike’s threat intelligence module. CrowdStrike’s Recon feature monitors the open, deep and dark web for threats to your brand and employees. Falcon Adversary Intelligence suits SOC teams already running CrowdStrike Falcon.
CrowdStrike says Falcon Adversary Intelligence profiles more than 290 attacker groups. Recon covers criminal forums, marketplaces, paste sites (sites where anyone can post text anonymously) and messaging apps.
Key features
- Leaked credential discovery. Finds compromised credentials and stolen data, including your customers’ data, on underground markets and forums.
- Forced password resets. Sends exposed passwords to Falcon Next-Gen Identity Security, a separate module, which forces a password change.
Pricing: CrowdStrike doesn’t publish a price for Falcon Adversary Intelligence. CrowdStrike’s 15-day free trial covers its endpoint products. You can request trials of other products through the CrowdStrike Store.
Rating: 4.7/5 on Gartner Peer Insights
Pros
- Detailed profiles of nation-state groups, cybercrime gangs and hacktivists.
- Works smoothly with the rest of the Falcon platform.
Cons
- Licensing and add-ons push up the total cost.
- Reports and dashboards feel rigid.
8. Google Threat Intelligence
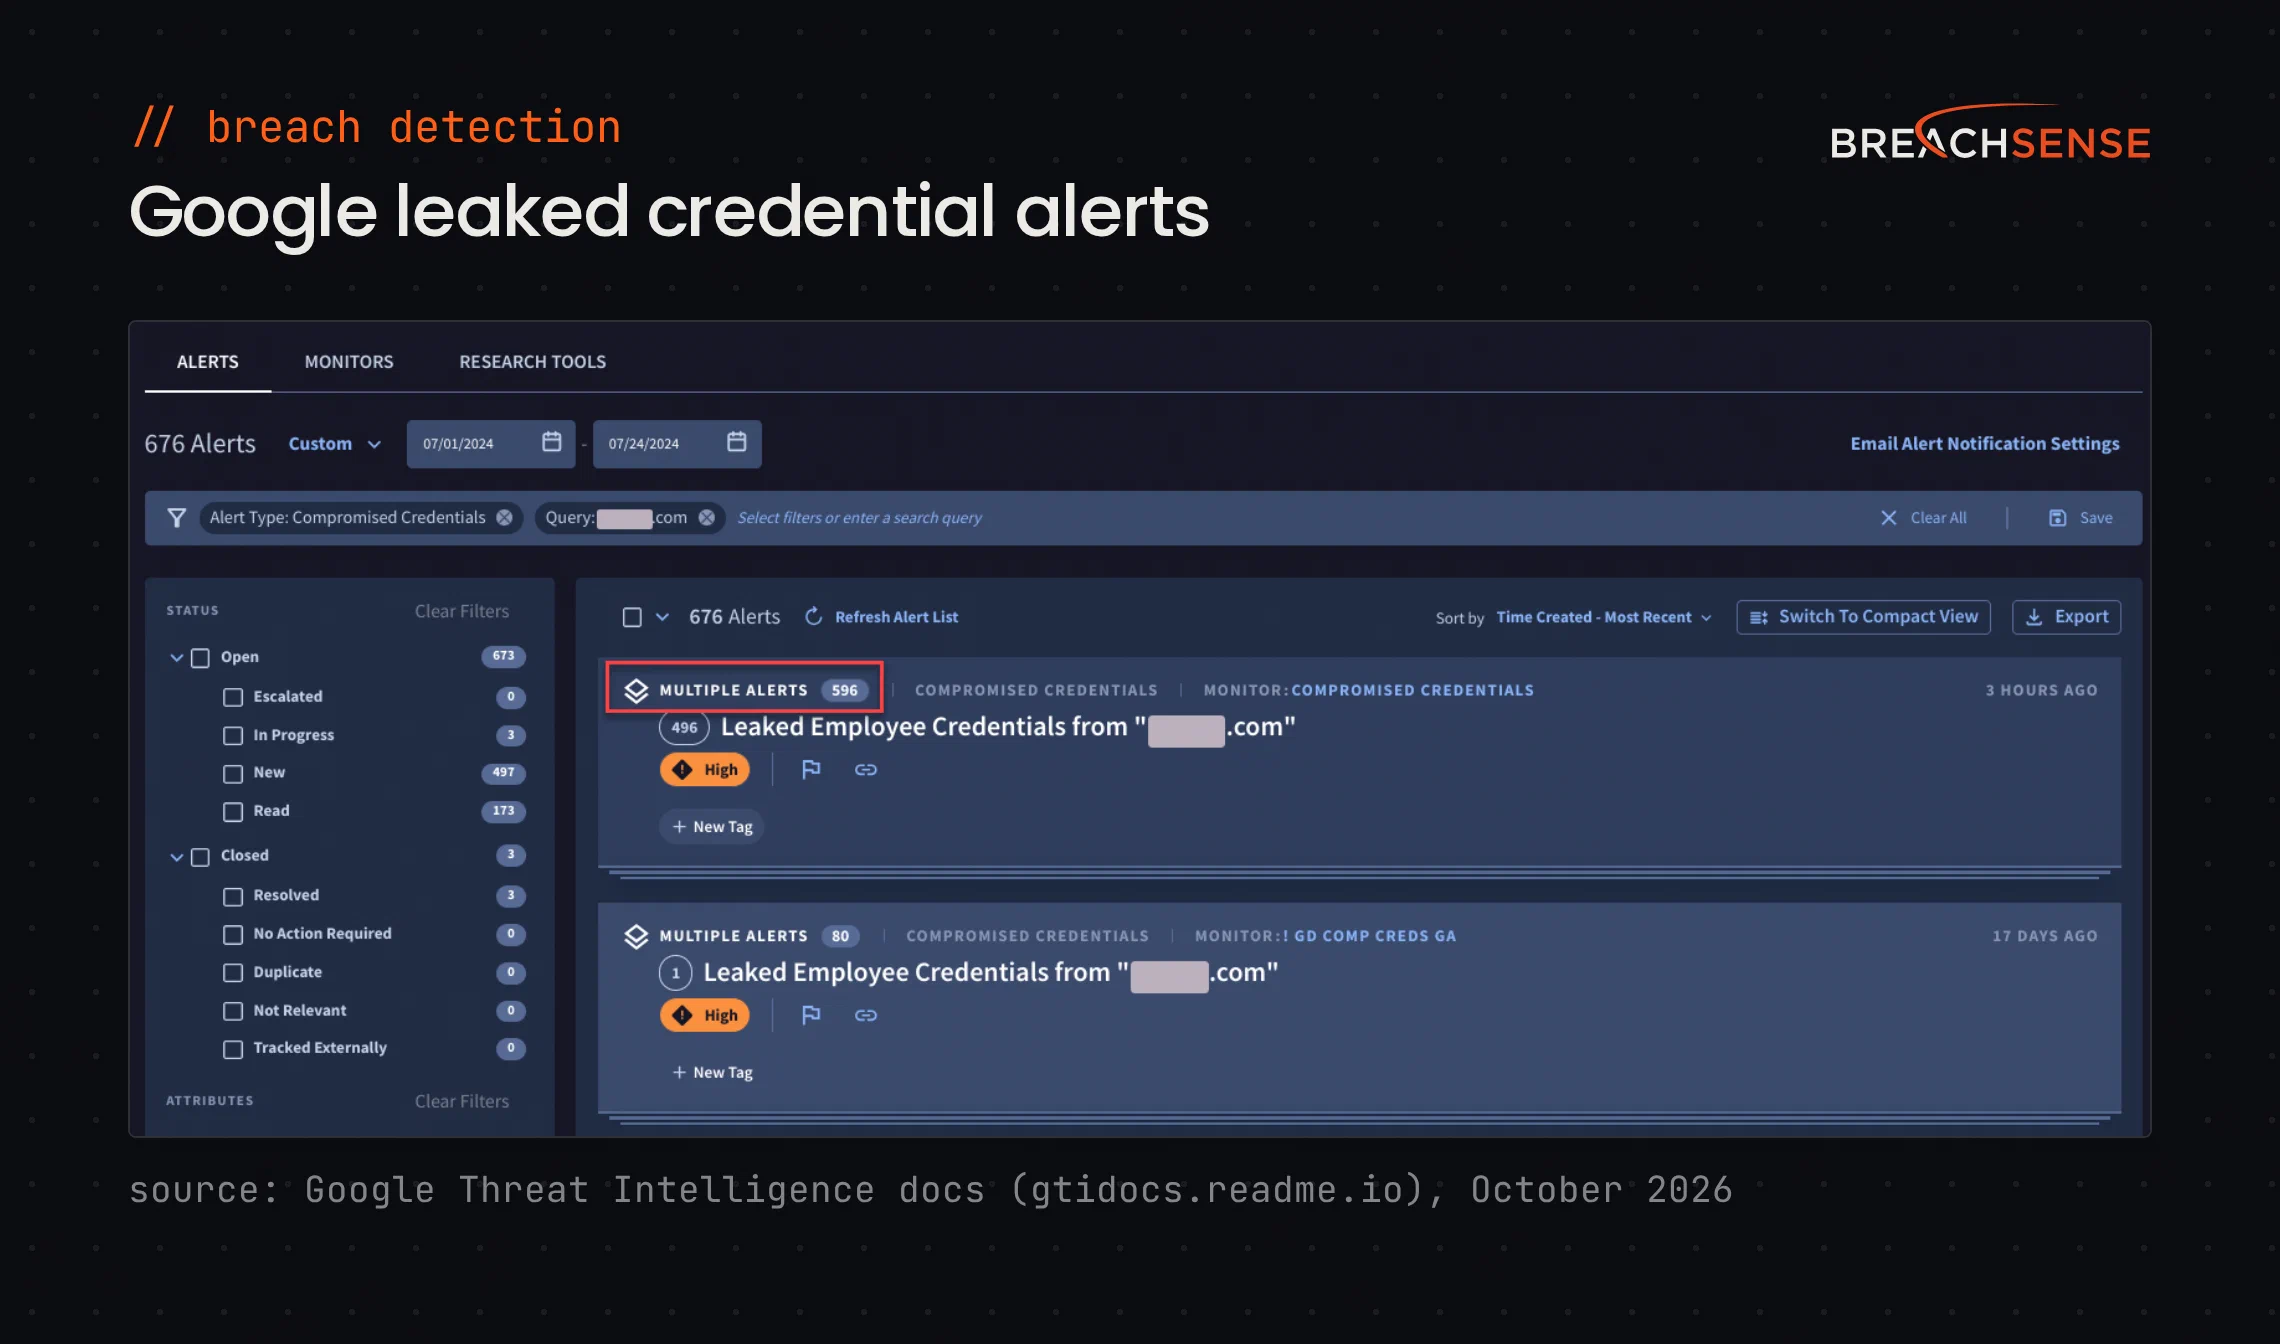
Google Threat Intelligence combines Mandiant’s research with VirusTotal data. Its Digital Threat Monitoring (DTM) feature watches the dark web for your company’s data. DTM comes only with the Enterprise and Enterprise+ tiers, which Google aims at teams that hunt for threats or run their own threat intelligence program.
Google’s documentation says DTM monitors more than 200 sites, including carding forums (where stolen payment cards are sold) and ransomware leak sites.
Key features
- Compromised credential alerts. Alerts you when employee or customer accounts linked to your company appear in compromised credential data.
- Unmasked passwords for verified domains. Shows full credential details once you prove you own the domain.
- Vendor monitoring. Flags mentions of your vendors on underground markets, paste sites, forums and blogs.
- Analyst triage. With the Managed Digital Threat Monitoring service, a designated Mandiant analyst triages and prioritizes alerts for you.
Pricing: Not published. Google sells Standard, Enterprise and Enterprise+ subscriptions at a flat annual rate, each with a set number of API calls. Google’s product pages don’t mention a free trial.
Rating: 10/10 on TrustRadius. TrustRadius reviews date from 2021 to 2023 and cover Mandiant Advantage, which Google later folded into Google Threat Intelligence.
Pros
- The API is easy to connect to other security tools.
- Reports on threat actors and their techniques give analysts context for an investigation.
- Vulnerability intelligence includes expert analysis of each CVE.
Cons
- Feeds and alerts are hard to tune to your own environment.
- With so many features, new analysts take a while to find the ones they need.
- Support is slow on non-critical cases and analysis requests.
9. Hudson Rock
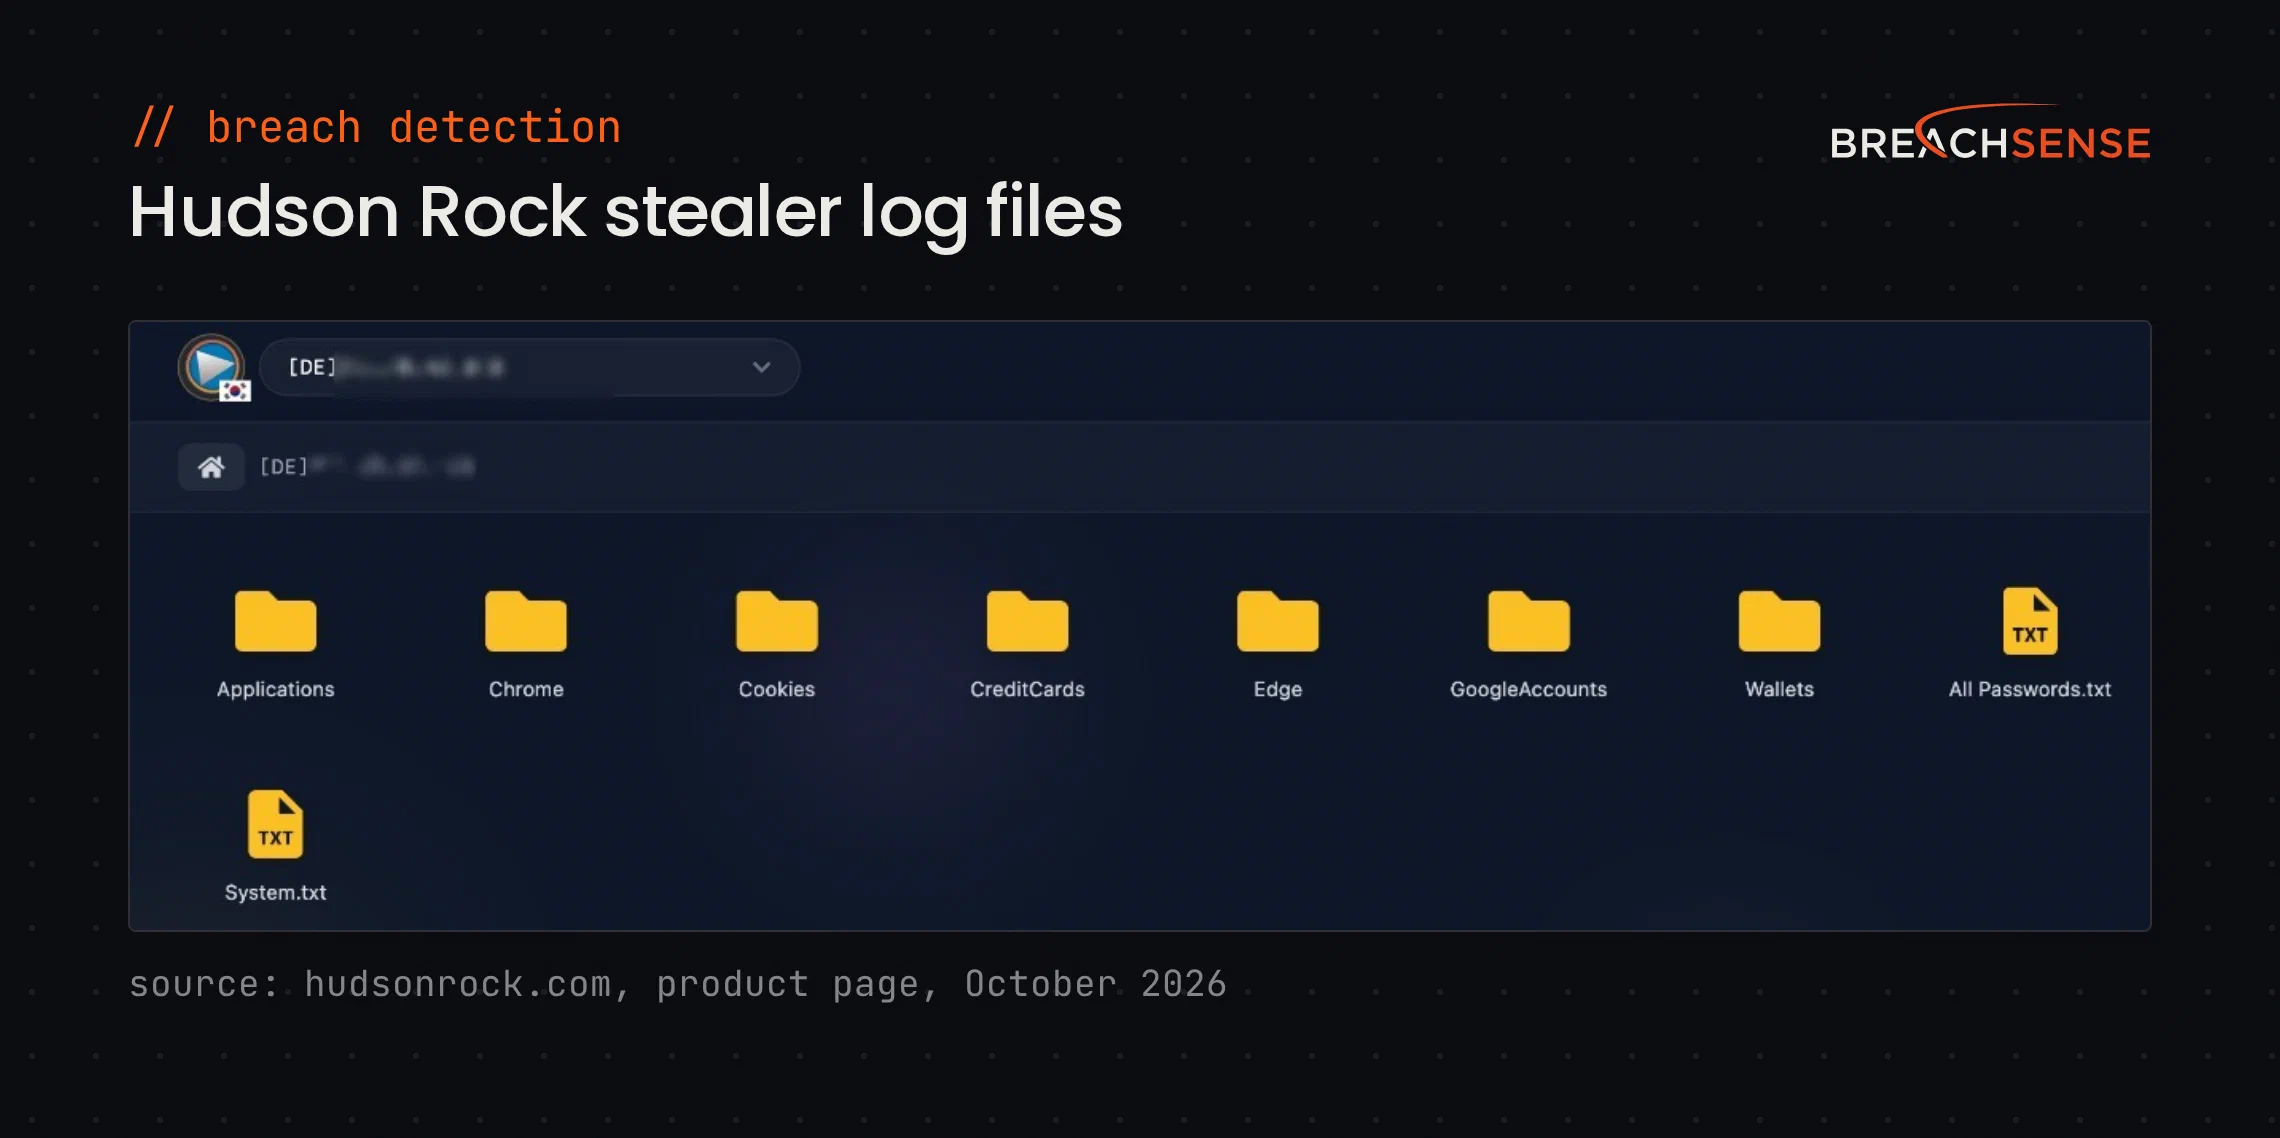
Hudson Rock builds its Cavalier platform on infostealer data. Hudson Rock sells Cavalier to security teams, cyber insurers, third-party risk providers and MSSPs (managed security service providers). Cavalier shows which of your employees, customers and partners had credentials stolen from infected machines.
Hudson Rock’s homepage counts more than 36.8 million compromised machines in its data as of October 2026. See our Breachsense vs Hudson Rock comparison.
Key features
- Domain search. Lists compromised employee, customer and third-party credentials tied to your domain.
- Account response. Terminates active sessions and disables compromised accounts through Active Directory, Okta or Auth0.
- Supply chain monitoring. Flags partner employees who sign in to your services from infected machines.
- Alert delivery. Sends alerts by email, Slack, Splunk or custom webhook.
Pricing: Not published. A free Hudson Rock account tracks up to three emails, three domains and three usernames.
Rating: Not enough reviews on G2.
Selection criteria
How we evaluated these tools
We compared each tool on five points, using each vendor’s own site for features and pricing:
- Sources covered. How many of the four sources the tool collects from (stealer logs, breach dumps, forums and ransomware leak sites).
- What an alert includes. Whether you get a plaintext password with its source and first-seen date, or only a password hash.
- How you get alerts. Webhook, API, a SIEM integration or a dashboard you log in to.
- Vendor breach coverage. Whether the tool tells you when a vendor is breached, and which of your records were in the leaked files.
- A trial on domains you choose. Whether you can trial the tool on any domain, including your clients’ domains if you’re an MSSP.
Ratings, pros and cons come from the review site named in each entry, checked in October 2026.
How to choose a tool
To catch an attacker already inside your network, you need EDR, XDR or a SIEM. The tools on this list find your data after it has leaked.
- Your employees’ passwords and session cookies? Ask whether alerts include the plaintext password or only a password hash. Only a plaintext password lets you check whether that password is still in use.
- Your vendors’ breaches? Ask whether the tool indexes the leaked files themselves or only lists which companies were breached. Breachsense indexes the files, so you can search them for any term, such as your company name or an executive’s name. A vendor risk score comes from a scoring company that lacks the context to judge leaked data. The scoring company can’t tell whether a leaked password still works, or whether the vendor already reset it. In the demo, ask which leaked records the score counts, so your team can judge the risk itself.
- Attackers and campaigns aimed at your industry? Shortlist the threat intelligence platforms above. These platforms also send reports on attacker groups targeting your industry. Ask each vendor whether its analysts will flag the reports that affect your company, or whether you need your own analyst.
- Where should alerts go? If your team works from a SIEM or ticketing system, ask whether the tool sends alerts by webhook or only shows alerts in a dashboard you log in to.
In every demo, first ask the vendor to name the sources it collects from, for example the actual forums and Telegram channels. An answer like “dark web forums” doesn’t tell you which forums, or how many. Second, ask the vendor to run a live search on your domain or a client’s, and show the date each record was first found. Compare the newest record with what the other vendors you’re testing find. A vendor whose newest record is months behind the others is slow to add new leaks. For more credential-focused options, see our credential monitoring tools.
Check what’s already leaked before you choose a tool
Run a free dark web scan on your domain. The scan gives you a list of your company’s leaked credentials. Compare that list with what each tool on your shortlist finds for the same domain. Then book a demo to search vendors’ leaked files for your company’s data.