Trusted by enterprise security teams
PwC Trustwave Teachers Mutual Bank Swire Shipping Defense.com

What Breachsense Monitors for Early Signs of Ransomware

  • Stolen credentials in infostealer logs. Passwords, session cookies, and VPN credentials harvested from infected employee devices. We index new stealer logs within hours. Stealer logs can also include API keys, which don’t prompt for MFA when used.
  • Credentials from phishing kits, combo lists and third-party breaches. We send an alert when one of your employees’ passwords shows up in any of them.
  • Initial access broker listings and other posts on hacker forums. Network access bundles priced by access level. We send an alert when your domain shows up in a forum post.
  • Leak sites for 100+ active ransomware groups. We send an alert when a domain on your watchlist shows up in one of their posts. Some groups hide the victim’s name. You can still search the files they publish for your company’s data.
  • Vendor and supply chain exposure. Add your vendors’ domains to your watchlist to get an alert when a vendor shows up on a leak site.
  • Session token theft that bypasses MFA. Stealer logs include browser cookies. You choose which session cookies to monitor. Each alert shows when the cookie expires.
  • RESTful API and webhooks. We send alerts to your SIEM or SOAR by webhook. Your own playbooks can then reset passwords and revoke session tokens.

The Early Warning Alerts Breachsense Sends

Reset Credentials Before They’re Used

Breachsense sends an alert when your domain shows up in a new stealer log. The alert also includes the infected computer’s name and IP address when the stealer log records them. Clean or reimage that computer first. Then reset the leaked password and revoke the employee’s session tokens.

Find Broker Posts Selling Access to Your Network

Initial access brokers verify and resell stolen credentials on criminal forums. If someone’s selling access to your network and your domain shows up in the post, Breachsense sends an alert.

Monitor Leak Sites for You and Your Vendors

Full-text search across files leaked in ransomware attacks, third-party breaches and unsecured databases. Search for your company’s data, such as your domain or an employee’s name, even in files from a vendor’s breach.

What a Ransomware Leak Site Alert Tells You

We send an alert when a ransomware group adds a company on your watchlist to its leak site. That company can be your own, a client or a vendor. If you’re an MSP (managed service provider), you can send each client’s alerts to that client’s own inbox or webhook.

Each leak site alert includes:

  • The domain on your watchlist that matched
  • The victim’s company name, as the group posted it
  • The ransomware group that made the post
  • The date we found the post
  • A link to the post on the leak site

Our API documentation describes each of these fields.

Some alerts also include a link to a screenshot of the post. The post can include samples of the stolen files, such as employee records or contracts. If the victim doesn’t pay, the group often publishes everything it stole.

When a vendor is breached, the leak site post usually mentions only the vendor. The stolen files can still include your data. Add your vendors’ domains to your watchlist, so you get an alert when a group lists one of them.

To find your data inside a vendor’s leaked files, add your company’s name to your watchlist as a term. To match an exact phrase, put it in double quotes. When that term shows up inside a vendor’s leaked file, we send an alert with the file’s URL. You can also search the leaked files for other company data, such as an employee’s name.
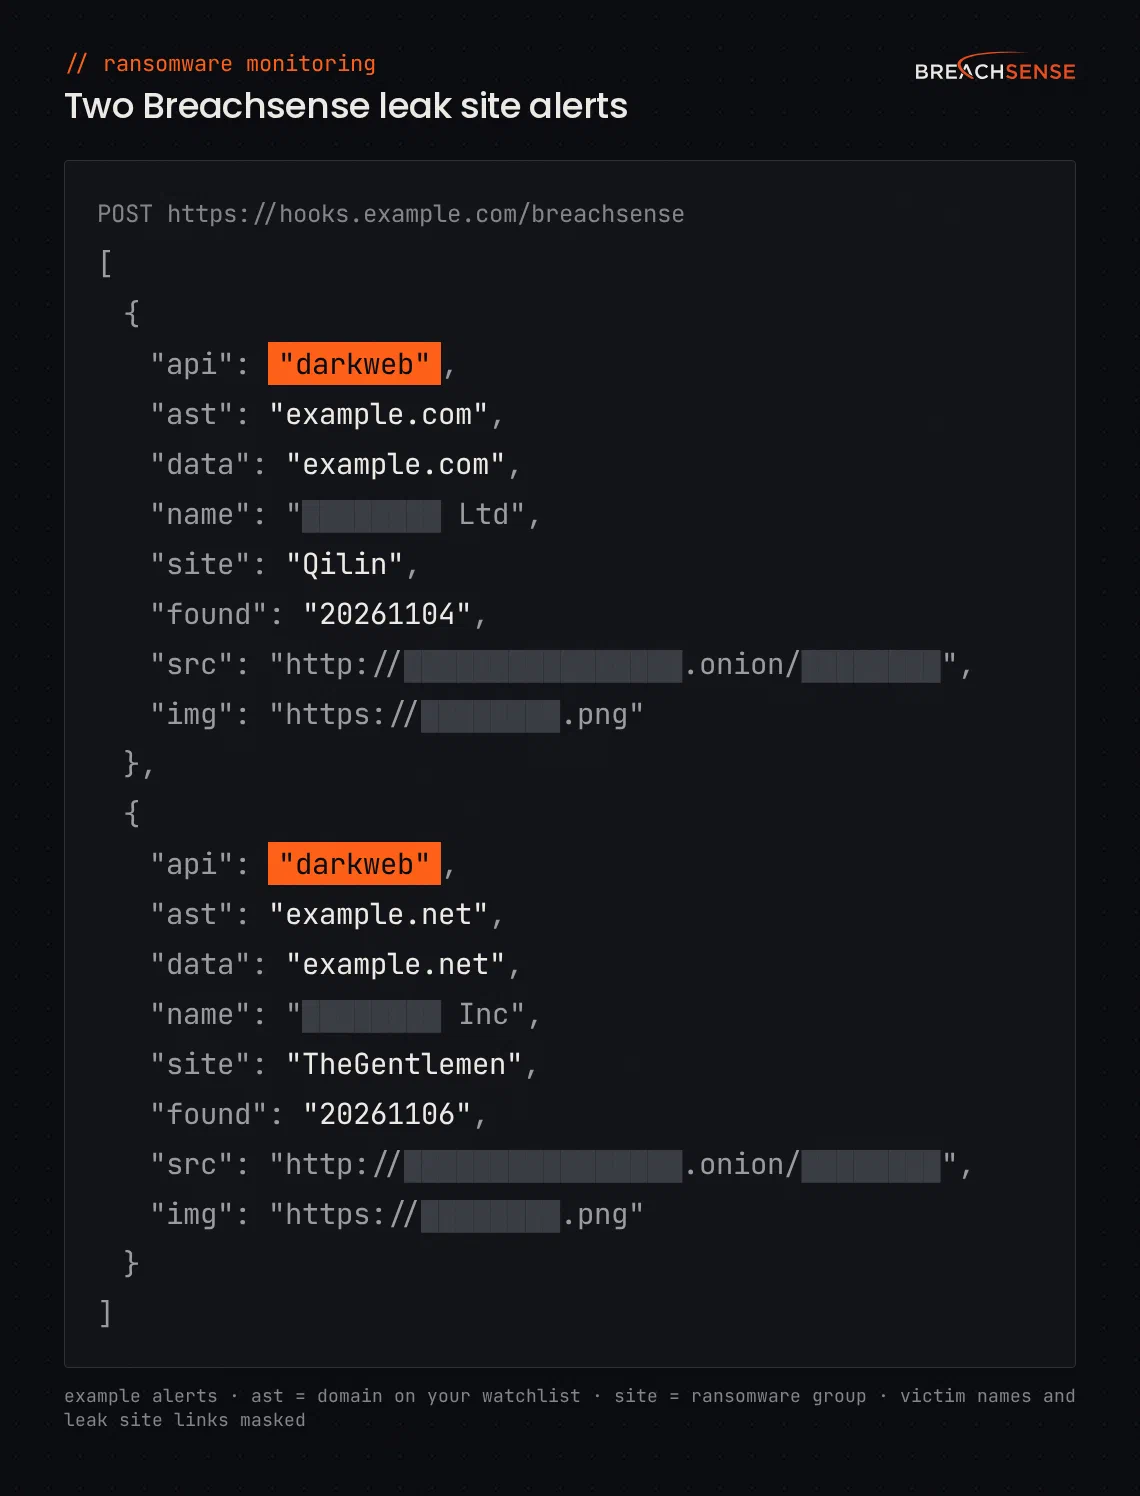
Example Breachsense webhook alert in JSON for two ransomware leak site posts, showing the endpoint, the monitored domain that matched, the victim's domain, a masked company name, the ransomware group, the date found and a masked link to the leak site post and a masked screenshot link

Track Ransomware Groups and Their Victims

Breachsense publishes a public ransomware intelligence page for each group we track. Each page shows the group’s victims, the industries it targets and the countries the victims are in. It also shows how many victims had employee credentials leak in the 12 months before the group’s leak site post.

Each page also lists the group’s recent victims, with each victim’s sector, country and posting date. See TheGentlemen’s and Qilin’s pages for examples. Use the industry and country breakdowns to see which groups target companies in your sector and region.

After a leak site alert about a vendor, check the group’s page. It shows which industries the group targets and its other recent victims.

You can browse every ransomware group we track. For the latest victim counts across all groups, read our monthly ransomware reports. Each report lists the month’s most active groups. It also shows the industries and countries their victims were in.

Add your own, your clients’ and your vendors’ domains to your watchlist. We send an alert when a group lists one of those companies as a victim.
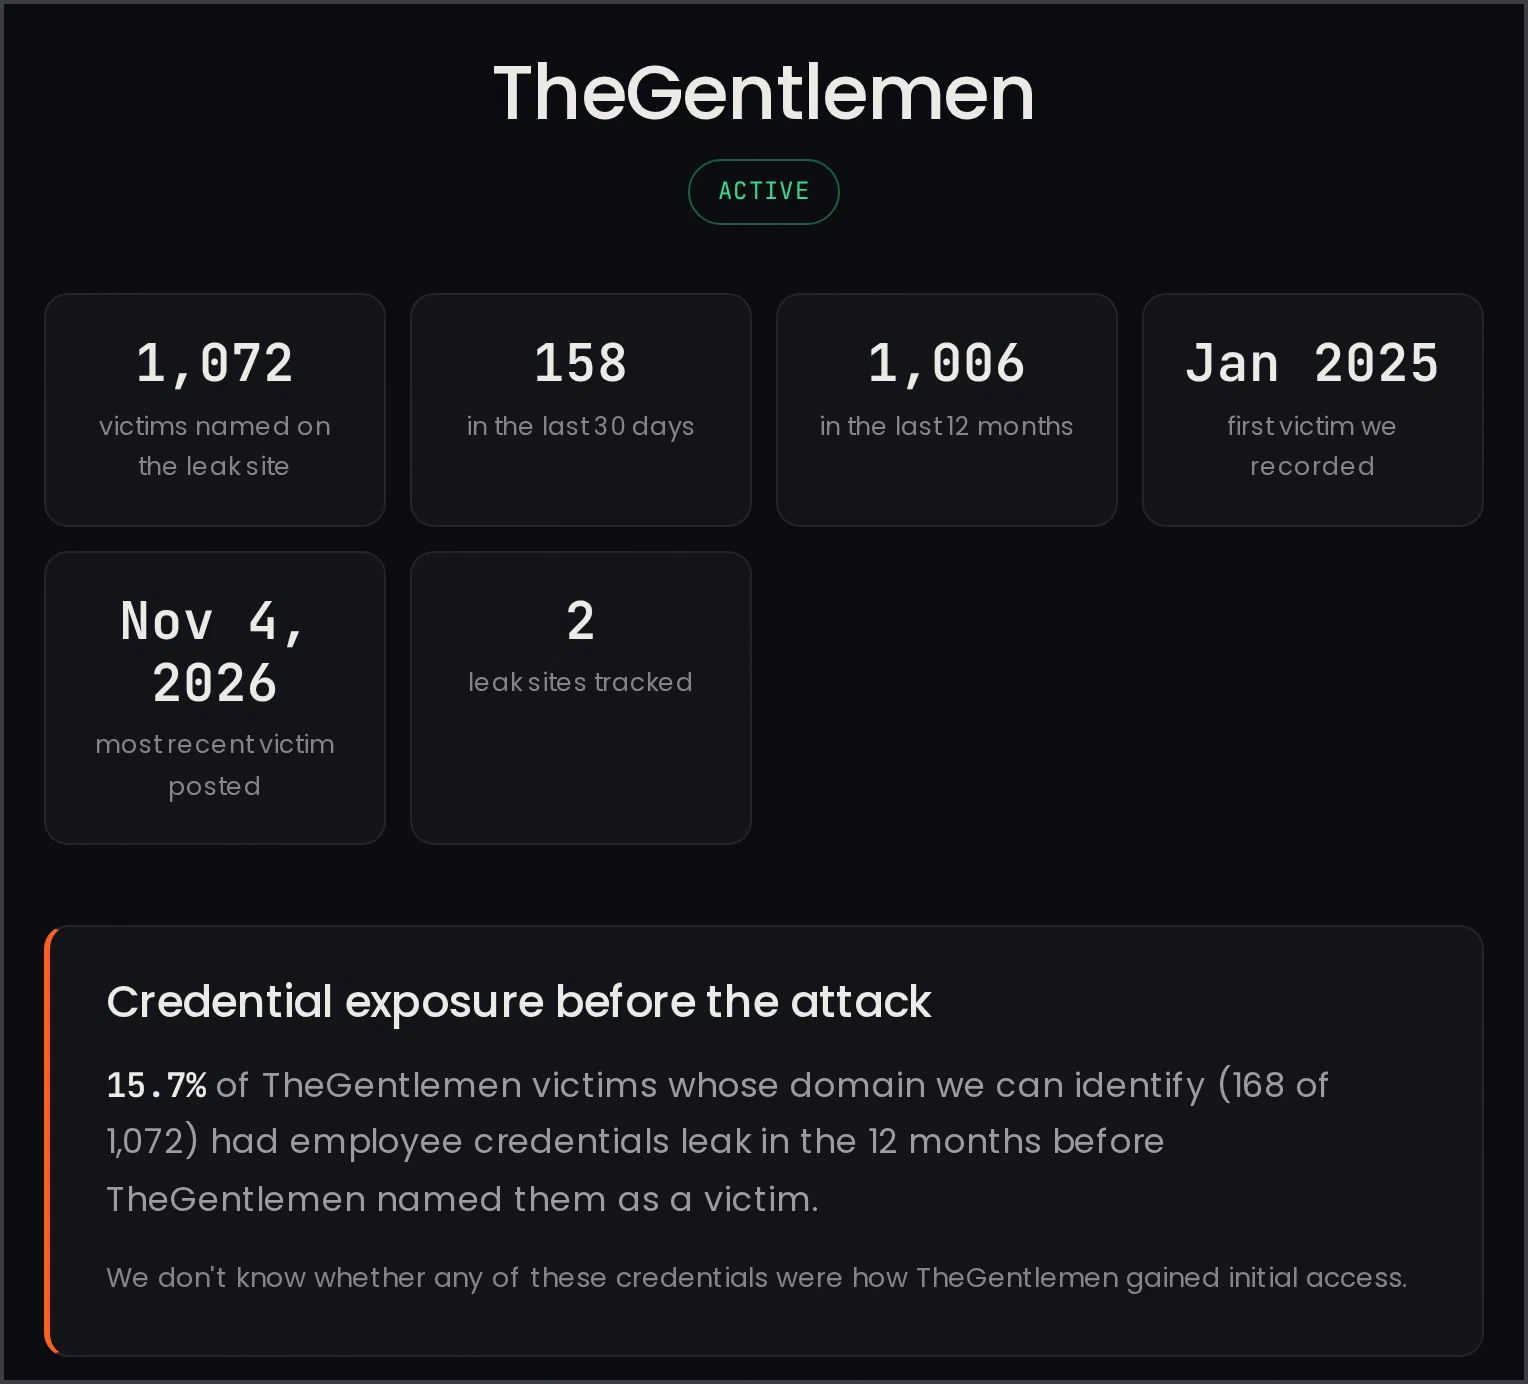
Top of Breachsense's public ransomware intelligence page for TheGentlemen, showing victims listed on the leak site, victims in the last 30 days and last 12 months, the first and most recent victim dates, and the share of victims with leaked employee credentials
Source: breachsense.com, November 2026

The Ransomware Kill Chain and Its Early Warning Signs

Ransomware grew to 48% of all breaches in Verizon's 2026 DBIR, up from 44% the year before. Dark web monitoring can warn you during steps 1 to 4, before the attacker deploys ransomware.

  • Step 1

    Credential theft on an endpoint

    Infostealer malware on an employee device harvests browser passwords, VPN credentials, and session cookies. The credentials get pushed to the malware operator's server within hours. EDR sometimes catches the infection. It can't tell you where the stolen credentials end up.

    Breachsense catches:
    Infostealer log appearanceSession cookie exposure
  • Step 2

    Credentials sold in bulk

    Stealer logs appear on Telegram channels and dark web marketplaces.

    Breachsense catches:
    Bulk dump indexingTelegram channel coverage
  • Step 3

    Network access listed on broker forums

    Brokers check which credentials still work. They price access by privilege level, then list it on criminal forums.

    Breachsense catches:
    Access broker listingsCompany-name mentions
  • Step 4

    Ransomware operator buys access

    An operator buys the access and logs in using valid credentials. If the broker also sold a stolen session cookie, the operator signs in without an MFA prompt. From here they spend time mapping your network and locating backups before they deploy.

    Breachsense catches:
    Forum chatter about target
  • Step 5

    Encryption and extortion

    The attacker steals your data. The attacker deploys ransomware. The leak site countdown begins. EDR is built to catch the encryption.

    What's left:
    Leak site monitoringIncident responseresponse playbook

How Ransomware Monitoring Works

Configure Your Assets

Add your domains to your watchlist by API, plus your clients’ and vendors’ domains. Each domain covers its subdomains and every email address at that domain. You can also add any search term, such as your company’s name or a project code name.

We Watch the Dark Web

We index new stealer logs within hours. We also collect new posts from ransomware leak sites and from the hacker forums where brokers sell network access.

Get Early Warning Alerts

We send an alert when a watchlist item shows up in leak site posts, forum posts or leaked files. We also send alerts for your employees’ leaked passwords, by email or webhook.

Reset Credentials Fast

Your team, or your own automation, cleans the infected computer and resets the leaked password. Revoke the employee’s session tokens too, because a stolen session cookie can still work after a password reset.

Frequently Asked Questions

Ransomware monitoring is the tracking of ransomware leak sites, stealer logs and access broker forums for your company, your clients and your vendors. Some ransomware groups buy network access from initial access brokers. Brokers often get the passwords they sell from stealer logs. If you reset a leaked password before a broker sells access, the buyer can’t sign in with it. If the stealer log included session cookies, revoke that employee’s session tokens too.
EDR monitors your endpoints. SIEM correlates logs from your systems. Both mostly catch attackers once they’re inside. Ransomware monitoring covers the dark web sources where attackers buy network access. It catches the warning signs often weeks or months before an attack.
The four sources that matter most are stealer logs, access broker forums, ransomware leak sites and criminal marketplaces. Infostealer log channels share passwords stolen from infected computers. Initial access broker forums list network access by company. Ransomware gang leak sites publish exfiltrated data from non-paying victims. Criminal marketplaces on Telegram and Tor circulate bulk credential dumps. Breachsense indexes all four.
VPN and remote desktop credentials top the list, because they give an attacker direct access to your network. In Verizon’s 2026 DBIR, 44% of the access that brokers offered was VPN access. Domain admin accounts are high value because they control Active Directory. Admin access also sells for more. In Verizon’s data, an admin account cost about $1,300, almost double a regular account’s $700.
For many ransomware victims, credentials leaked within a few months of the attack. In Verizon’s 2026 DBIR, 73% of ransomware victims had a credential or infostealer leak in the year before the attack. Half of those victims had the leak in the 95 days before the attack. Infostealer malware sends stolen credentials to the malware operator within hours.
Add your domains, your vendors’ domains and your executives’ personal email addresses to your watchlist by API. We send an alert by webhook or email when a match is found. Your SOAR playbooks can then reset passwords and revoke session tokens. Your tools can also pull leaked credentials, broker listings and leak site posts from the Breachsense API.
Yes. Add your vendors’ domains to your watchlist. We send an alert when we find a vendor employee’s leaked password. We also send one when a group lists the vendor as a victim on its leak site. A vendor’s leak post usually won’t mention your company, even when the stolen files include your data. So add your company’s name to your watchlist too. We send an alert when the name appears inside a leaked file.
Our public ransomware group pages list each group’s most recent victims, with each victim’s industry, country and posting date. Our monthly ransomware reports give the latest victim counts across all groups. Add your own, your clients’ and your vendors’ domains to your watchlist. We send an alert when a group lists one of those companies as a victim.
Breachsense collects new posts from the leak sites of 100+ ransomware groups. How quickly we send an alert depends on your package. We also send an alert when a search term on your watchlist shows up inside a leaked file.

Ransomware Monitoring Resources

Ransomware Gangs Tracker

Live tracker of active ransomware groups, leak sites, and victim counts. Built on Breachsense’s own dark web monitoring.

Learn More

Compromised Credential Monitoring

How Breachsense tracks leaked credentials across third-party breaches and stealer logs. The data layer that powers ransomware monitoring.

Learn More

Infostealer Channels

Telegram channels that share stealer logs, often for free.

Learn More

Threat Actor Channels

Telegram channels where criminals advertise stolen data and sell access to hacked companies.

Learn More

Dark Web API

REST API for credential lookups, leak file search, and webhook alerts. Send ransomware monitoring alerts to your SIEM or SOAR.

Learn More

Ransomware Detection Methods

Detection complements monitoring. How EDR, SIEM, and behavioral monitoring catch attacks already inside your network.

Learn More

Ransomware Attack Response Plan

Playbook for what to do when an employee’s password leaks or your data appears on a leak site.

Learn More

Famous Ransomware Examples

Case studies showing how real attacks unfold, from initial access to encryption. Useful context for tabletop exercises.

Learn More

See Your Ransomware Exposure Before Attackers Use It

Book a demo