Why Criminal Telegram Channels Are Hard to Track
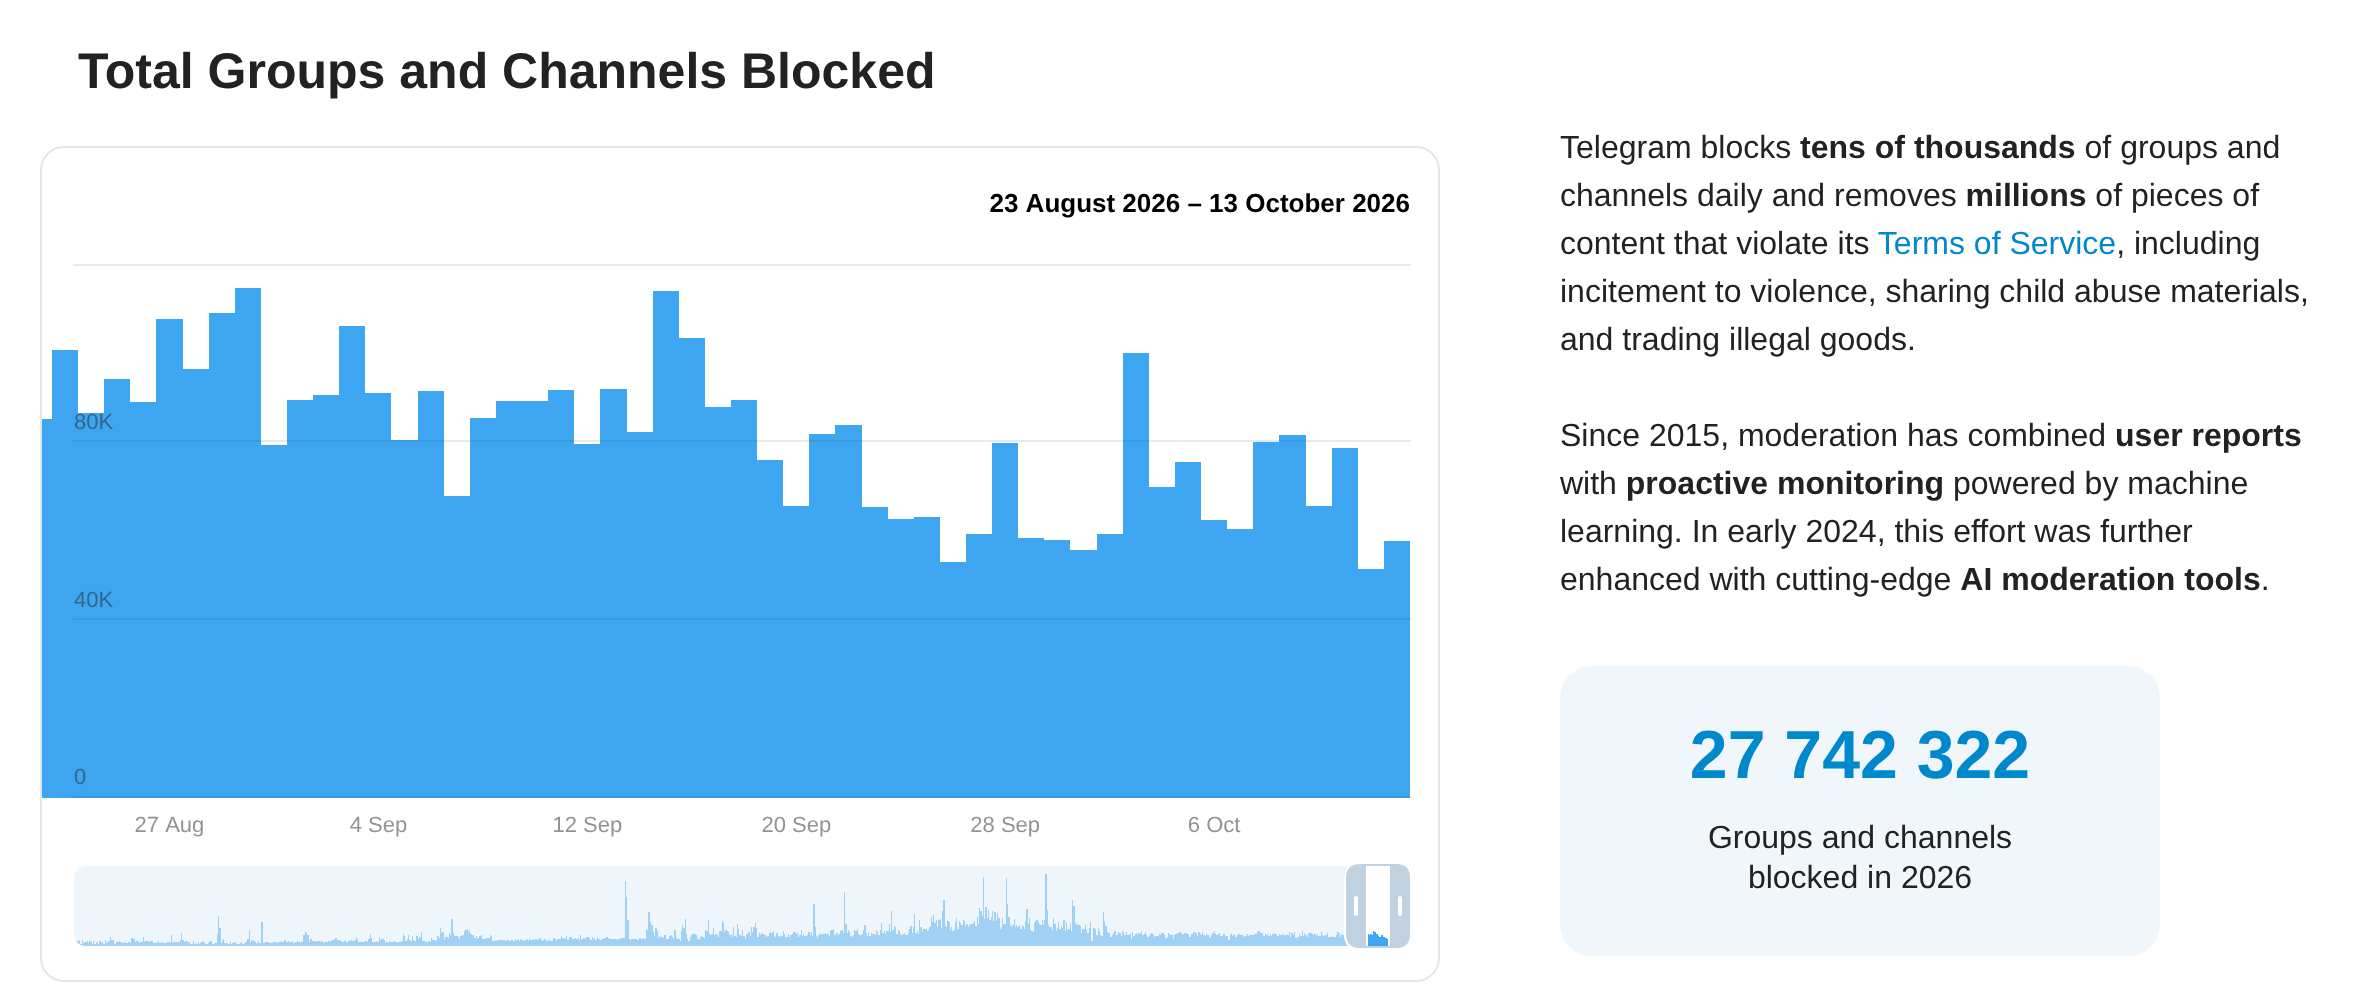
Criminal Telegram channels are hard to track because Telegram keeps blocking them. Any list of criminal channels goes out of date quickly. Telegram says it blocks tens of thousands of groups and channels every day. By October 13, Telegram had blocked 27,742,322 groups and channels in 2026, according to its moderation page.
Of the 1,057 channels on deepdarkCTI’s public list of Telegram threat actor channels, 659 are now offline or expired.
Stealer logs we indexed before Telegram blocked a channel stay searchable through our API. Besides keeping a channel list current, monitoring stealer logs yourself means processing millions of records a week, as our collection methodology explains.
Monitor Telegram Yourself or Use a Monitoring Service?
Use a monitoring service if you need to track Telegram channels continuously. Joining channels yourself suits one-off research, such as checking a single leak an analyst has heard about.
| Approach | What your team does |
|---|---|
| Analysts join channels | Find and join each replacement channel after Telegram blocks the old one, then search each stealer log by hand |
| Script on Telegram’s free API | Maintain the channel list, log parsing and alerts |
| Breachsense free dark web scan | Run a one-time check; no alerts follow |
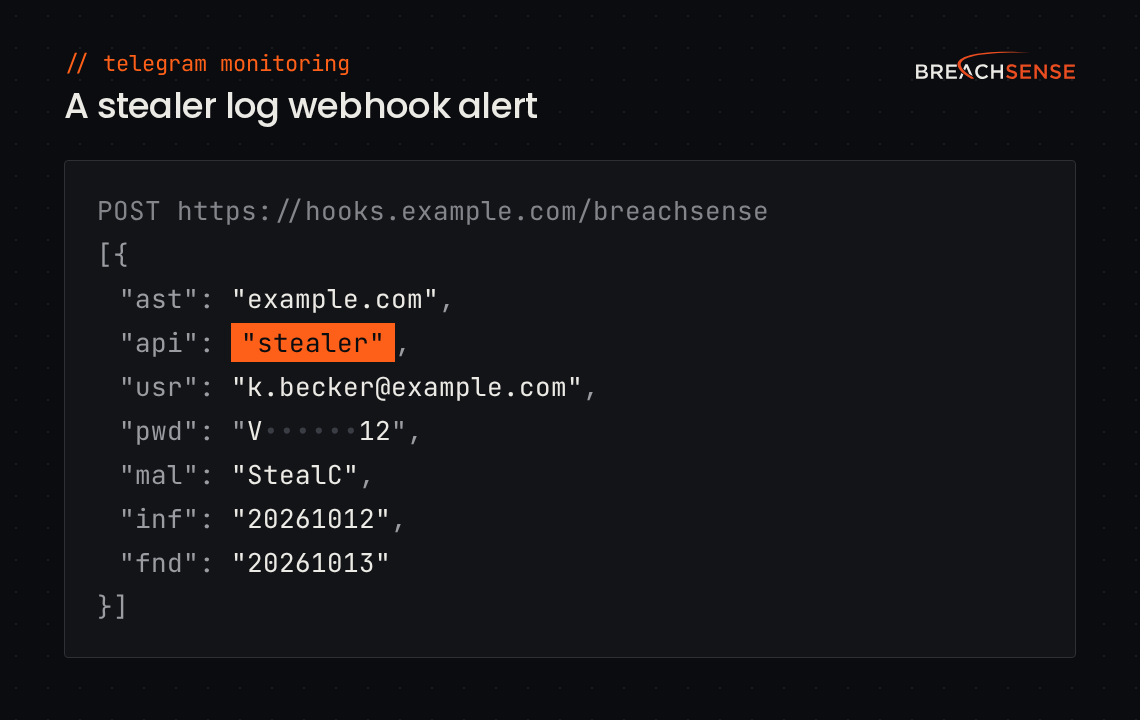
| Breachsense monitoring | Add your domains once through our dark web monitoring API, then reset each leaked password we send you by webhook or email |
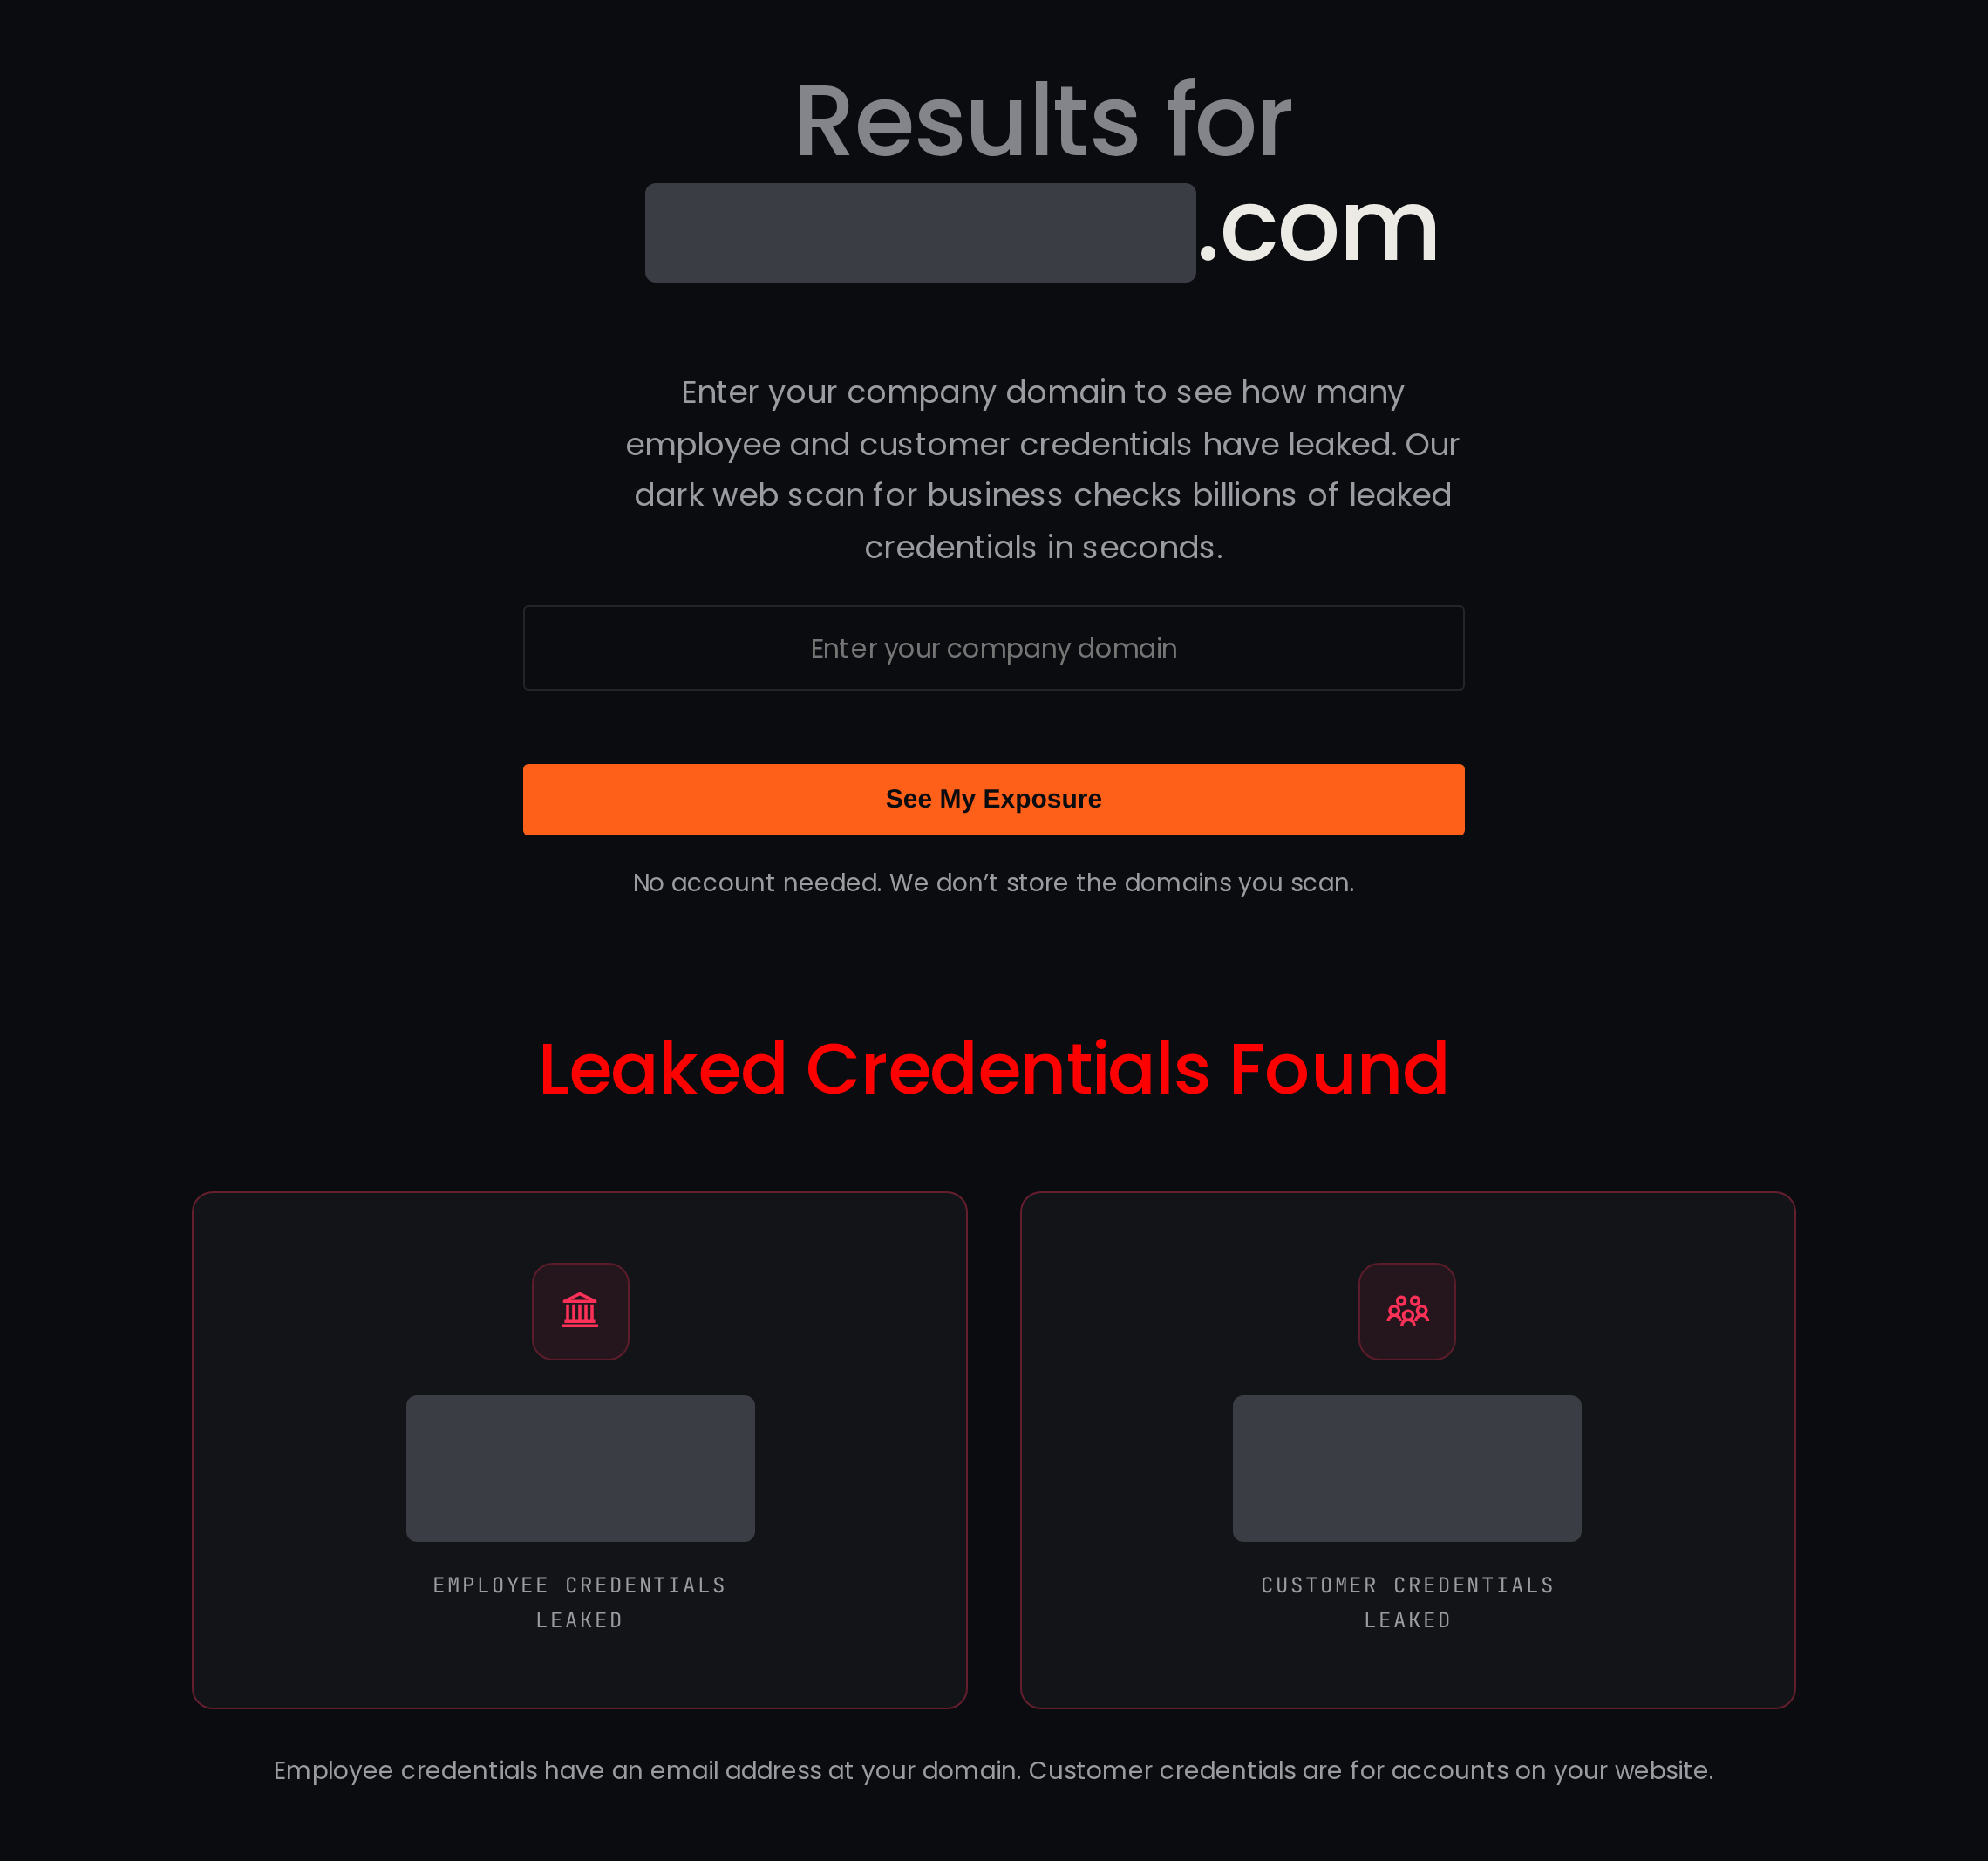
Our free dark web scan counts the leaked employee and customer credentials for a domain (redacted here). Source: breachsense.com, October 2026
Who Uses Telegram Monitoring?
SecOps and incident response teams, threat intelligence teams, third-party risk teams and service providers use Breachsense for Telegram monitoring.
-
SECOPS / IR
SecOps and incident response
Catch employee credentials within hours of infostealer operators dumping fresh logs into a channel. During triage, pivot from a password or IP address in one stealer log to every other record with the same value.
What they use:webhook alertssession token detectioninfostealer pivots -
THREAT INTEL
Threat intelligence teams
Watch the channels where access brokers advertise and ransomware groups announce victims, so you see threats forming before they reach your network.
What they use:channel coverageransomware victim alertsthreat actor chatter about your domain -
THIRD-PARTY RISK
Third-party risk teams
Know when a vendor is named in a ransomware announcement or access listing, so you can act before their breach becomes your exposure.
What they use:vendor and subsidiary lookupsransomware announcementsdomain monitoring -
MSSP
Service providers
Deliver Telegram coverage across your client base with per-client webhook routing, as part of our dark web monitoring for MSSPs. Show prospects their own leaked credentials live on a sales call.
What they use:per-client webhook routinglive credential lookupsAPI access