Infostealer Attacks in September 2026: Monthly Report
Quick Summary
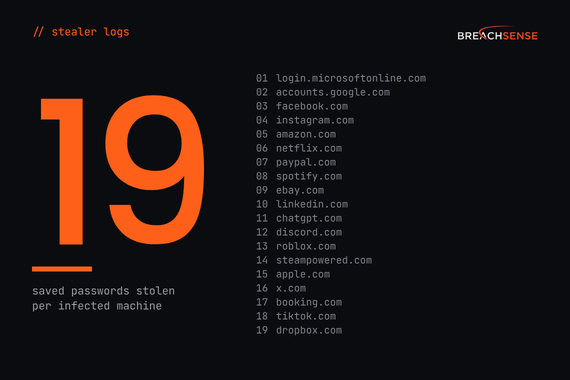
The stealer logs we indexed in September 2026 came from 1,176,466 infected machines. The median machine leaked 19 saved credentials, and 166,287 machines had a Microsoft 365 password saved. When an employee turns up in a stealer log, reset their work passwords and revoke their sessions. Then have them change every other password saved in that browser.
One infected machine leaks every password saved in its browser
Infostealer malware takes every password saved in the browser, work and personal. The median infected machine in September’s logs leaked 19 saved passwords, and a quarter leaked more than 61. A personal password the employee also uses at work puts the work account at risk too.
We index stealer logs leaked or sold on private Telegram channels and criminal marketplaces.
Why listen to us?
Breachsense is a dark web monitoring API that indexes stealer logs alongside phishing kit credentials and breach data. Our founder, Josh Amishav, used leaked credentials to get into client networks during nearly 20 years as a penetration tester. Our stealer-log alerts include the plaintext password and, when the log records them, details of the infected machine. We’ve indexed over 41 billion leaked credentials. Kaspersky’s ICS CERT cites our breach records in its quarterly industrial cybersecurity reports, and TechTarget has cited our research. See who else cites our data.
Does a password reset end a stolen session?
Not always. Microsoft Entra ID ends sessions created with a password when the password changes. Sessions from a passwordless sign-in keep working, so a stolen session cookie still gets the attacker in. Revoking the user’s sessions in Entra ends them all.
September 2026 infostealer numbers at a glance
- 1,176,466 infected machines identified in the logs we indexed
- 19 saved credentials leaked from the median machine
- 115,531,775 credential records, containing 53,760,438 distinct username and password pairs
- 166,287 machines had a Microsoft 365 password saved
- 69,186 machines had an OpenAI credential saved
The median infected machine leaked 19 saved credentials
A quarter of machines leaked more than 61 saved credentials, and one in ten leaked more than 135.
We use the median because a few very large logs pull the average up.
One in seven infected machines had a Microsoft 365 password saved
369,893 distinct usernames for login.microsoftonline.com, the Microsoft 365 sign-in page, turned up across 166,287 machines.
6.3% of those usernames were on Microsoft’s default onmicrosoft.com tenant domains.
Monitor your tenant’s onmicrosoft.com domain, not just your main domain. The first admin account in a Microsoft 365 tenant is created on the onmicrosoft.com domain.
AI and developer accounts in September’s logs
OpenAI credentials turned up on 69,186 machines, one in every 17.
| AI platform | Credentials |
|---|---|
| openai.com | 111,544 |
| huggingface.co | 6,811 |
| runwayml.com | 3,238 |
| mistral.ai | 87 |
| chatgpt.com | 74 |
| cohere.com | 24 |
GitHub credentials came from 83,809 machines, more than any other developer platform we track.
| Platform | Credentials |
|---|---|
| discord.com | 791,272 |
| github.com | 141,742 |
| slack.com | 15,563 |
| docker.com | 6,355 |
| gitlab.com | 4,856 |
| atlassian.net | 2,458 |
| npmjs.com | 1,746 |
| bitbucket.org | 1,269 |
A stolen GitHub session cookie gets an attacker past GitHub’s two-factor check. Revoke GitHub sessions for any employee whose machine turns up in a stealer log.
What security teams should do
Have the employee change every password saved in that browser. Start with any they also use for a work account.
Revoke the user’s sessions too, starting with Microsoft 365 and GitHub.
Route stealer-log alerts into your SOAR or ticketing system. Breachsense sends alerts by webhook, so a stealer-log alert can open the reset and revocation tasks without someone reading it first.
How we collected this data
This report counts the infostealer logs we index, not all infostealer activity for the month. Figures are dated by when we indexed the log, not when the machine was infected. We don’t compare monthly totals, because the number of logs we index varies from month to month.
The same credential often turns up in several logs, so September’s 115,531,775 records contain 53,760,438 distinct username and password pairs.
21.4% of September’s credential records have no machine identifier. The per-machine figures use the 90,822,586 records that include a machine identifier. The per-machine figures count each combination of site, username and password once per machine. The Credentials columns count distinct username and password pairs.
The platform tables cover a fixed list of sites, not every site in the logs.
Find out if your staff are in stealer logs
Dark web monitoring alerts you by webhook or email when we find one of your employees’ passwords in a stealer log.
Breachsense is a dark web monitoring API for security teams and MSSPs. It finds credentials and session tokens that have already been stolen from your staff or customers, whether by infostealer malware or a phishing page. It delivers them by webhook so teams can reset the affected accounts before attackers use them. It also indexes the files ransomware groups leak, so you can search them for your own company’s data.
To see what has already leaked for your domain, run a free dark web scan, then book a demo to set up alerts.
Our September 2026 phishing report counts credentials taken from fake login pages. The September 2026 ransomware report counts the companies named on leak sites.