How Breachsense Compares to Traditional Detection
SIEM, EDR (endpoint detection and response) and DLP (data loss prevention) tools monitor systems you control. Breachsense finds your data in the dark web sources where stolen files and credentials end up.
| Capability | Breachsense | SIEM | EDR | DLP |
|---|---|---|---|---|
| Finds your data after attackers leak it | Included | |||
| Finds your employees' leaked passwords | Included | |||
| Full-text search across leaked files from ransomware attacks | Included | |||
| Finds credentials stolen from unmanaged or personal devices | Included | |||
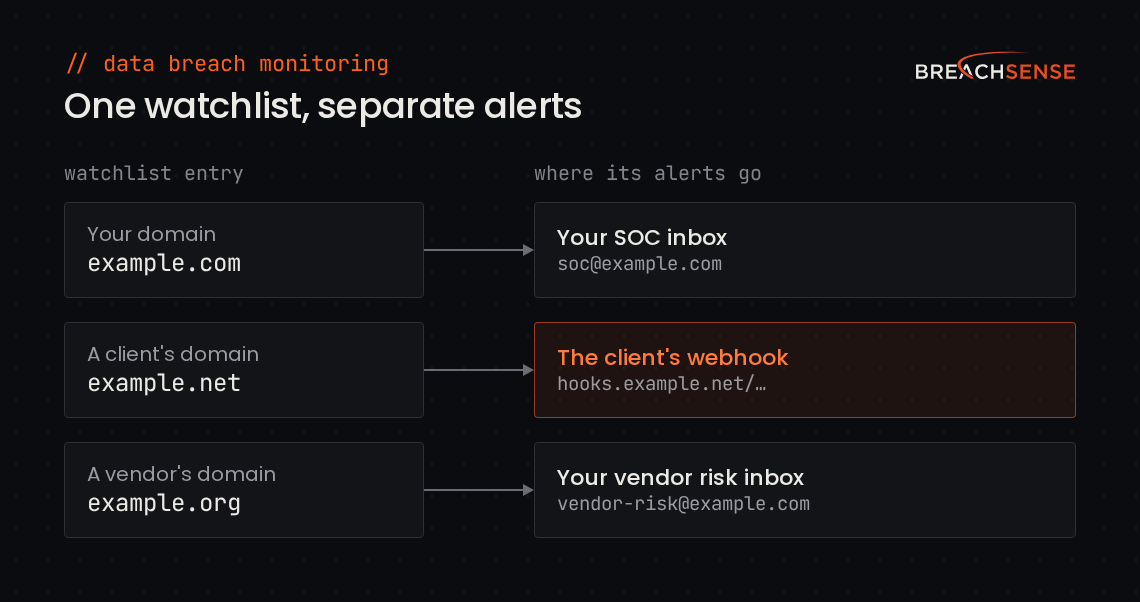
| Finds your data in a vendor's breach | Included | |||
| Detects an attacker inside your network | Partial | Included | ||
| Blocks data from leaving your network | Included | |||
| Correlates logs across your systems | Included | |||
| When it can alert | Once the data shows up in a source we monitor | Only when logs show activity | Only on managed endpoints | Only on devices, apps and networks you control |
| Requires endpoint agents | No | For endpoint logs | Yes | Endpoint DLP only |
Who Uses Breachsense Data and Why
-
SOC Analysts
Alert triage and response
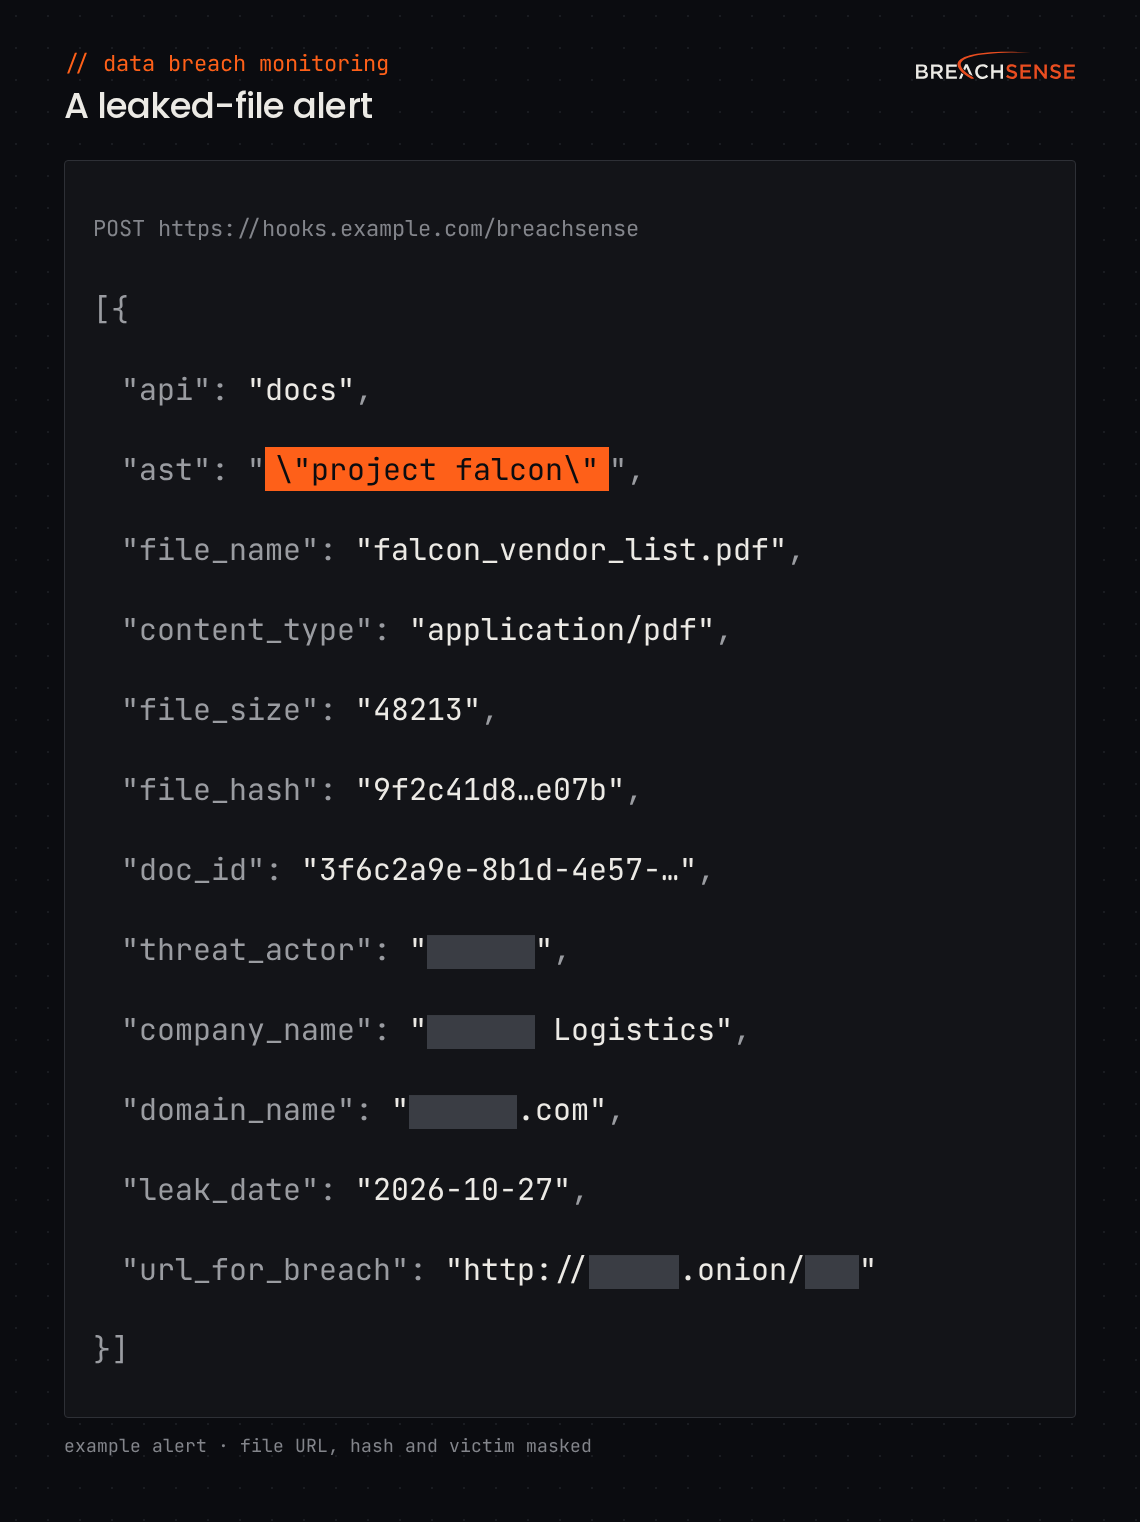
We send each alert as JSON to your SIEM or SOAR tool, which can open a ticket and start your playbook.
What they use: -
CISOs
Board reporting on exposure
Pull every leaked credential from our API with its source and date, including credentials leaked in third-party breaches. Then count them by source or month.
What they use:Leaked credential countsthird-party breach credentialsdate found on every record -
Incident Response
Post-breach scoping
During an incident, search our API for your domain's leaked credentials to see which accounts the attacker could have used. If a ransomware group posts your files, you can search them for customer and employee data.
What they use:Full-text leak file searchper-user credential historyAPI searches by IP address or email -
Compliance Teams
Notification triggers
Each leaked-file match includes the leak date and a link to the file. Your legal team can open the file to see which customer records it contains before deciding whether to notify customers or regulators.
What they use:Leaked-file alertsleak date and file URL for each match