10 Best Cyber Threat Intelligence Tools (2026): Do You Need the Platform or Just the Data?
Quick Summary
The best cyber threat intelligence tools are Breachsense for finding stolen employee credentials and session tokens, and Recorded Future for analyst teams that research attackers. CrowdStrike Falcon Adversary Intelligence suits teams already running Falcon. If you need a platform to pull many feeds together, shortlist Anomali ThreatStream, ThreatConnect, ThreatQ or OpenCTI.
| Tool | Built for | Collects or aggregates | Rating |
|---|---|---|---|
| Breachsense | Stolen credentials, session tokens and leaked files | Collects, from stealer logs, phishing kits and leak sites | 4.8/5 (G2) |
| Recorded Future | Analyst teams, plus stolen credentials | Collects, from over a million sources | 4.5/5 (G2) |
| CrowdStrike Falcon Adversary Intelligence | Falcon customers tracking adversaries | Collects, from its own research and the criminal underground | 4.7/5 (Gartner Peer Insights) |
Do you need a threat intelligence platform, or just the data?
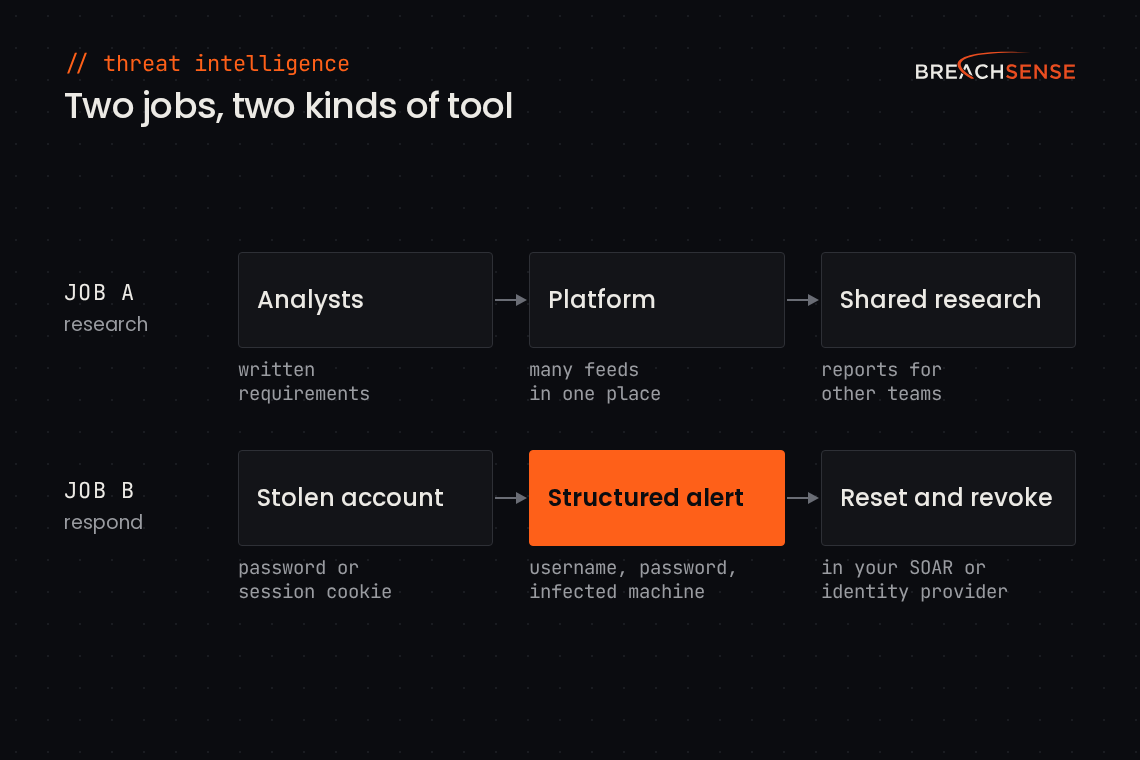
Do you need a threat intelligence platform, or just the data? You need a platform if your team has analysts with written intelligence requirements, and just the data if your team’s job is finding and resetting stolen accounts.
Job A: your team has analysts. They write intelligence requirements and research the groups that attack companies like yours. They need a platform to collect that research and share it with other teams.
Job B: your team needs to know what’s already stolen. The stolen data includes employee passwords in infostealer logs, session cookies or your leaked files inside a supplier’s ransomware breach. A playbook in your SOAR (security automation tool) or identity provider can reset each stolen password, or revoke each stolen session, as soon as the alert arrives. For the playbook to act, the alert has to include the username and plaintext password as structured data.
Why listen to us?
Breachsense is one of the tools on this list, so the ratings, pros and cons for the other nine come from user reviews. Our founder, Josh Amishav, spent nearly 20 years as a penetration tester. He found that the easiest way to gain initial access during an engagement was with leaked credentials. Based on that experience, Breachsense was born. We have over 41 billion leaked records indexed. Our research has been cited by Kaspersky ICS CERT and TechTarget. We collect the same stolen credentials and leaked files that end up in tools like these.
What are cyber threat intelligence tools?
Cyber threat intelligence tools are software and data services that tell your security team who is attacking companies like yours and what they’ve already stolen.
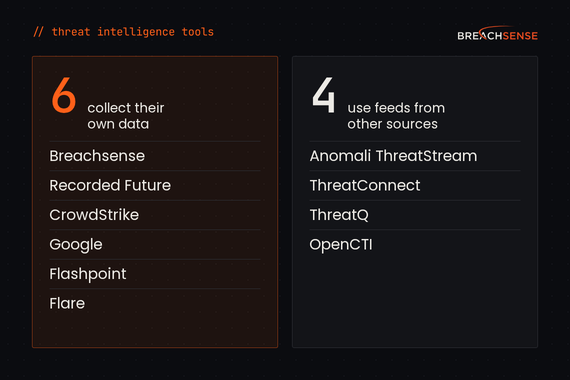
Data sources collect threat information themselves. Threat intelligence platforms (TIPs) pull many sources into your SIEM (the system that collects your security logs) or SOAR. Some vendors sell both.
A threat intelligence platform automates parts of the threat intelligence lifecycle with these seven jobs:
- Collect indicators and reports from feeds.
- Correlate them, so one IP address links to the campaign it belongs to.
- Enrich each item with context, such as which attacker uses it.
- Analyze the enriched data.
- Integrate the output into your SIEM or firewall.
- Act on the analysis.
- Collaborate by sharing findings with other teams.
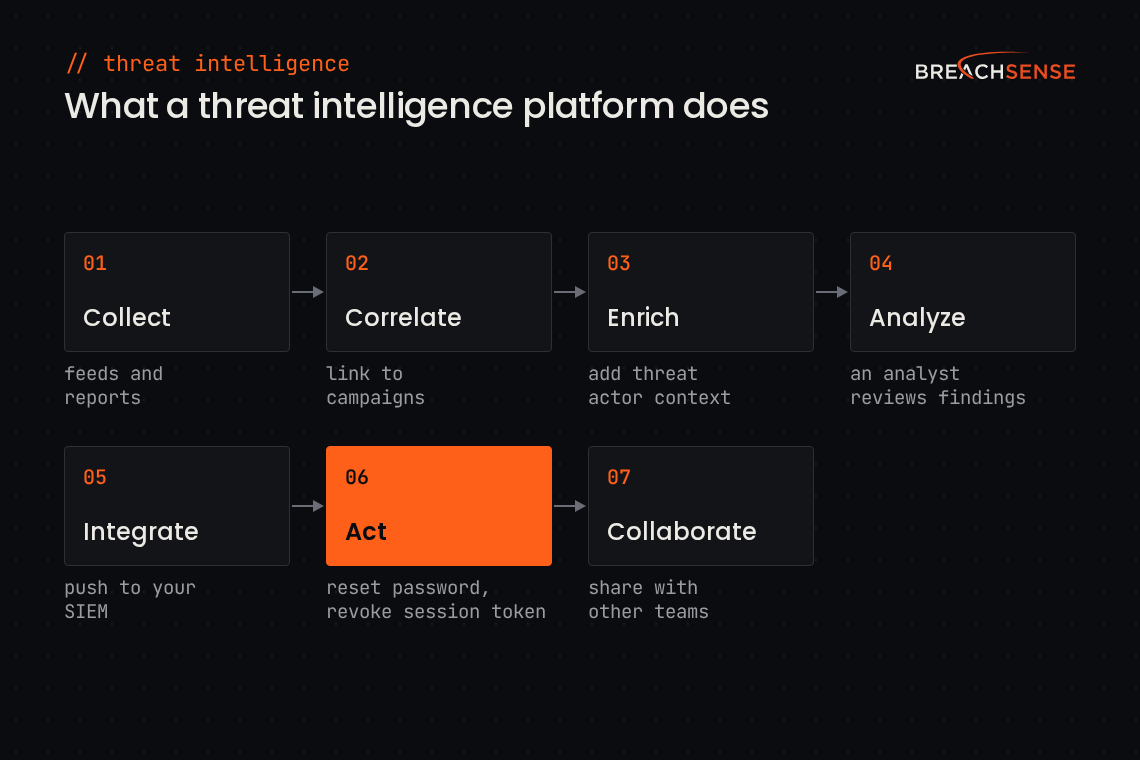
For a stolen account, step six means resetting the password and revoking the user’s sessions. The platform hands that step to your SOAR, your identity provider or a person.
Why are cyber threat intelligence tools important?
- Attackers exploit known vulnerabilities first. Exploiting a vulnerability is now the most common way attackers get in. Verizon’s 2026 Data Breach Investigations Report puts it at 31% of the breaches where the way in is known (p.10). Threat intelligence shows which vulnerabilities attackers are exploiting now.
- Leaked credentials often surface months before ransomware. Verizon looked at ransomware victims whose credentials leaked, or turned up in infostealer logs, in the year before the attack (p.44). For half of them, the leak came within 95 days of the ransomware attack. A leaked credential found that early gives you time to reset the password.
- Stolen session cookies bypass multi-factor authentication (MFA). Infostealer malware steals session cookies along with passwords. A stolen session cookie lets an attacker bypass the MFA prompt.
- Ransomware leak sites post suppliers’ files. When a supplier is hit, your contracts and customer records can be in the files the ransomware group publishes.
- Context shows which alerts matter. The infection date in an alert shows how recently a password was stolen, so you can prioritize resetting accounts.
10 best cyber threat intelligence tools
- Breachsense
- Recorded Future
- CrowdStrike Falcon Adversary Intelligence
- Google Threat Intelligence
- Flashpoint
- Flare
- Anomali ThreatStream
- ThreatConnect (Dataminr)
- ThreatQ (Securonix)
- OpenCTI
We checked every cell except Rating against the vendor’s own site in October 2026. Ratings come from the review site named in each entry.
| Tool | Built for | Collects or aggregates | What a credential match includes | How it arrives | After a match | Rating |
|---|---|---|---|---|---|---|
| Breachsense | Stolen credentials, session tokens and leaked files | Collects, from stealer logs, phishing kits and leak sites | Plaintext password where the password hash can be cracked, infected machine details, session token | Webhook and REST API, into your own tools | Your SOAR or identity provider resets | 4.8/5 (G2) |
| Recorded Future | Analyst teams, plus stolen credentials | Collects, from over a million sources | Credentials from infostealer logs, combo lists and database dumps | Portal, API, identity provider and SOAR integrations | Automated resets via Okta, Azure AD or a SOAR | 4.5/5 (G2) |
| CrowdStrike Falcon Adversary Intelligence | Falcon customers tracking adversaries | Collects, from its own research and the criminal underground | Exposed credentials found by its Recon module | Falcon console, API, SOAR | Resets through CrowdStrike’s own identity product | 4.7/5 (Gartner Peer Insights) |
| Google Threat Intelligence | Alert triage and analyst teams | Collects, from Google, Mandiant and VirusTotal | Leaked credentials, in plaintext only for domains you verify | Platform, API, email alerts, Google SecOps | Your playbooks | 10/10 (TrustRadius) |
| Flashpoint | Analysts researching forums, fraud and vulnerabilities | Collects, from sources it operates | Credentials, cookies and infostealer logs, with host details | Ignite platform, API, SIEM and SOAR connectors | Your playbooks | 4.5/5 (G2) |
| Flare | Leaked identities, acted on in Entra ID or Okta | Collects, from stealer log markets, the dark web and Telegram | Stealer log credentials, mapped to an identity profile | Portal, API, webhooks, SIEM and ticketing integrations | Revokes sessions or disables the account via Entra ID or Okta (add-on) | 4.7/5 (Gartner Peer Insights) |
| Anomali ThreatStream | Analyst teams that share intelligence | Aggregates hundreds of feeds | Whatever your credential feed provides | Platform, pushes to SIEM and SOAR | Your playbooks | 4.8/5 (Gartner Peer Insights) |
| ThreatConnect (Dataminr) | Analyst teams that automate with playbooks | Aggregates 300+ sources, plus Dataminr’s own | Whatever your feed provides | Platform, playbook triggers | Your playbooks | 4.6/5 (G2) |
| ThreatQ (Securonix) | Analyst teams that want one threat library | Aggregates, over 450 integrations | Whatever your feed provides | Platform | Your playbooks, or Okta actions an analyst runs | 5.0/5 (Gartner Peer Insights) |
| OpenCTI | Analyst teams with no platform budget | Aggregates, 400+ connectors | Whatever your feed provides | Self-hosted or SaaS, STIX/TAXII | Your playbooks (Enterprise Edition) | 4.6/5 (G2) |
For Job A, three of the collection vendors add research beyond credentials. Recorded Future, Google and Flashpoint each have their own research team, so analysts get finished reports on attackers and vulnerabilities.
For Job B, look at the credential, delivery and after-a-match columns. In a trial, check that a sample alert includes the username and plaintext password a playbook needs.
1. Breachsense
Breachsense isn’t a threat intelligence platform. We collect stolen credentials, session tokens and leaked files. Each finding goes to your SIEM or TIP as a webhook alert. Your tools can also pull findings from our API.
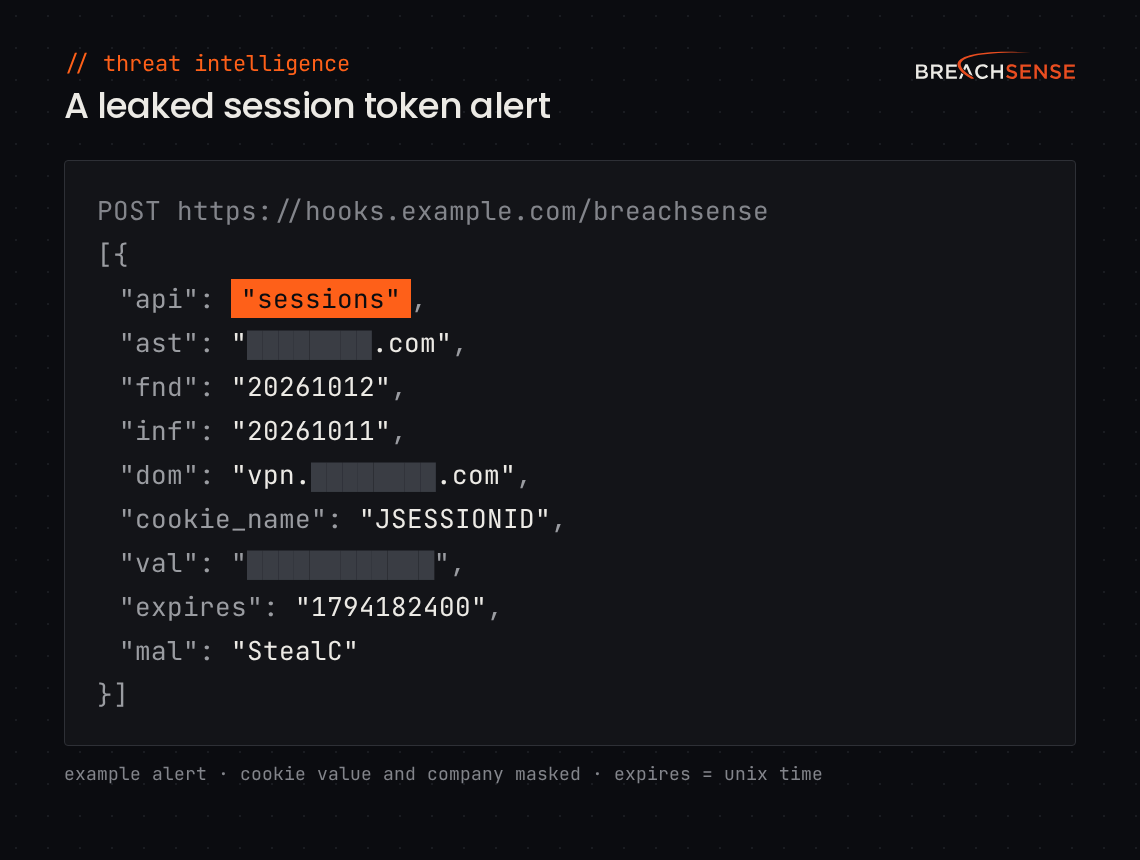
A plaintext password shows whether the employee in the alert already rotated it. A raw session cookie tells you which session to revoke. The infection date shows how recently the password was stolen. We also collect passwords from phishing kits, the code that runs fake login pages. A password from a phishing kit means the employee typed it into a fake page, so the account is definitely compromised.
We index files from 100+ ransomware groups, so you can search inside those files for your company’s data. Our dark web monitoring API returns every finding as JSON.
Key features
- Stealer log credentials: usernames and passwords from infected machines, plus the device name and malware family when the log records them.
- Session tokens: stolen browser cookies, with each cookie’s name, domain and expiry.
- Phishing kit captures: passwords employees typed into fake login pages.
- Leaked file search: full-text search inside files leaked in ransomware attacks and third-party breaches, plus files from unsecured databases.
- Plaintext password recovery: we crack passwords stored in weak hash formats.
- Pivoting from one infected device: search by the device’s IP address, or by a username or password from the alert, to find related stolen credentials.
- Webhook alerts: findings go to the webhook or email address you set for each monitored domain.
Pricing: Not published. On a demo call, we learn your requirements, then put together a package that covers only what you need. Trials are available after the demo.
Rating: 4.8/5 on G2
Pros
- Plaintext passwords and raw session cookies, so a playbook can automate remediation.
- Full-text search inside leaked files, from ransomware attacks, third-party breaches and unsecured databases.
- Priced on what you need, with no per-seat licenses.
Cons
- No vulnerability or geopolitical intelligence.
- Resets are left to your SOAR or identity provider.
- Prices aren’t published.
2. Recorded Future
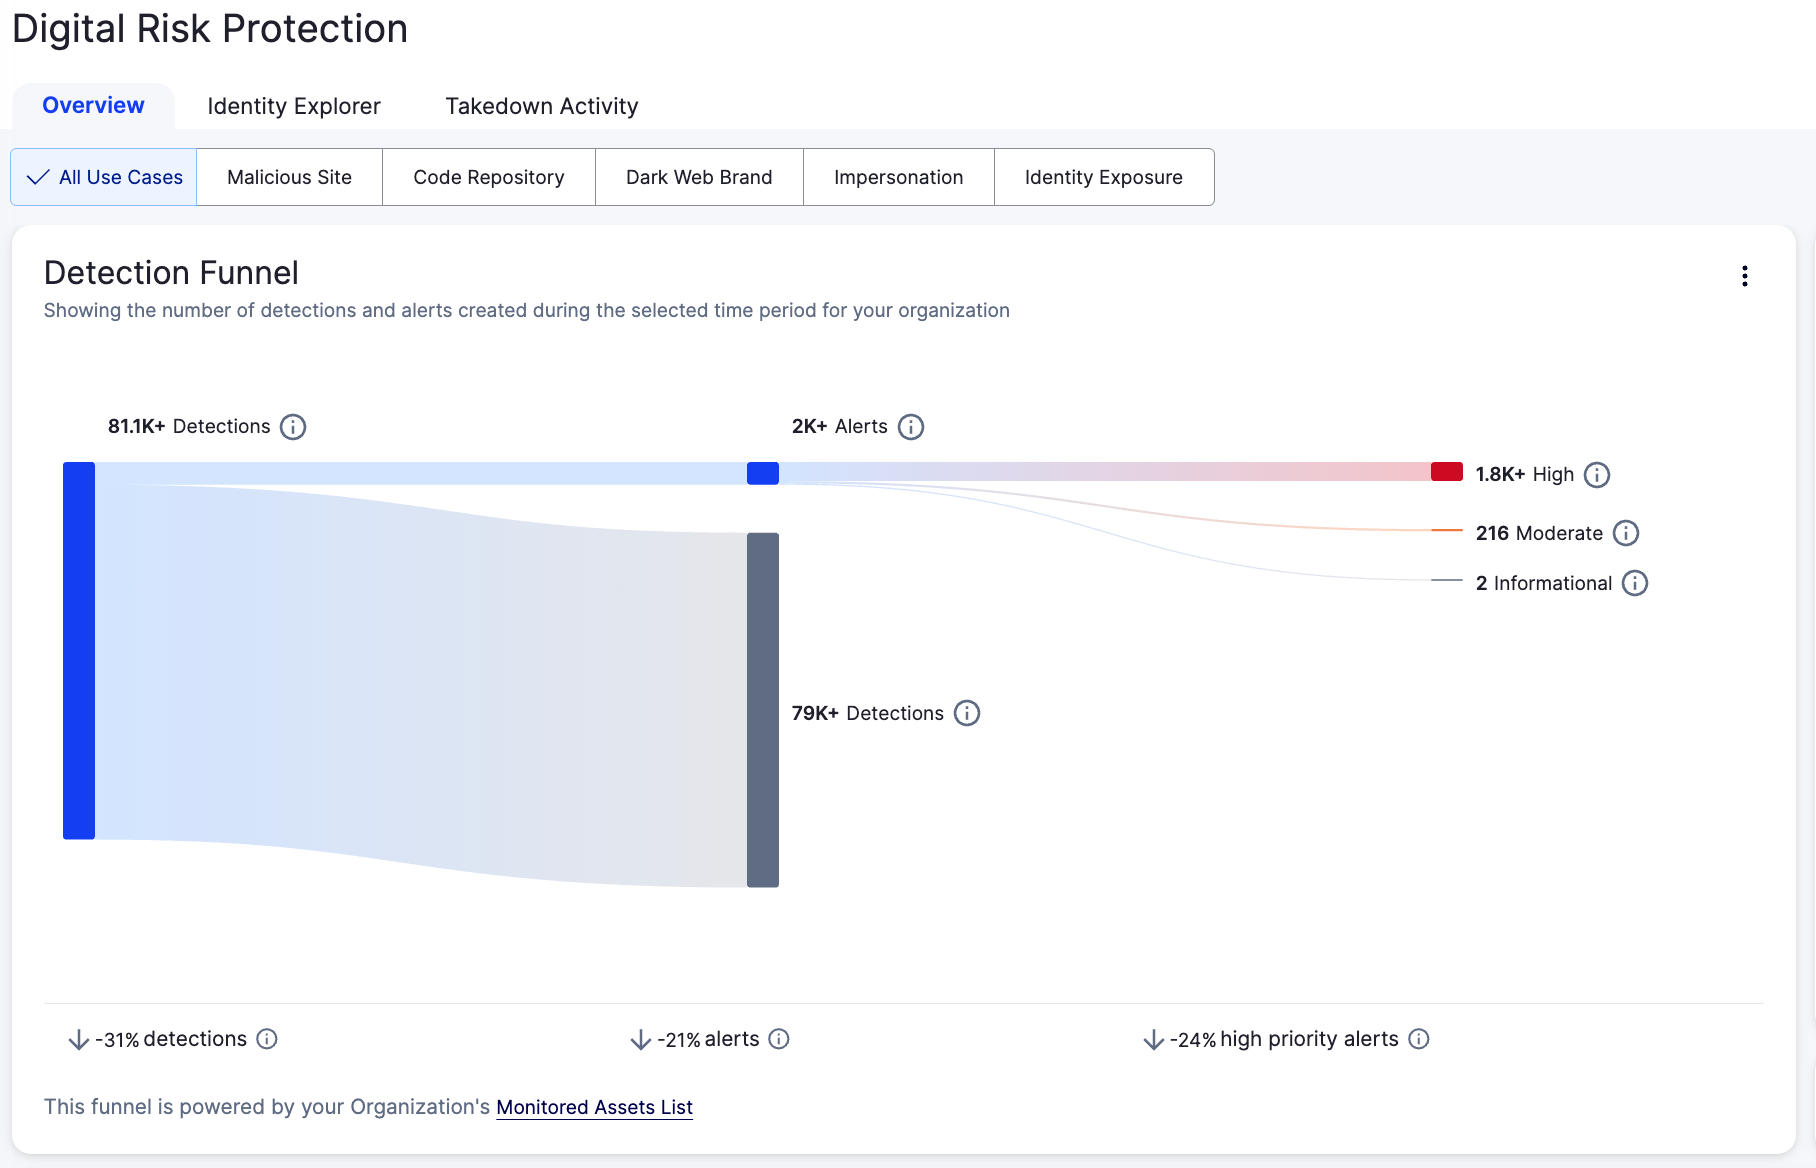
Recorded Future is a threat intelligence company that Mastercard has owned since December 2024. Recorded Future’s platform is built around analyst research. Its Identity Intelligence module also finds stolen employee credentials. Our guide to Recorded Future alternatives compares Identity Intelligence with our own alerts.
Recorded Future collects its own data, from the open and dark web, its own network sensors and its Insikt Group research team. Recorded Future says it finds 1.3 million new exposed credentials a day. Identity Intelligence can reset a password automatically through Okta, Azure AD or a SOAR.
Key features
- Intelligence Graph: links billions of entities, such as IP addresses, malware and threat actors.
- Identity Intelligence: finds credentials in infostealer logs, combo lists and database dumps.
- Intelligence Cards: one view of what’s known about an IP address, domain or file.
- Insikt Group research: reports from Recorded Future’s own analysts.
Pricing: Not published. Recorded Future prices mainly on organization size, measured by unique workforce credentials, plus the package and add-ons you choose.
Rating: 4.5/5 on G2
Pros
- Gives fast context on an IP address or a CVE (a publicly listed vulnerability), with the evidence behind it.
- Recorded Future’s malware sandbox returns packet captures.
- AI-generated reports speed up investigations of new threats.
Cons
- Expensive, and modules like Identity Intelligence often need separate licenses.
- The platform takes time to learn because there’s so much data.
- The query language is complex, and reports are hard to customize.
3. CrowdStrike Falcon Adversary Intelligence
CrowdStrike Falcon Adversary Intelligence gives security operations center (SOC) teams adversary profiles, dark web monitoring and malware analysis. CrowdStrike sells Adversary Intelligence as a module of the Falcon platform.
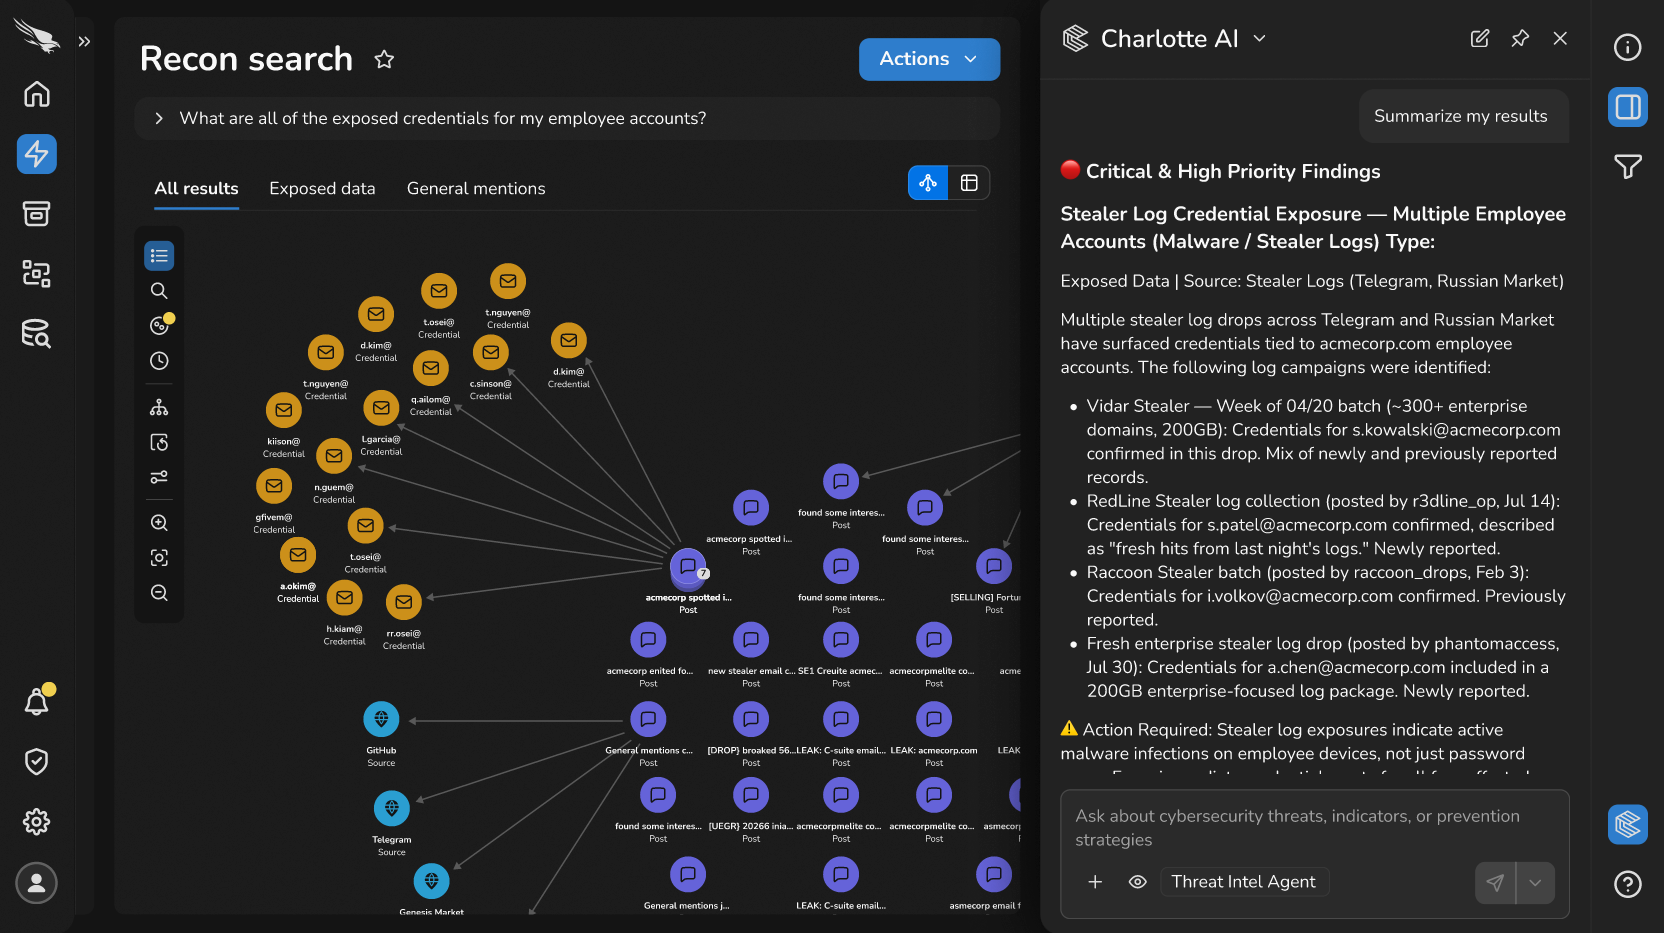
CrowdStrike collects its own data. Its researchers monitor the criminal underground. CrowdStrike says it tracks 290+ adversaries. Its Recon module finds exposed employee credentials. CrowdStrike’s own identity product, Falcon Next-Gen Identity Security, can then reset the password automatically.
Key features
- Recon: monitors the dark web for stolen credentials and other exposed company data.
- Intel Explorer: one workspace to search CrowdStrike’s intelligence.
- Malware sandbox: analyzes files, emails and command lines.
- Threat AI agents (Premium): agents that explain threats and take response actions.
Pricing: Not published. CrowdStrike licenses Adversary Intelligence by endpoint, server or employee count.
Rating: 4.7/5 on Gartner Peer Insights
Pros
- Maps each attacker group’s techniques to MITRE ATT&CK (a public catalog of attacker techniques).
- Sits inside the Falcon console, next to Falcon’s endpoint detection and response (EDR) alerts.
- Shows the attacker group’s profile when a Falcon alert fires.
Cons
- Advanced features take training to learn.
- Dashboards and reports are rigid.
- The volume of detail can overwhelm a small team without dedicated analysts.
4. Google Threat Intelligence
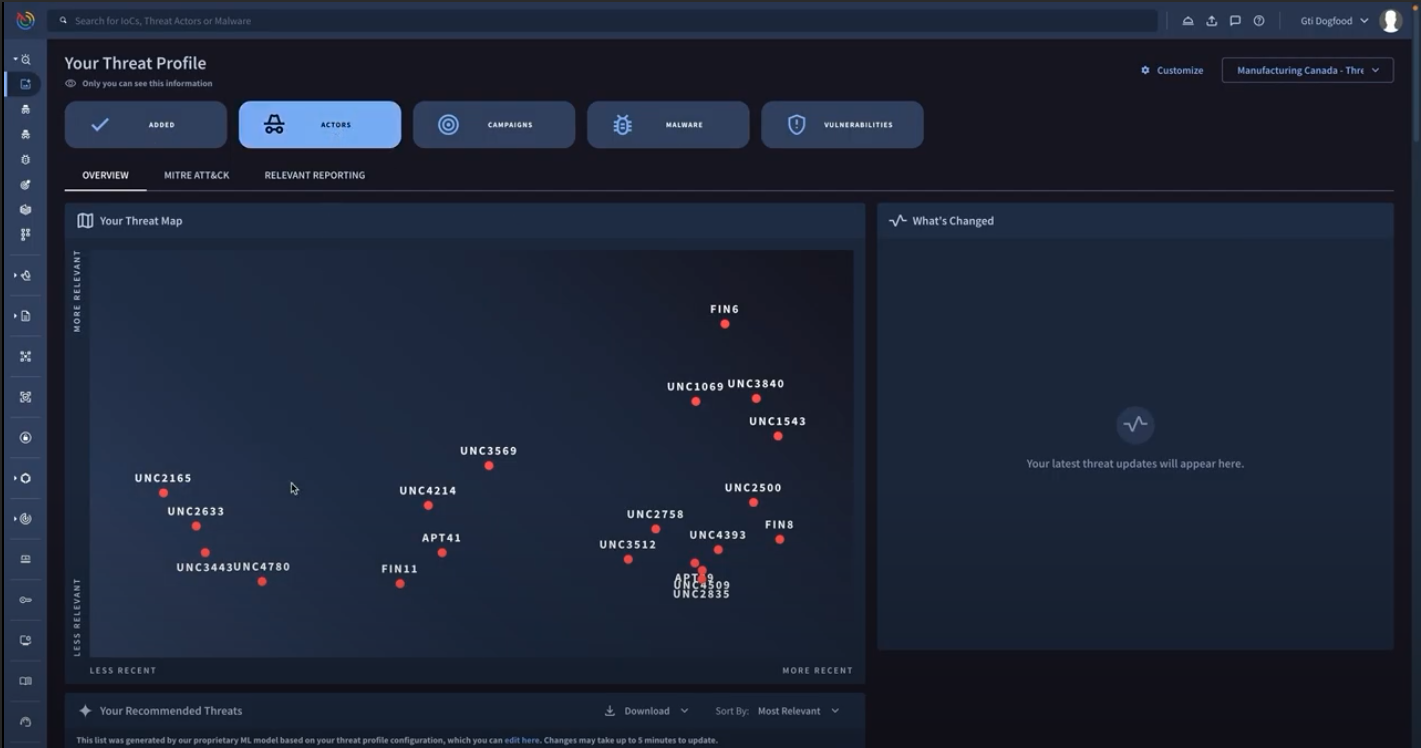
Google Threat Intelligence combines Mandiant’s incident response research, VirusTotal’s malware data and Google’s own threat data in one platform. Google built Google Threat Intelligence for SOC teams triaging alerts and for dedicated threat analysts.
Google collects its own data. Google says its teams spend hundreds of thousands of hours investigating incidents. Its Digital Threat Monitoring module alerts on leaked employee and customer credentials. Digital Threat Monitoring shows plaintext passwords only for domains you verify you own.
Key features
- Digital Threat Monitoring: monitors the open, deep and dark web for compromised credentials.
- Gemini in Threat Intelligence: an AI assistant that summarizes threats and reports.
- Workbench: Google’s malware database, plus tools to investigate indicators.
- Mandiant experts: ask a Mandiant analyst for help from inside the console.
Pricing: Not published. Google charges a flat annual rate that includes a set number of API calls. Extra call packs cost more.
Rating: 10/10 on TrustRadius
Pros
- Detailed research on threat actors and their tactics.
- Strong vulnerability intelligence, with expert analysis of each CVE.
- The API and third-party integrations are easy to set up.
Cons
- The portal is hard to customize, and navigation is rigid.
- Support is slow on requests that aren’t urgent.
- Lower tiers hide data you need partway through an investigation.
5. Flashpoint
Flashpoint sells threat intelligence through its Ignite platform, built for analyst teams that research criminal forums, fraud and vulnerabilities. Analysts can also send Flashpoint requests for information and get custom research back.
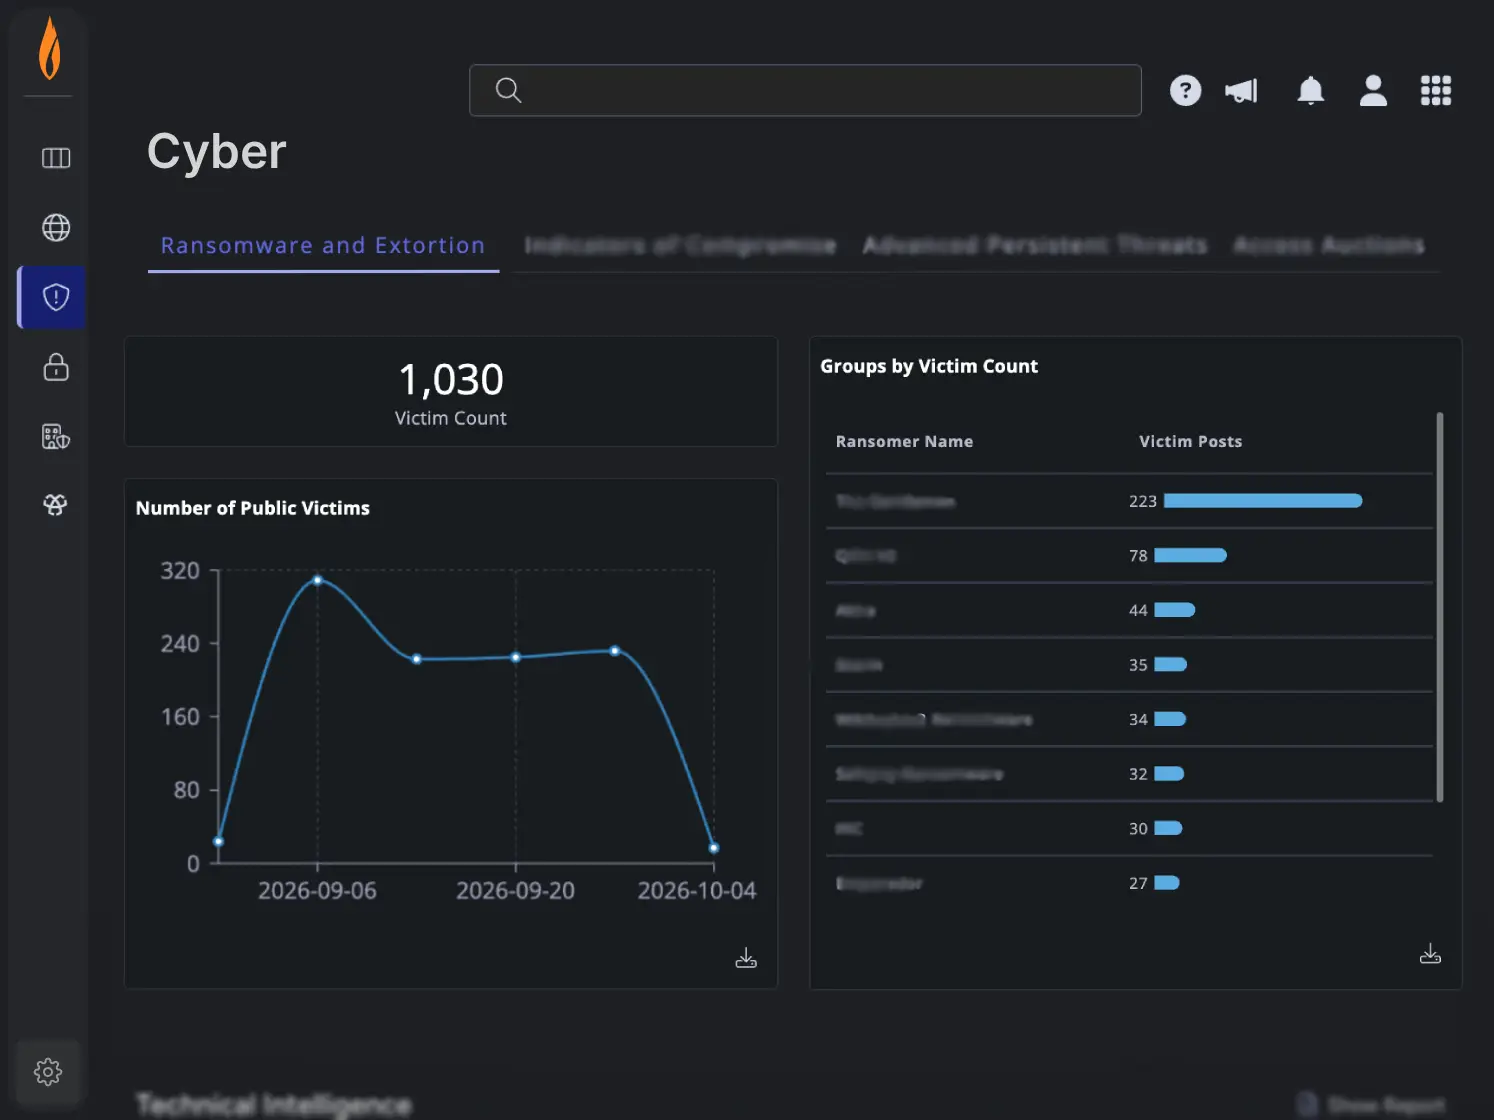
Flashpoint says it holds more than 3.6 petabytes of data from the open, deep and dark web. Its Account Takeover module covers stolen credentials and cookies.
Key features
- Primary Source Collection: Flashpoint gathers data from criminal communities itself.
- Account Takeover module: alerts on stolen employee credentials and cookies, with details of the infected host.
- Curated Alerting: alerts that Flashpoint’s analysts review before you get them.
- Vulnerability Intelligence: Flashpoint says it identifies vulnerabilities about two weeks before NVD (the US government’s vulnerability database).
Pricing: Not published. Flashpoint’s pricing page lists what each package includes, with a “Get Pricing” request for each.
Rating: 4.5/5 on G2
Pros
- Shows the raw criminal posts and listings, with a link to the original post.
- Analysts answer requests for information quickly, with thorough reports.
- The Ignite search is easy to filter by channel and author.
Cons
- Keyword alerts can be noisy and take work with Flashpoint’s team to tune.
- Each request for information draws down a block of analyst hours, so costs are hard to predict.
- Frequent platform changes have broken integrations for some customers.
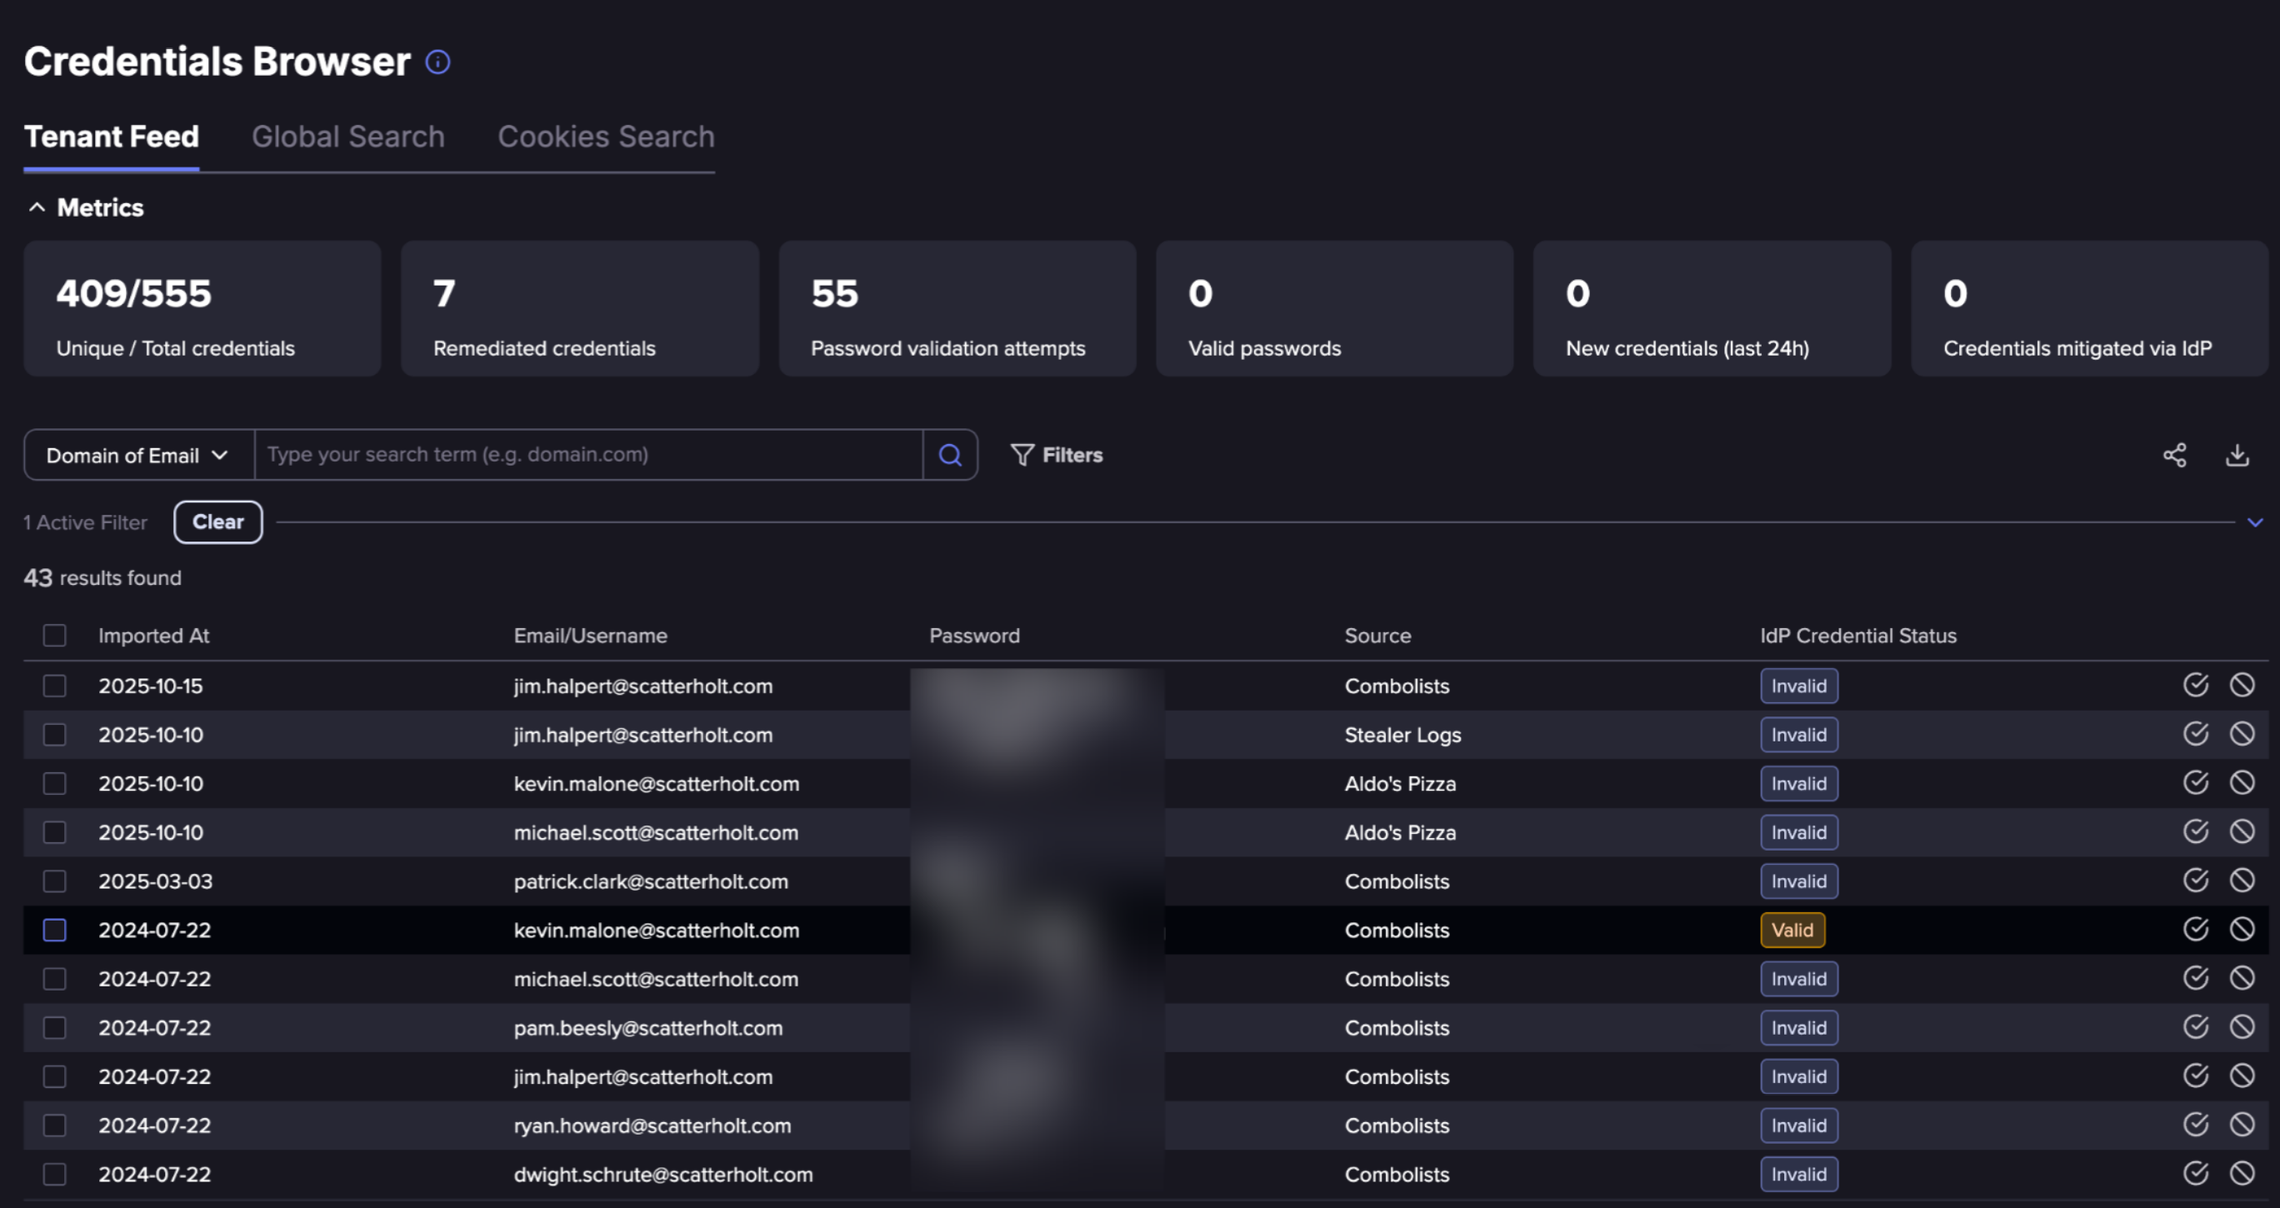
6. Flare
Flare is a threat intelligence service for security operations, threat intelligence and fraud teams, and for managed security providers.
Flare collects its own data from the dark web, stealer log markets and Telegram. Flare says it adds over 1 million new stealer logs a week. Its Identity Exposure Management add-on can mark a user compromised, disable the account or revoke the user’s sessions through Entra ID or Okta. The password reset itself is left to your Conditional Access policy.
Key features
- Identity Exposure Management: links leaked credentials to each employee’s identity in Entra ID or Okta.
- Stealer Log Intelligence: credentials and cookies from infected machines.
- Threat Flow: an AI engine that translates dark web discussions and correlates them across sources.
- Dark Web and Telegram Monitoring: Flare says it covers 127,000+ Telegram channels.
Pricing: Not published. Flare offers a free trial.
Rating: 4.7/5 on Gartner Peer Insights
Pros
- Analysts without deep technical knowledge can set up Flare and investigate its alerts.
- New leaks appear in Flare quickly, in some cases within hours of the breach.
- Flare’s support team answers questions quickly and acts on feature requests.
Cons
- You can’t customize alerts or response actions much.
- Integrations with other security and SaaS tools are limited.
7. Anomali ThreatStream
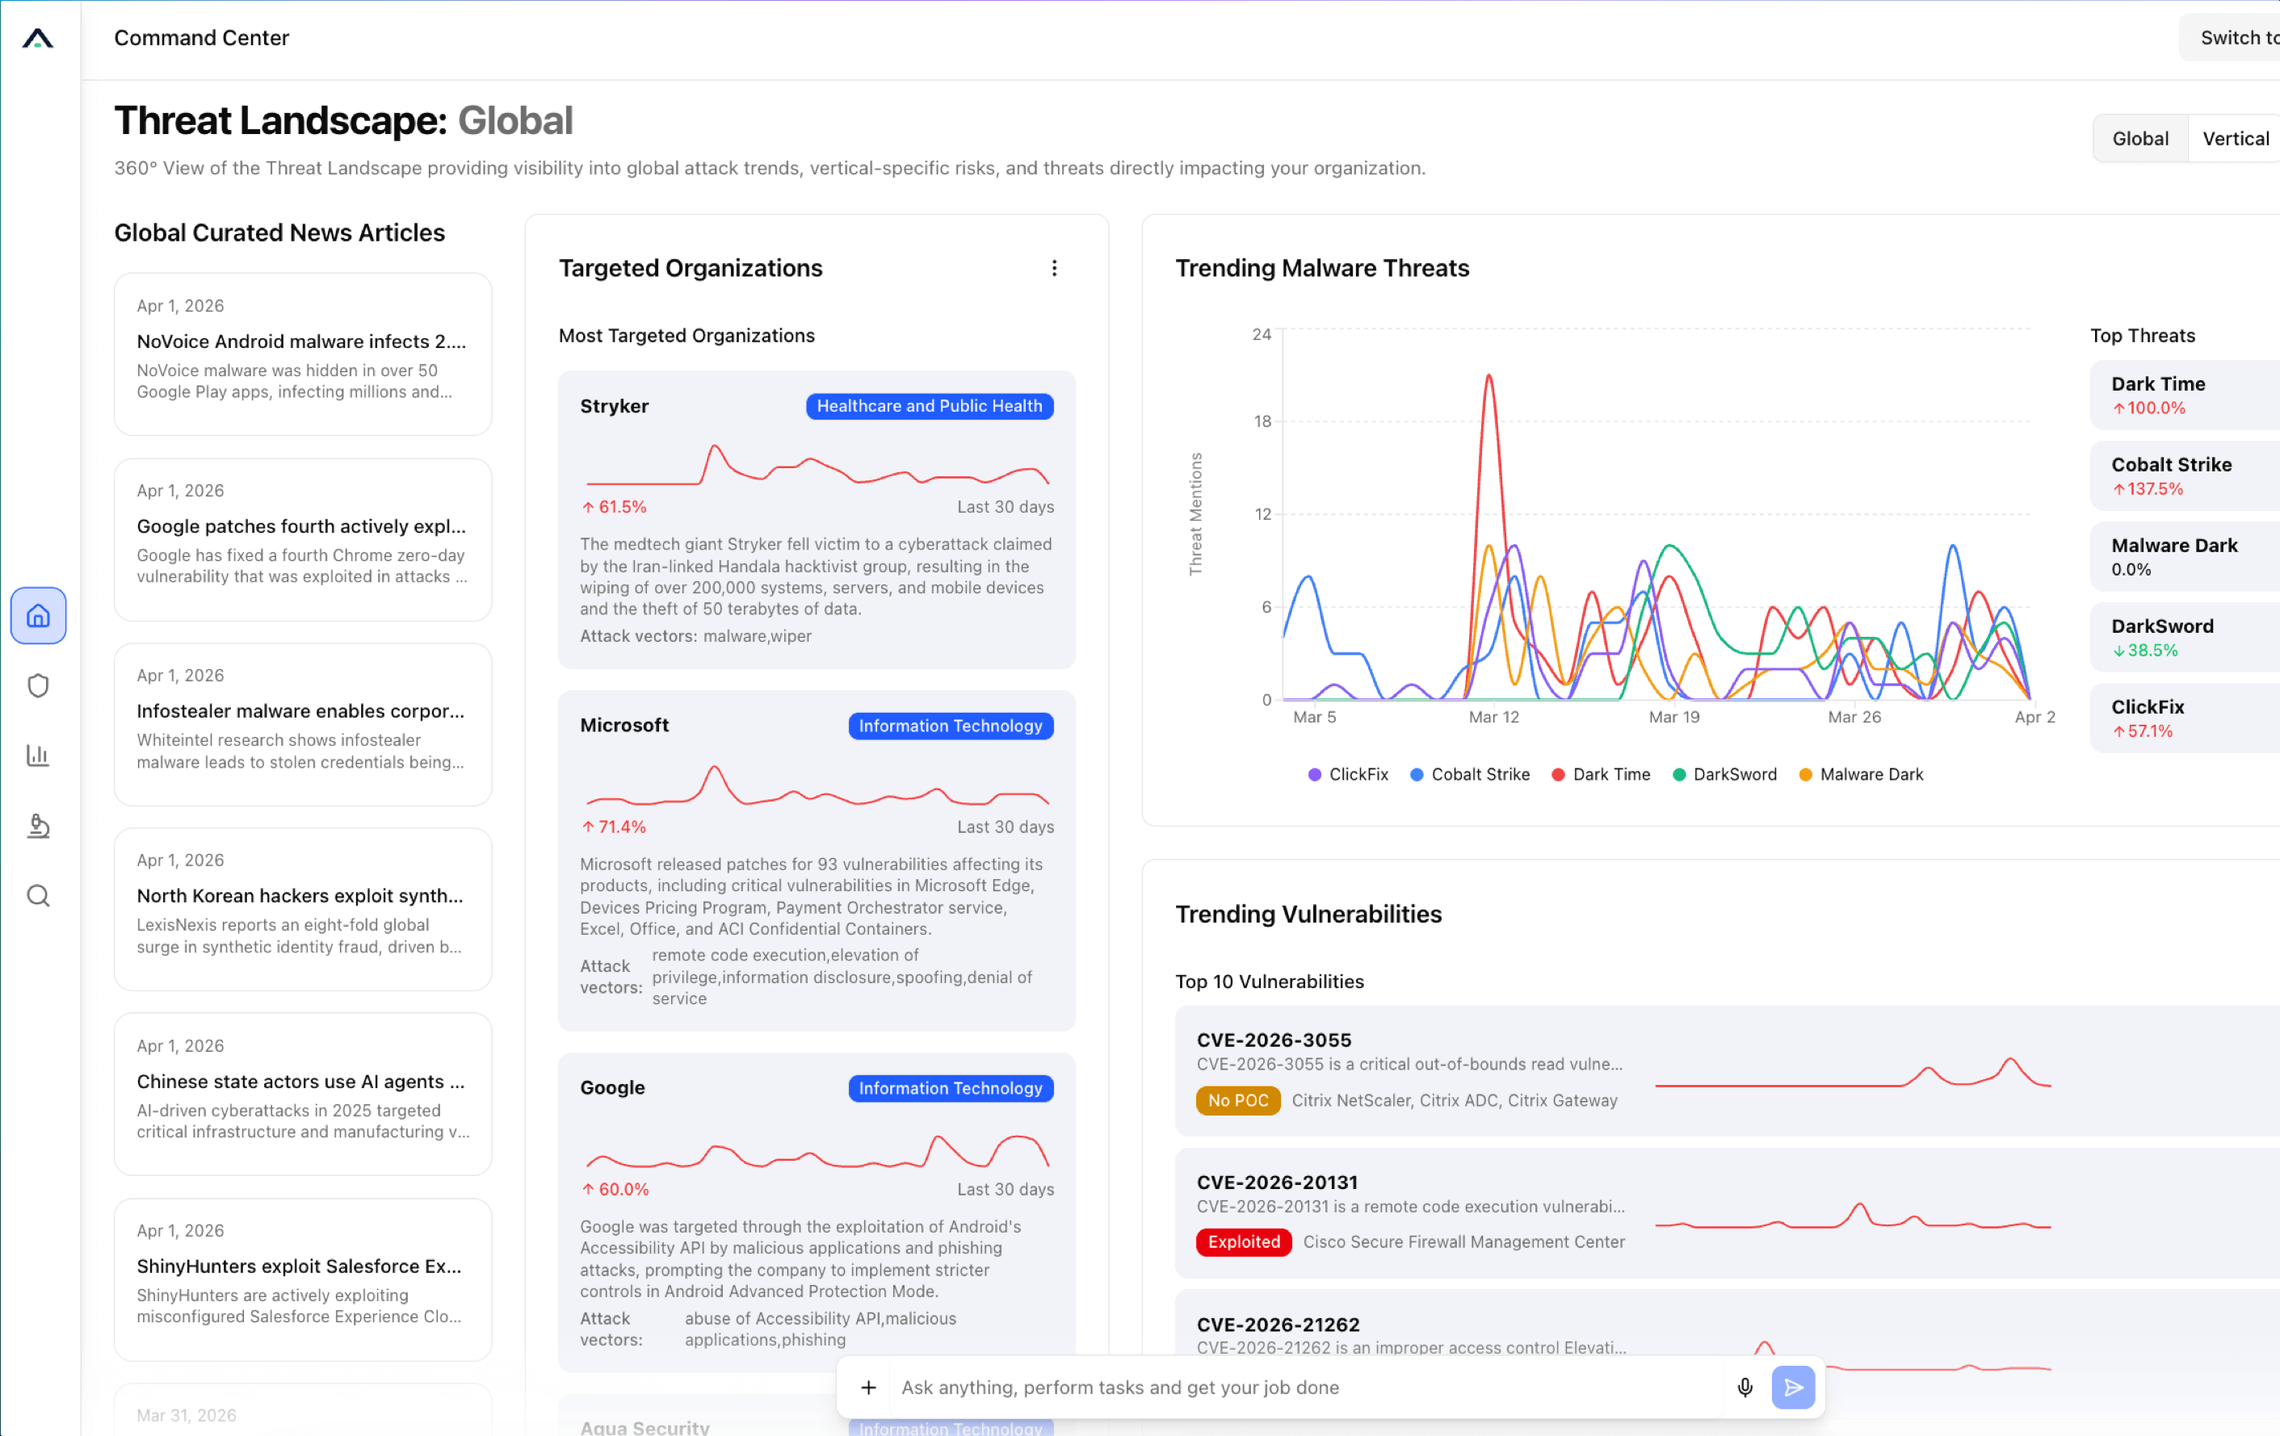
Anomali ThreatStream, now sold as ThreatStream Next-Gen in the Anomali Agentic SOC Platform, is a threat intelligence platform for analyst teams. Anomali also sells it as a managed service.
ThreatStream aggregates intelligence from hundreds of open, commercial and community sources rather than collecting its own. ThreatStream can take in partner feeds, including credential alerts from Mandiant Digital Threat Monitoring. ThreatStream then pushes the combined indicators to your SIEM and SOAR.
Key features
- Anomali Marketplace: partner feeds you can add to ThreatStream.
- Trusted Circles: share intelligence with ISACs (industry sharing groups) and peers.
- Intelligence Graph API: query Anomali’s linked threat data.
- Command Center: a dashboard that ranks current threats by how relevant they are to you.
Pricing: Not published.
Rating: 4.8/5 on Gartner Peer Insights
Pros
- The Lens browser add-on pulls indicators from a web page you’re reading into ThreatStream.
- Shows open-source lookups for each indicator of compromise (IOC) in one view.
- Works out of the box with little custom development.
Cons
- The API is hard to adapt to your own workflows.
- Support is slow to act on change and feature requests.
- Linking threat actors to their campaigns, and mapping both to MITRE ATT&CK, is clunky.
8. ThreatConnect (Dataminr)
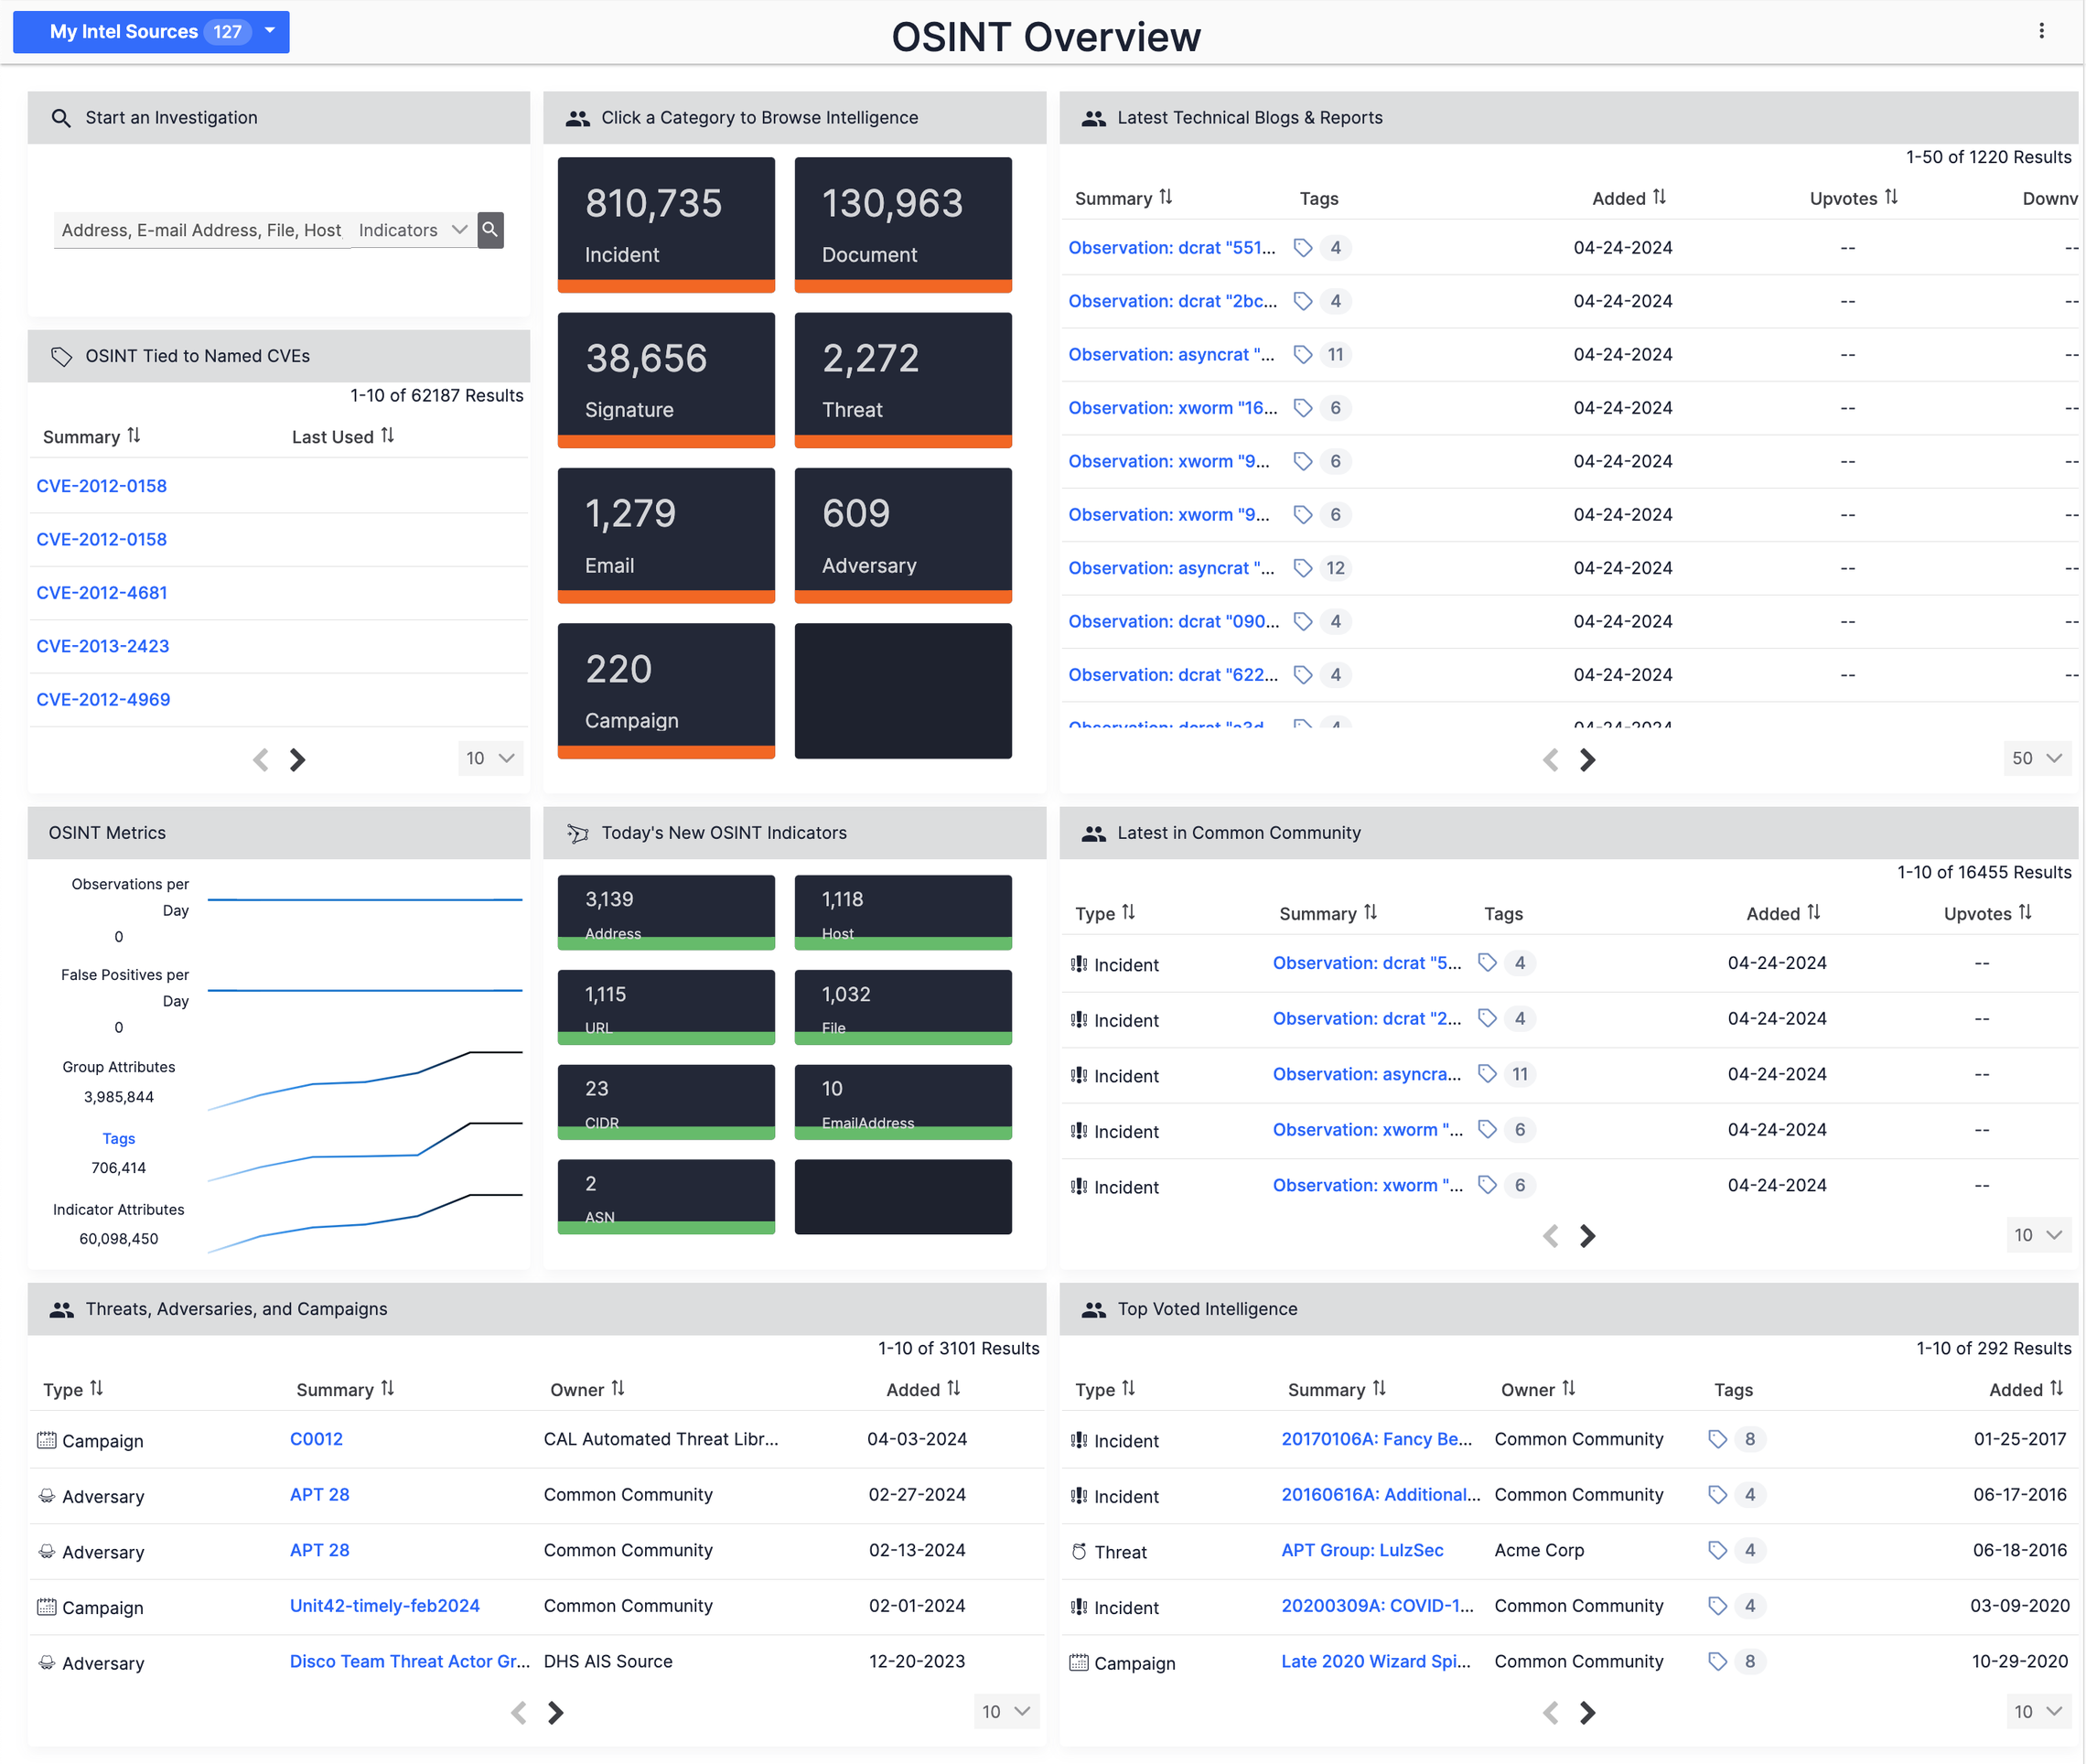
ThreatConnect is now part of Dataminr, which sells it as the Agentic Threat Intelligence Platform. ThreatConnect is built for analyst teams that automate their work with playbooks, which run response steps in your other tools.
ThreatConnect normalizes data from 300+ sources, including subscriptions you already pay for. Dataminr says it adds its own collection from 1M+ sources on the public, deep and dark web.
Key features
- Intel Agents: AI agents that spot new threats and draft finished intelligence.
- No-Code Agentic Playbooks: response playbooks you build without writing code.
- Collective Analytics Layer (CAL): scores each indicator using anonymized data from other ThreatConnect customers.
- Investigation Insights (sold separately, formerly Polarity): one search across your connected tools, such as your SIEM and EDR.
Pricing: Not published.
Rating: 4.6/5 on G2
Pros
- You build playbooks by drag and drop, with no code, to enrich indicators and run response steps.
- A built-in HTTP client lets playbooks call tools that have no ready-made app.
Cons
- The interface is hard to navigate. You can’t work on all the indicators in one event from a single screen.
- Some ThreatConnect Marketplace apps need extra licenses.
9. ThreatQ (Securonix)
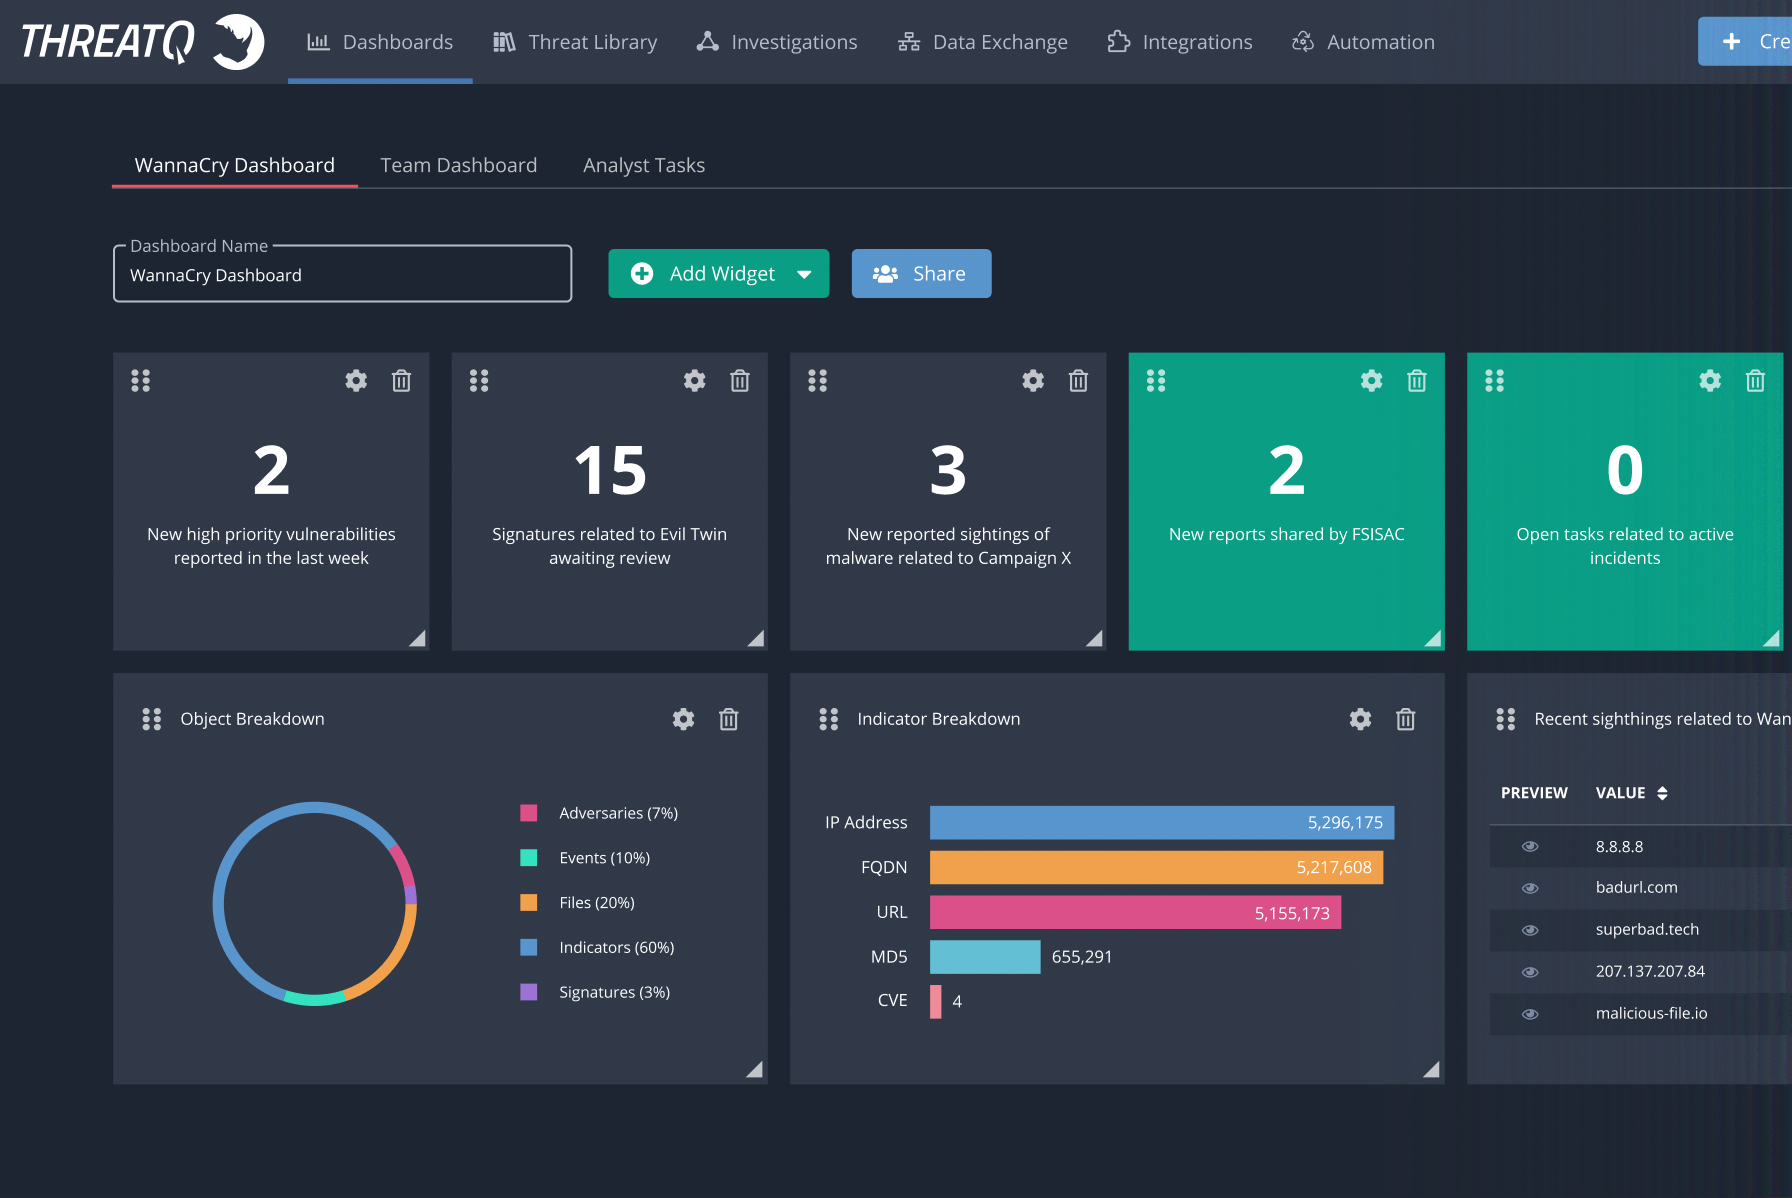
ThreatQ is a threat intelligence platform from ThreatQuotient, which Securonix bought in June 2025. ThreatQ is built for analyst teams that keep their threat data in one library and send it to their security tools.
ThreatQ aggregates threat intelligence from other sources rather than collecting its own. ThreatQ connects to over 450 security products, services and feeds. From ThreatQ, an analyst can act on an Okta account, for example by suspending the user or expiring the password.
Key features
- Threat Library: one store for all your threat data.
- Dynamic Scoring: ranks internal and external intelligence automatically.
- Smart Collections: saved groups of data to review or act on.
- TDR Orchestrator: feeds Threat Library data into your threat detection and response workflows.
Pricing: Not published.
Rating: 5.0/5 on Gartner Peer Insights
Pros
- Stable and reliable in daily use.
- New analysts can learn ThreatQ quickly.
- The product team acts on feature requests and builds missing integrations quickly.
Cons
- Releases every two weeks are hard to keep up with, and one self-hosted upgrade had to be rolled back.
- Some feeds and integrations need command-line steps to finish setup.
- You can’t easily limit who sees data by its Traffic Light Protocol (TLP) sharing label.
10. OpenCTI
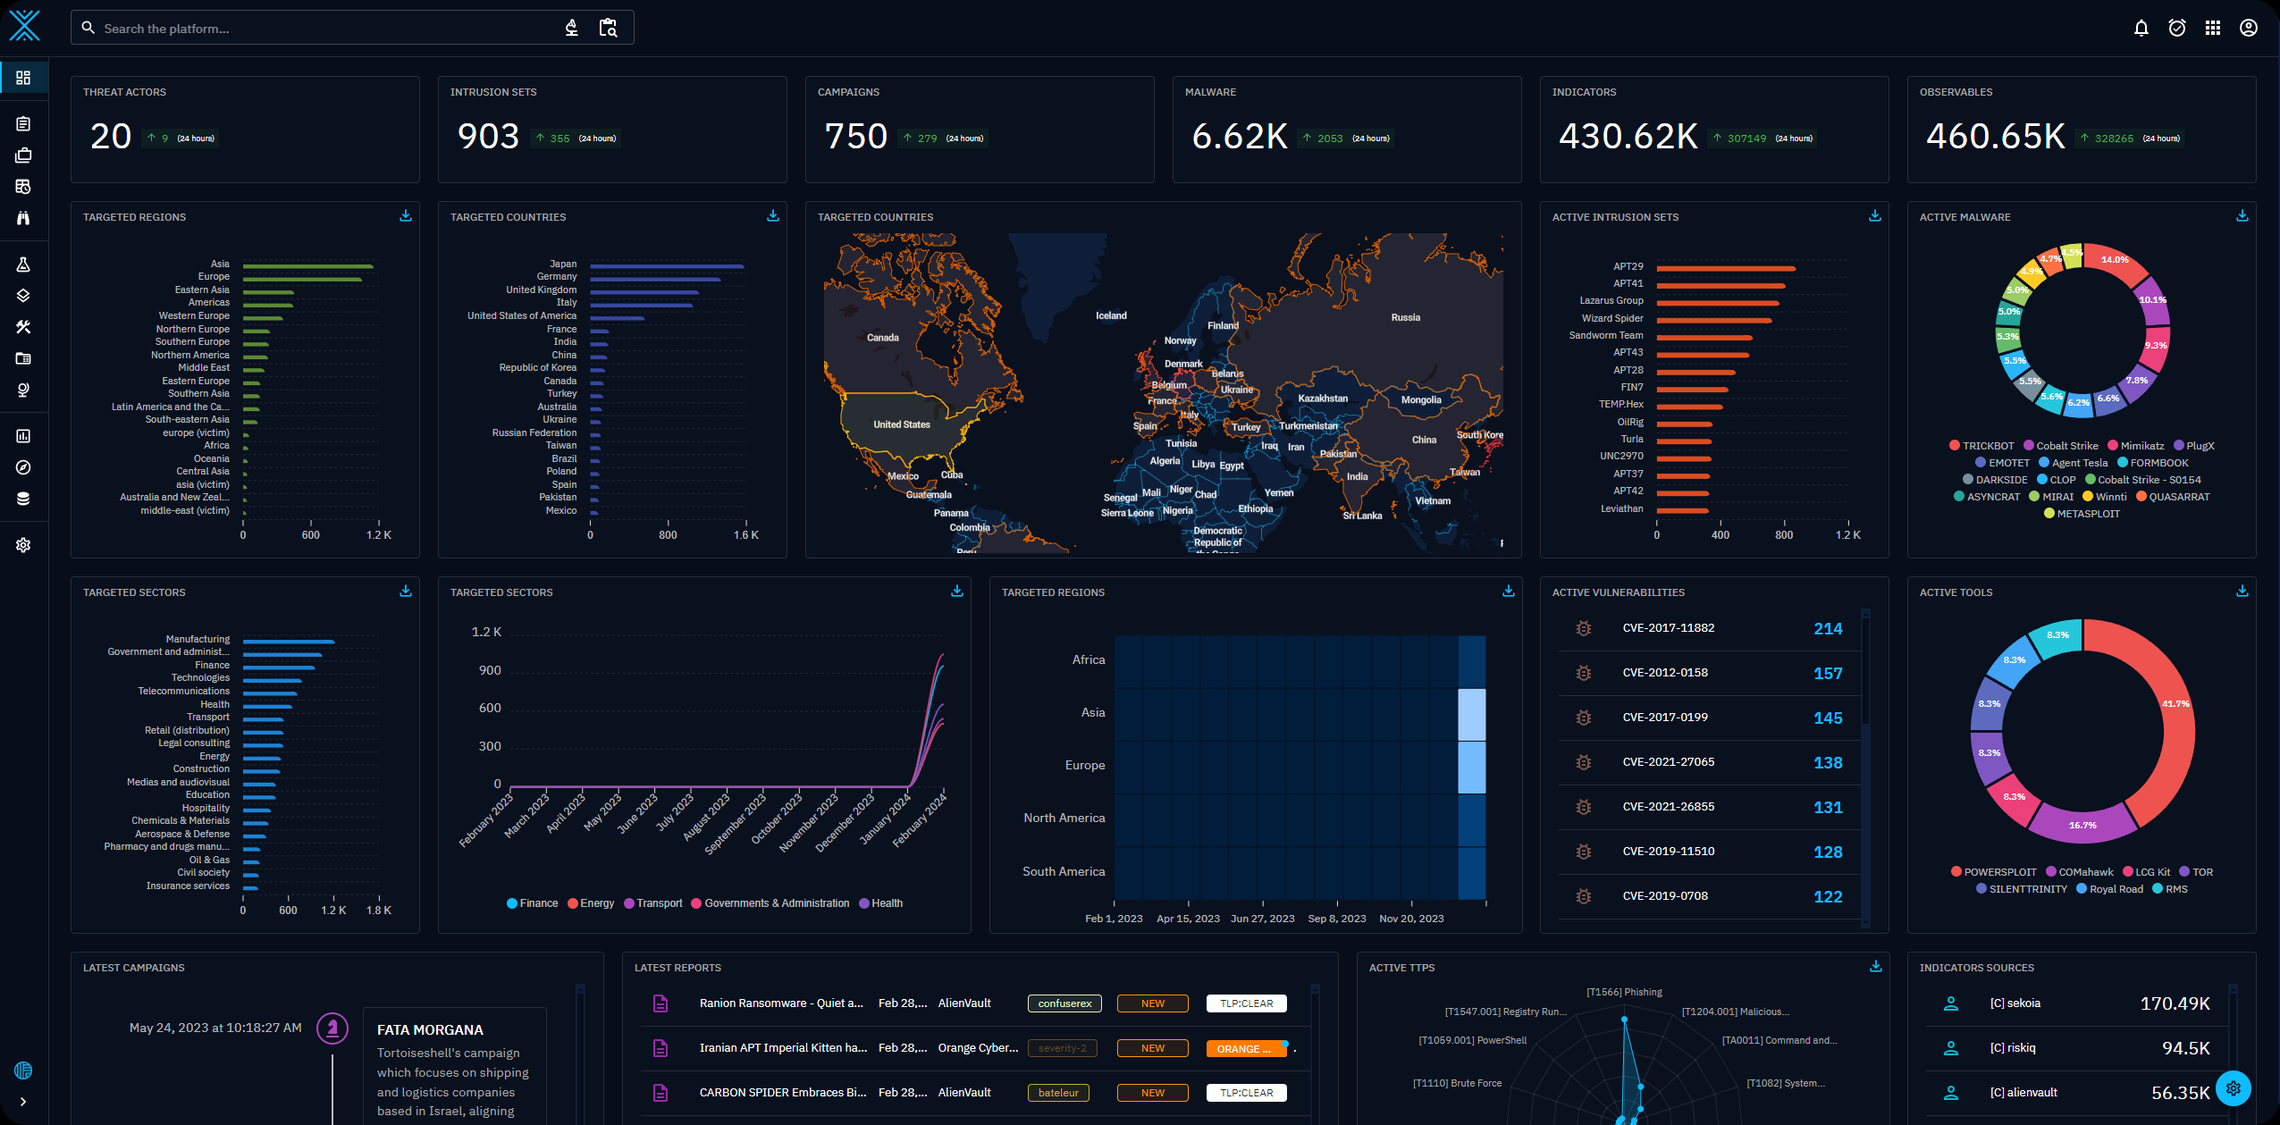
OpenCTI is a free, open-source threat intelligence platform from Filigran, built for analyst teams that organize threat data in STIX 2.1, the standard format threat intelligence tools use to share data. You can run OpenCTI yourself or in Filigran’s cloud.
OpenCTI imports data from other sources rather than collecting its own, through what Filigran counts as 400+ connectors to commercial feeds and open sources. An Enterprise Edition license adds features such as playbooks.
Key features
- STIX 2.1 knowledge graph: links actors, malware and indicators in one graph.
- Connectors: import from commercial feeds and open sources, and export to SIEMs.
- Playbooks (Enterprise Edition): trigger enrichment, webhooks, reports or cases when conditions you set are met.
- Filigran Browser Extension: turns any web page into a structured threat report.
Pricing: The Community Edition is free. Filigran gives Enterprise Edition prices on request, with a 30-day free trial of its cloud version.
Rating: 4.6/5 on G2
Pros
- A Python library makes it easy to write your own connectors.
- Matches activity in your own network against outside threat reports.
- Filigran’s support team is responsive and helps with onboarding.
Cons
- Connectors and playbooks take time to learn to set up.
- Dashboards don’t support custom columns, and graphs are hard to adjust.
- Some features are buggy or don’t work as expected.
Selection criteria
How we evaluated
We judged each tool on six criteria for enterprise security teams:
- Collects or aggregates: does the vendor gather its own data, or pull in feeds from other sources?
- Credential match: does the alert include the structured data a playbook needs to act on its own?
- Delivery: does the vendor send alerts to your SIEM or SOAR by webhook, or does someone have to log in to its portal to see them?
- After a match: who runs the reset, the vendor, your SOAR or a person?
- Freshness: does the vendor say how many credentials or stealer logs it collected last month?
- Reviews: ratings, pros and cons from the review site named in each entry.
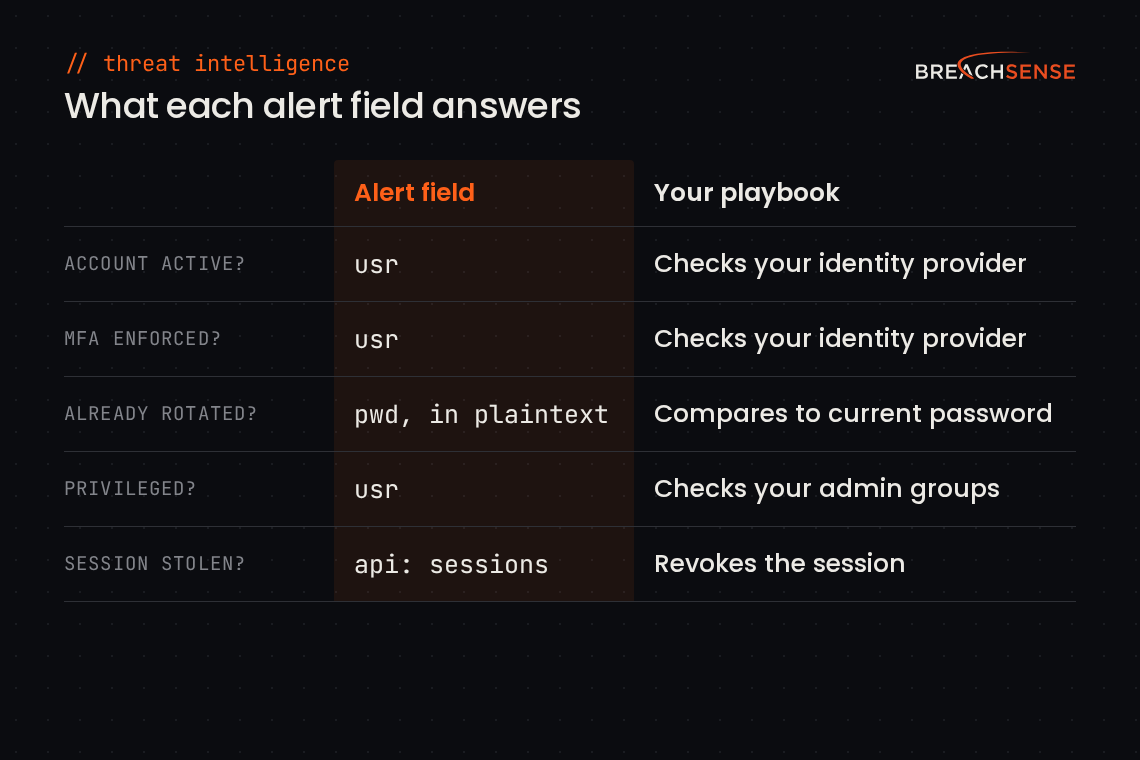
A credential alert is only useful if a playbook can answer four questions from it, with no person involved. Is the account still active? Is MFA enforced? Was the password already rotated? Is the account privileged? Your identity provider answers three of those questions from the username. The rotation question needs the plaintext password, because a plaintext password can be compared with the employee’s current password. Our API documentation lists every field an alert includes. If the alert includes a stolen session token, revoke the user’s session, even when MFA is enabled and the password has changed. A stolen session token lets an attacker sign in without the password or an MFA prompt.
For freshness, ask each vendor how much data it collected last month, not for a headline total. Recorded Future says it draws on over a million sources. Microsoft says it processes 100 trillion security signals a day. Neither number tells you whether your accounts were stolen last week. We publish how many infected machines we index each month in our infostealer reports. In September 2026, we indexed stealer logs from 1,176,466 infected machines. One machine in seven held a Microsoft 365 password. Also ask whether the vendor’s alerts flag a credential reposted from an old dump.
Which cyber threat intelligence tools do you already own?
You may already pay for cyber threat intelligence tools inside an endpoint, SIEM or SOAR contract:
- CrowdStrike’s Falcon Enterprise bundle includes Threat Intelligence & Hunting.
- Microsoft puts threat intelligence in the Defender portal for Defender XDR and Sentinel customers.
- Google SecOps Enterprise Plus includes full access to Google Threat Intelligence.
- A Palo Alto Networks Cortex XSOAR Threat Intel Management license comes with the Unit 42 feed preinstalled.
These bundled products track attacker groups and the tools they use. Check whether your tier also covers stolen employee passwords and session tokens. If your tier doesn’t, add enterprise dark web monitoring, which alerts you when we find an employee’s stolen password or session token.
How to choose
Choose by your job to be done.
| If your team… | Shortlist |
|---|---|
| has analysts with written intelligence requirements | Anomali ThreatStream, ThreatConnect or ThreatQ |
| has analysts and no platform budget | OpenCTI or MISP, plus one data source |
| needs threat actor, malware and vulnerability collection | Recorded Future, Google or Flashpoint |
| runs CrowdStrike Falcon, Defender XDR, Google SecOps or Cortex XSOAR | The vendor you already pay for |
| must reset stolen accounts today | Breachsense (your SOAR resets) or Flare (revokes sessions in Entra ID or Okta) |
Anomali, ThreatQ and OpenCTI pull in data from other sources rather than collecting their own, so a team that picks one of them still needs a data source that its response playbooks can act on.
How to narrow your threat intelligence shortlist
Narrow your shortlist in three steps. First, pick the job, either research for analysts or finding and resetting stolen accounts. Second, check whether a contract you already have, such as CrowdStrike Falcon Enterprise or Defender XDR, includes threat intelligence. If your contract includes threat intelligence, don’t pay for a second platform for research on attacker groups. Third, ask each vendor left on your shortlist how much data it collected last month. Also ask whether a playbook can tell from an alert if the account is active, privileged, protected by MFA or still using the leaked password.
To see which of your employees’ credentials have already leaked, run our free dark web scan, then book a demo.