SpyCloud Alternatives & Competitors (2026)
Quick Summary
The best SpyCloud alternatives are Breachsense, Recorded Future, Flare and Hudson Rock. Pick Breachsense if you need credential monitoring plus search inside leaked files.
| Tool | Best for | Rating |
|---|---|---|
| Breachsense | Teams that want leaked credentials from stealer logs, combo lists, phishing kits and third-party breaches, plus full-text search of leaked files | 4.8/5 (G2) |
| Recorded Future | Enterprise threat intelligence teams tracking geopolitical risk and vulnerabilities | 4.5/5 (G2) |
| Flare | Teams that want to know whether a leaked password still works in Microsoft Entra ID or Okta before resetting it | 4.7/5 (Gartner Peer Insights) |
| Hudson Rock | Teams that want to know when a partner’s employees sign in from infected machines | Not enough reviews |
SpyCloud Focuses on Stolen Identity Data
SpyCloud and Breachsense both monitor leaked credentials, but credentials are only part of your exposure. Breachsense also lets you search the full text of leaked files.
SpyCloud’s G2 reviewers praise how fast it reports exposed credentials. They recapture passwords and session cookies from breaches, stealer logs, combo lists and phishing kits. Then they help you reset exposed credentials before attackers exploit them.
Your team might need to search leaked documents for company data or monitor hacker forums where attackers sell initial access.
Last reviewed October 15, 2026. Facts about SpyCloud come from spycloud.com and its API docs, and ratings from G2 and Gartner Peer Insights.
What Does SpyCloud Do Well?
SpyCloud’s dark web monitoring focuses on extracting stolen credentials from third-party breaches and stealer logs.
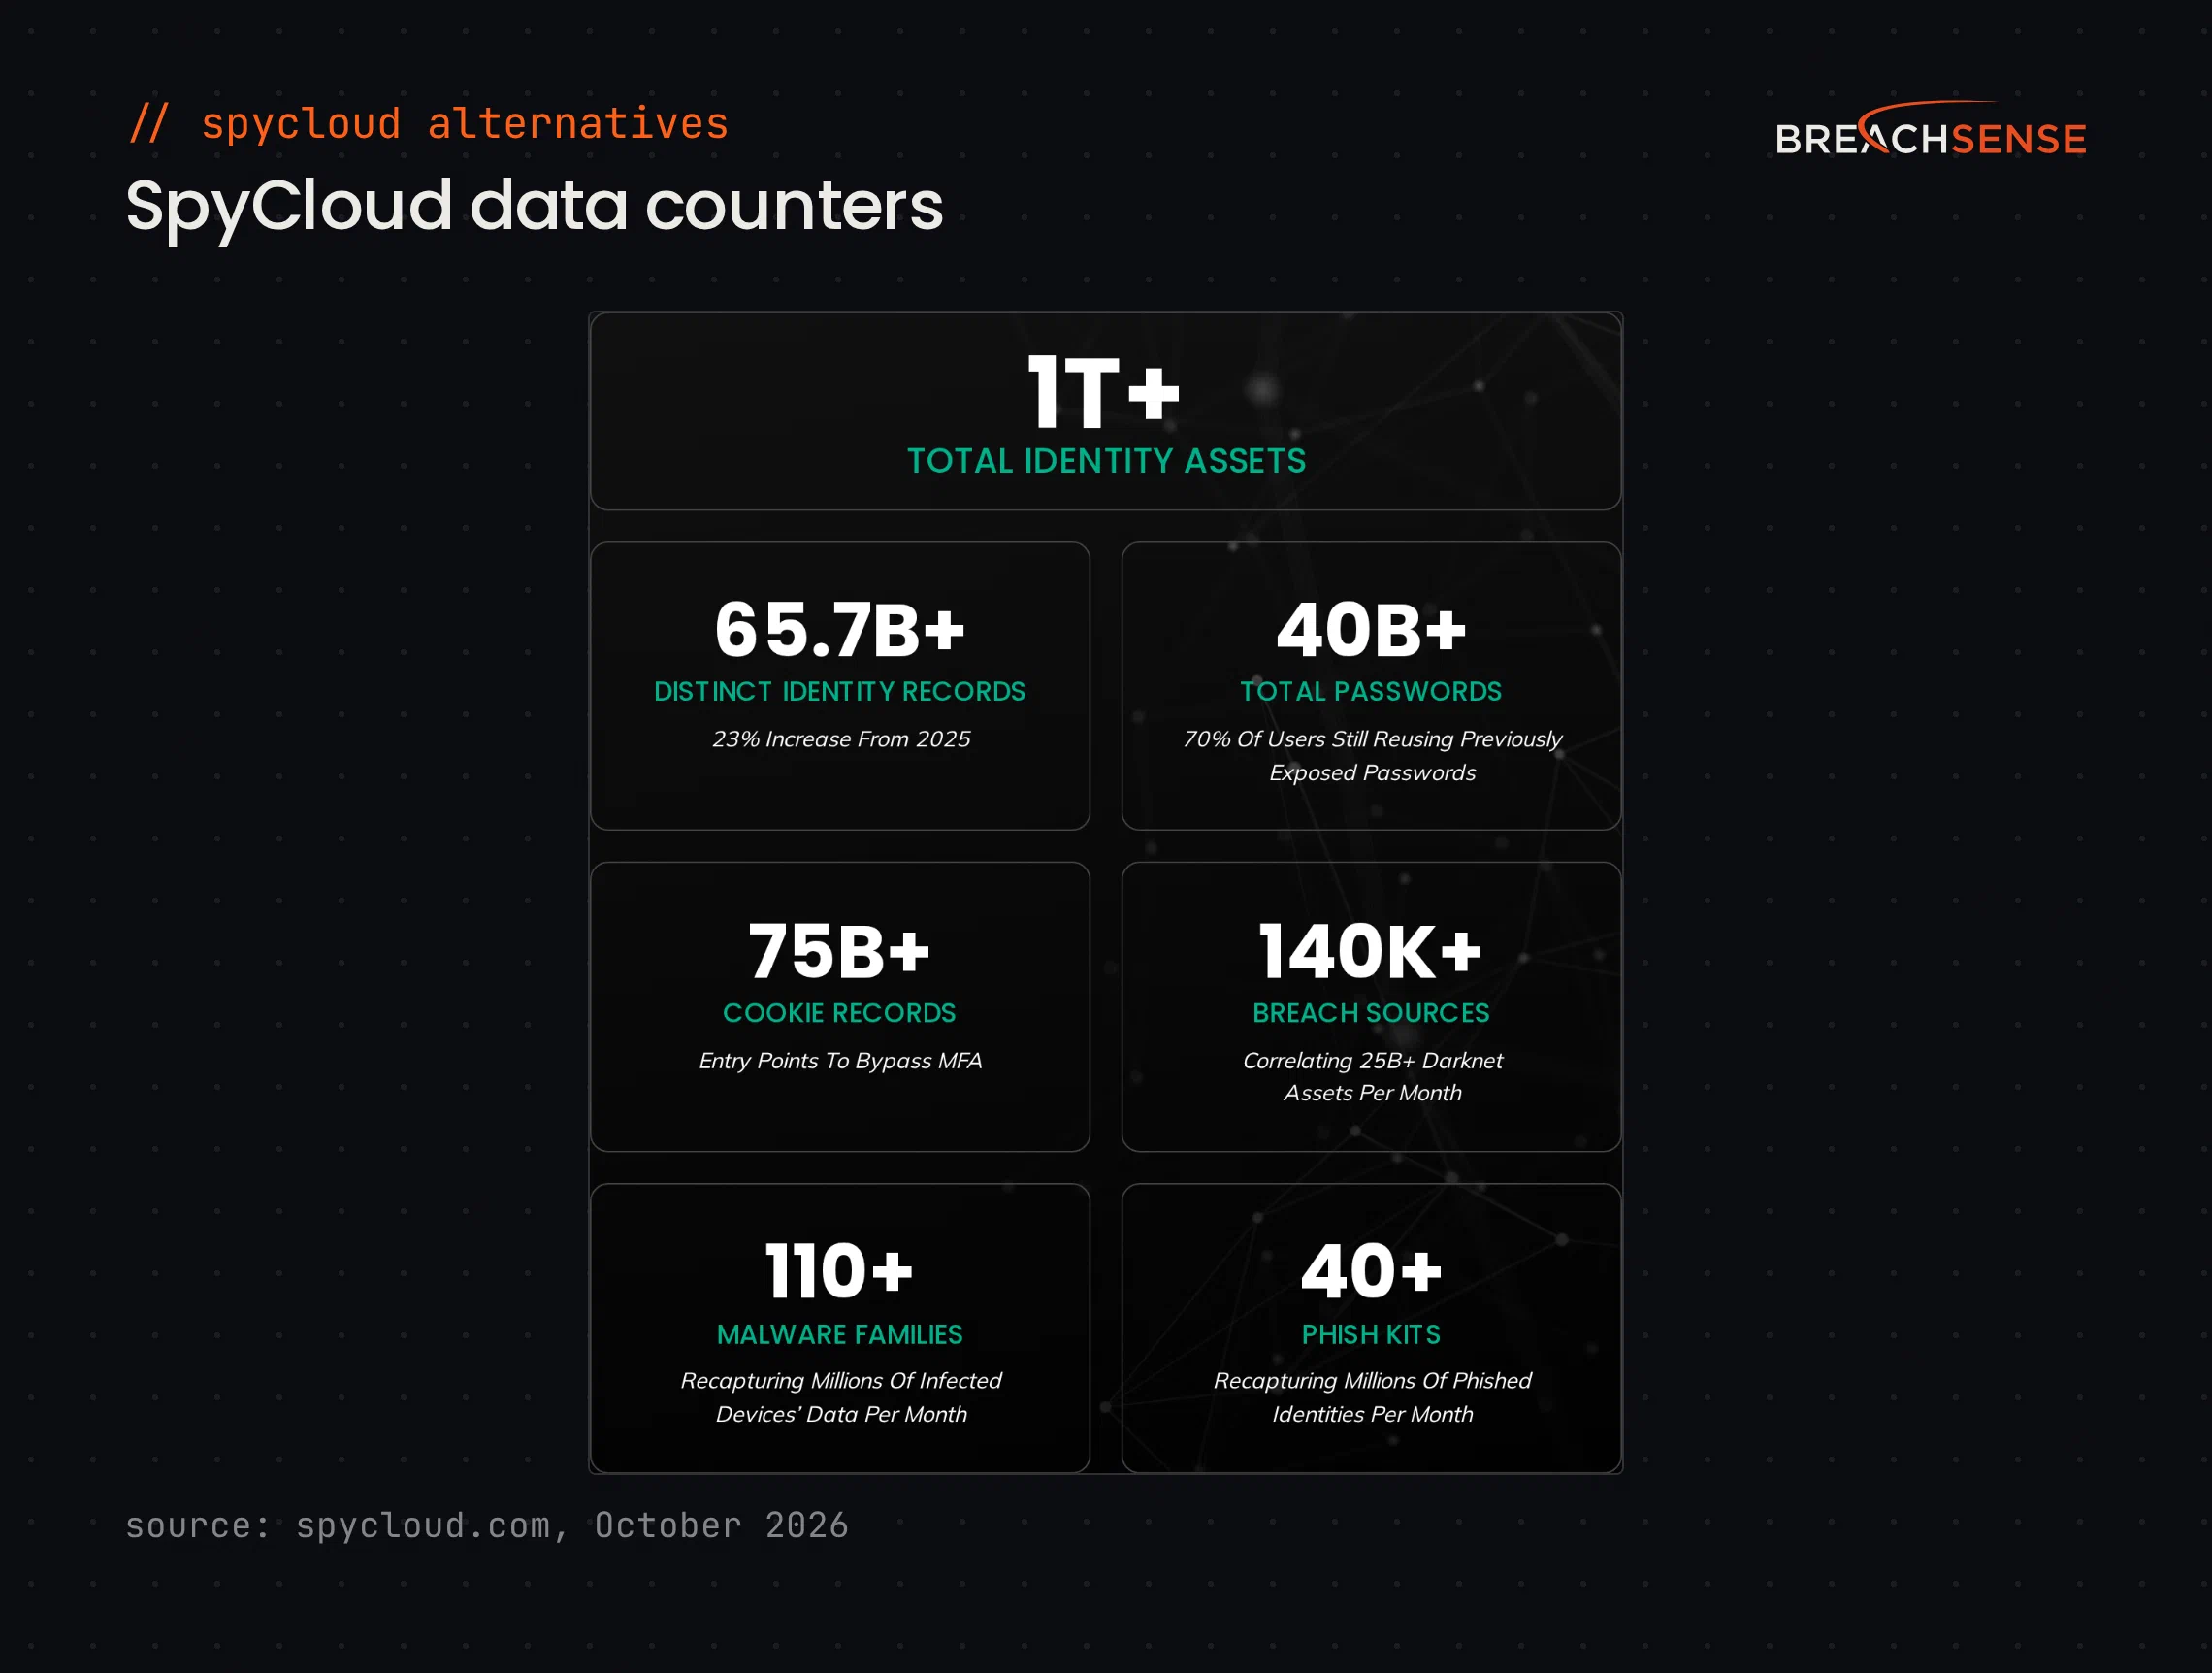
SpyCloud says it passed 1 trillion recaptured identity assets in 2026. They monitor 110+ malware families and crack hashed passwords to plaintext.
Their core strengths:
Data quality and speed. SpyCloud says new data typically reaches its dataset “within days” of surfacing in criminal markets.
Account takeover prevention. Their platform is built specifically for detecting and remediating compromised credentials.
Enterprise Protection monitors employee accounts. Consumer Threat Protection checks customer logins in real time. Identity Guardians reset leaked passwords and end stolen sessions automatically in Active Directory, Entra ID and Okta.
Data enrichment. Raw breach data gets deduplicated and enriched with context. This reduces noise for security teams reviewing alerts.
Enterprise integrations. SpyCloud connects with Okta and CrowdStrike among others. SpyCloud Connect is a managed service. SpyCloud says its engineers typically build custom integrations in 2 to 4 weeks.
SpyCloud serves large enterprises well. Seven of the Fortune 10 are customers. If your primary need is credential monitoring with a managed dashboard experience, SpyCloud is a good choice.
Why Do Teams Look for SpyCloud Alternatives?
SpyCloud handles credentials well. But three common needs push teams to look elsewhere.
You Need to Search Leaked Documents
When a vendor gets hit with ransomware, the attackers don’t just steal passwords. They grab contracts and financial records. SpyCloud’s API looks up identity records by email address or domain, for example. Neither SpyCloud’s API nor its console lets you search the text inside leaked files.
Say a law firm that handles your contracts gets hit by ransomware. The group dumps 500GB of files. If you monitor the law firm as a vendor, Breachsense alerts you when the firm is named on the group’s leak site. The third-party risk monitoring alert includes the URL of the group’s post about the firm.
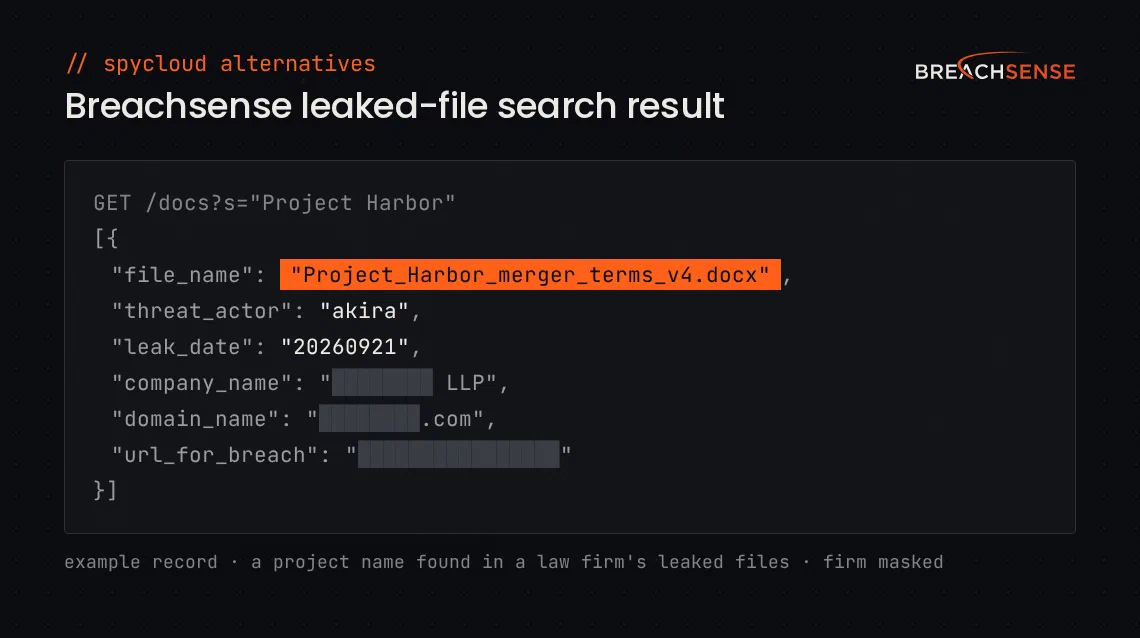
Breachsense also indexes the text of those 500GB of files. If a file mentions your company, you get an alert with a link to that file. If the file is no longer online, you can download its text from our backup. You can also search the files for any other term, such as a client’s name.
You Need Forum and Marketplace Monitoring
Attackers don’t just steal data silently. They leak files on hacker forums. They sell network access on dark web markets and Telegram channels.
SpyCloud collects data from forums and Telegram to find credentials. SpyCloud returns the credentials it finds as structured records. It doesn’t alert you to the forum posts themselves, such as an access broker’s listing. If someone posts about selling VPN access to your network, you want to know. To catch a listing like that, you need alerts when your company is named on hacker forums or dark web marketplaces.
You Need API-First Integration
SpyCloud has a full, documented REST API. The API only accepts calls from IPv4 addresses you’ve registered. A new server can’t call the API until you add its address.
Teams building automated workflows or embedding credential intelligence into products often want the API to be the primary interface. Breachsense was built around its API from day one. Calling the API needs only a license key.
How Does Breachsense Compare to SpyCloud?
Breachsense covers compromised credential monitoring like SpyCloud, including stealer log coverage and password cracking. It also indexes the full text of leaked files and monitors hacker forums where access gets sold.
| What you get | SpyCloud | Breachsense |
|---|---|---|
| Credentials, session tokens and stealer logs | Yes | Yes |
| Cracked plaintext passwords | Yes | Yes |
| Phishing-harvested credentials | Yes, from 40+ phishing kits | Yes |
| Full-text search of leaked files | Not offered | Full text, searchable by any string |
| API | REST API; IP allowlist required | Full REST API, the primary interface |
| Pricing | On request | On request |
| Before you buy | Free Check Your Exposure report; demo center | Free dark web scan; trials are available after a demo call |
| G2 rating, October 2026 | 4.7/5 | 4.8/5 |
What SpyCloud and Breachsense Each Cover
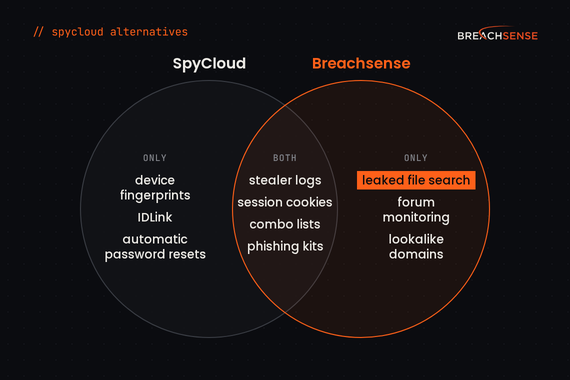
SpyCloud dark web monitoring and Breachsense both cover breach and stealer log credentials, session cookies, combo lists, phishing kits, leaked API keys and exposed data stores.
Document search. Breachsense indexes the text of files from ransomware leaks, third-party breaches and unsecured databases. With data breach monitoring, you get an alert when one of those files mentions your company. A leaked password shows you which account to reset. A leaked file shows you which documents about your company attackers stole.
Forum monitoring. Breachsense monitors hacker forums and Telegram channels where attackers discuss targets and sell network access. You catch threats that never show up in a stolen-credential feed, like an initial access broker advertising VPN access to your organization.
SpyCloud adds device fingerprints (browser and device details that identify a computer) and IDLink, which connects work and personal accounts.
For a detailed feature-by-feature comparison, see Breachsense vs SpyCloud.
Who Should Choose SpyCloud, and Who Should Choose Breachsense?
Pick SpyCloud if you want a dashboard to share with your clients, checks on customer logins as they happen, or automatic password resets.
You want a dashboard to share with your clients. Breachsense sends alerts by webhook and has no dashboard. If your clients want to log in and check their own leaked credentials, SpyCloud gives them a dashboard to do it in.
You need consumer account protection at login. SpyCloud’s Consumer Threat Protection watches customer logins as they happen. Breachsense finds the exposed credentials. It doesn’t sit in your login flow.
You want leaked passwords reset automatically. SpyCloud’s Identity Guardians reset each leaked password in your directory and end sessions that use stolen cookies.
Pick Breachsense in these cases.
API-first design. Breachsense was built for programmatic access from day one. The REST API and webhooks let you integrate with your SIEM (security information and event management) or build custom workflows. No IP allowlisting required. Teams typically integrate within hours.
You need to search inside leaked files. We index the full text of files from ransomware leaks, third-party breaches and unsecured databases. You can search those files for your domain or a project name.
You want forum and access-broker posts. We monitor hacker forums and dark web marketplaces for posts about your company, such as an initial access broker selling access to your network.
If you want analysts who interpret alerts for you, look at Flashpoint or Recorded Future. If you need geopolitical and vulnerability intelligence, look at Recorded Future or Intel 471.
What Other SpyCloud Competitors and Alternatives Exist?
SpyCloud isn’t the only option for dark web monitoring. For a broader look at the category, see our best dark web monitoring tools roundup and our credential monitoring tools list. Here are the main SpyCloud competitors teams evaluate when looking for broader coverage.
Recorded Future
Recorded Future is a broad threat intelligence platform, owned by Mastercard since December 2024. It covers geopolitical threats and vulnerability intelligence alongside dark web monitoring. It’s built for dedicated threat intelligence teams at large enterprises. Credential monitoring is one module inside a much wider platform.
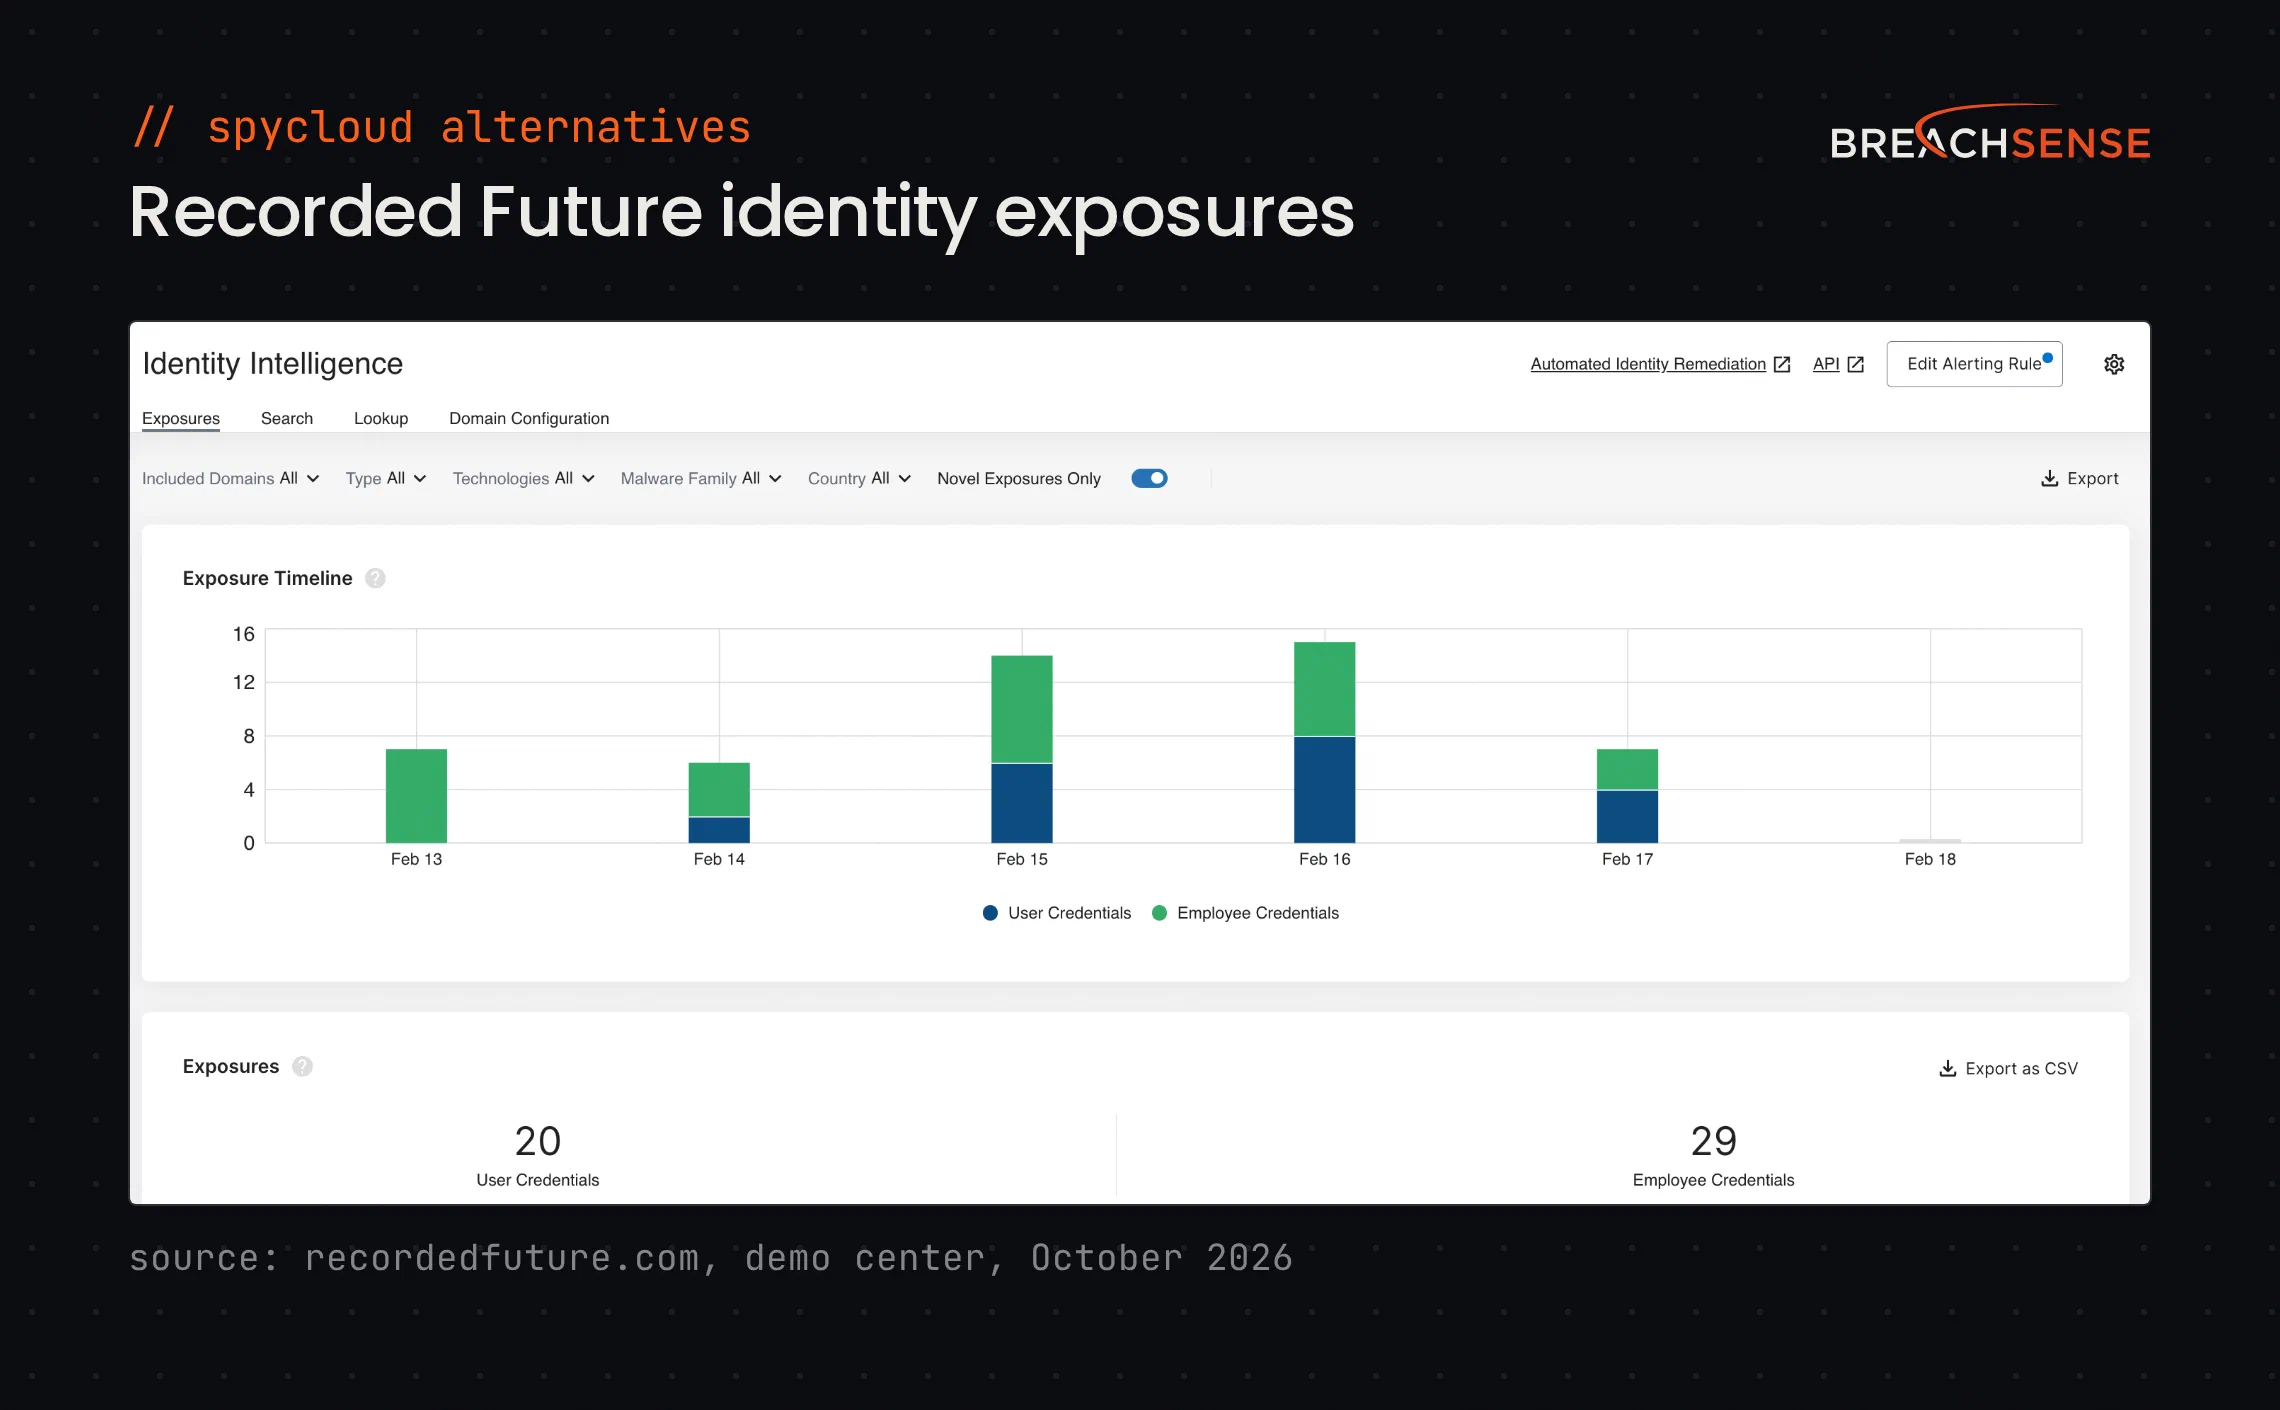
Recorded Future says it finds “1.3 million novel exposed login credentials per day.”
Key features
- Identity Intelligence. Finds exposed credentials in infostealer logs, malware combo lists and database dumps.
- Automated response. Resets exposed passwords through Okta, Microsoft Entra ID and SOAR tools, the software that runs your response playbooks.
- Brand Intelligence. Alerts you to typosquat domains and dark web discussions of your brand, and lets you start a takedown.
- Geopolitical Intelligence. Alerts you to events near your facilities, such as conflicts or natural disasters. Recorded Future also scores each country’s business risk.
Rating: 4.5/5 on G2
Pros
- Links technical indicators, such as IP addresses, to real threat actors and active exploits.
- Shows why Recorded Future gave an IP address, domain or vulnerability its risk score.
- Recorded Future’s AI writes ad hoc reports on new threat topics.
Cons
- Identity intelligence, brand protection and third-party risk often need separate add-on licenses.
- The query language is hard to learn.
- Searches can return so much information that narrowing it down takes time.
Flare
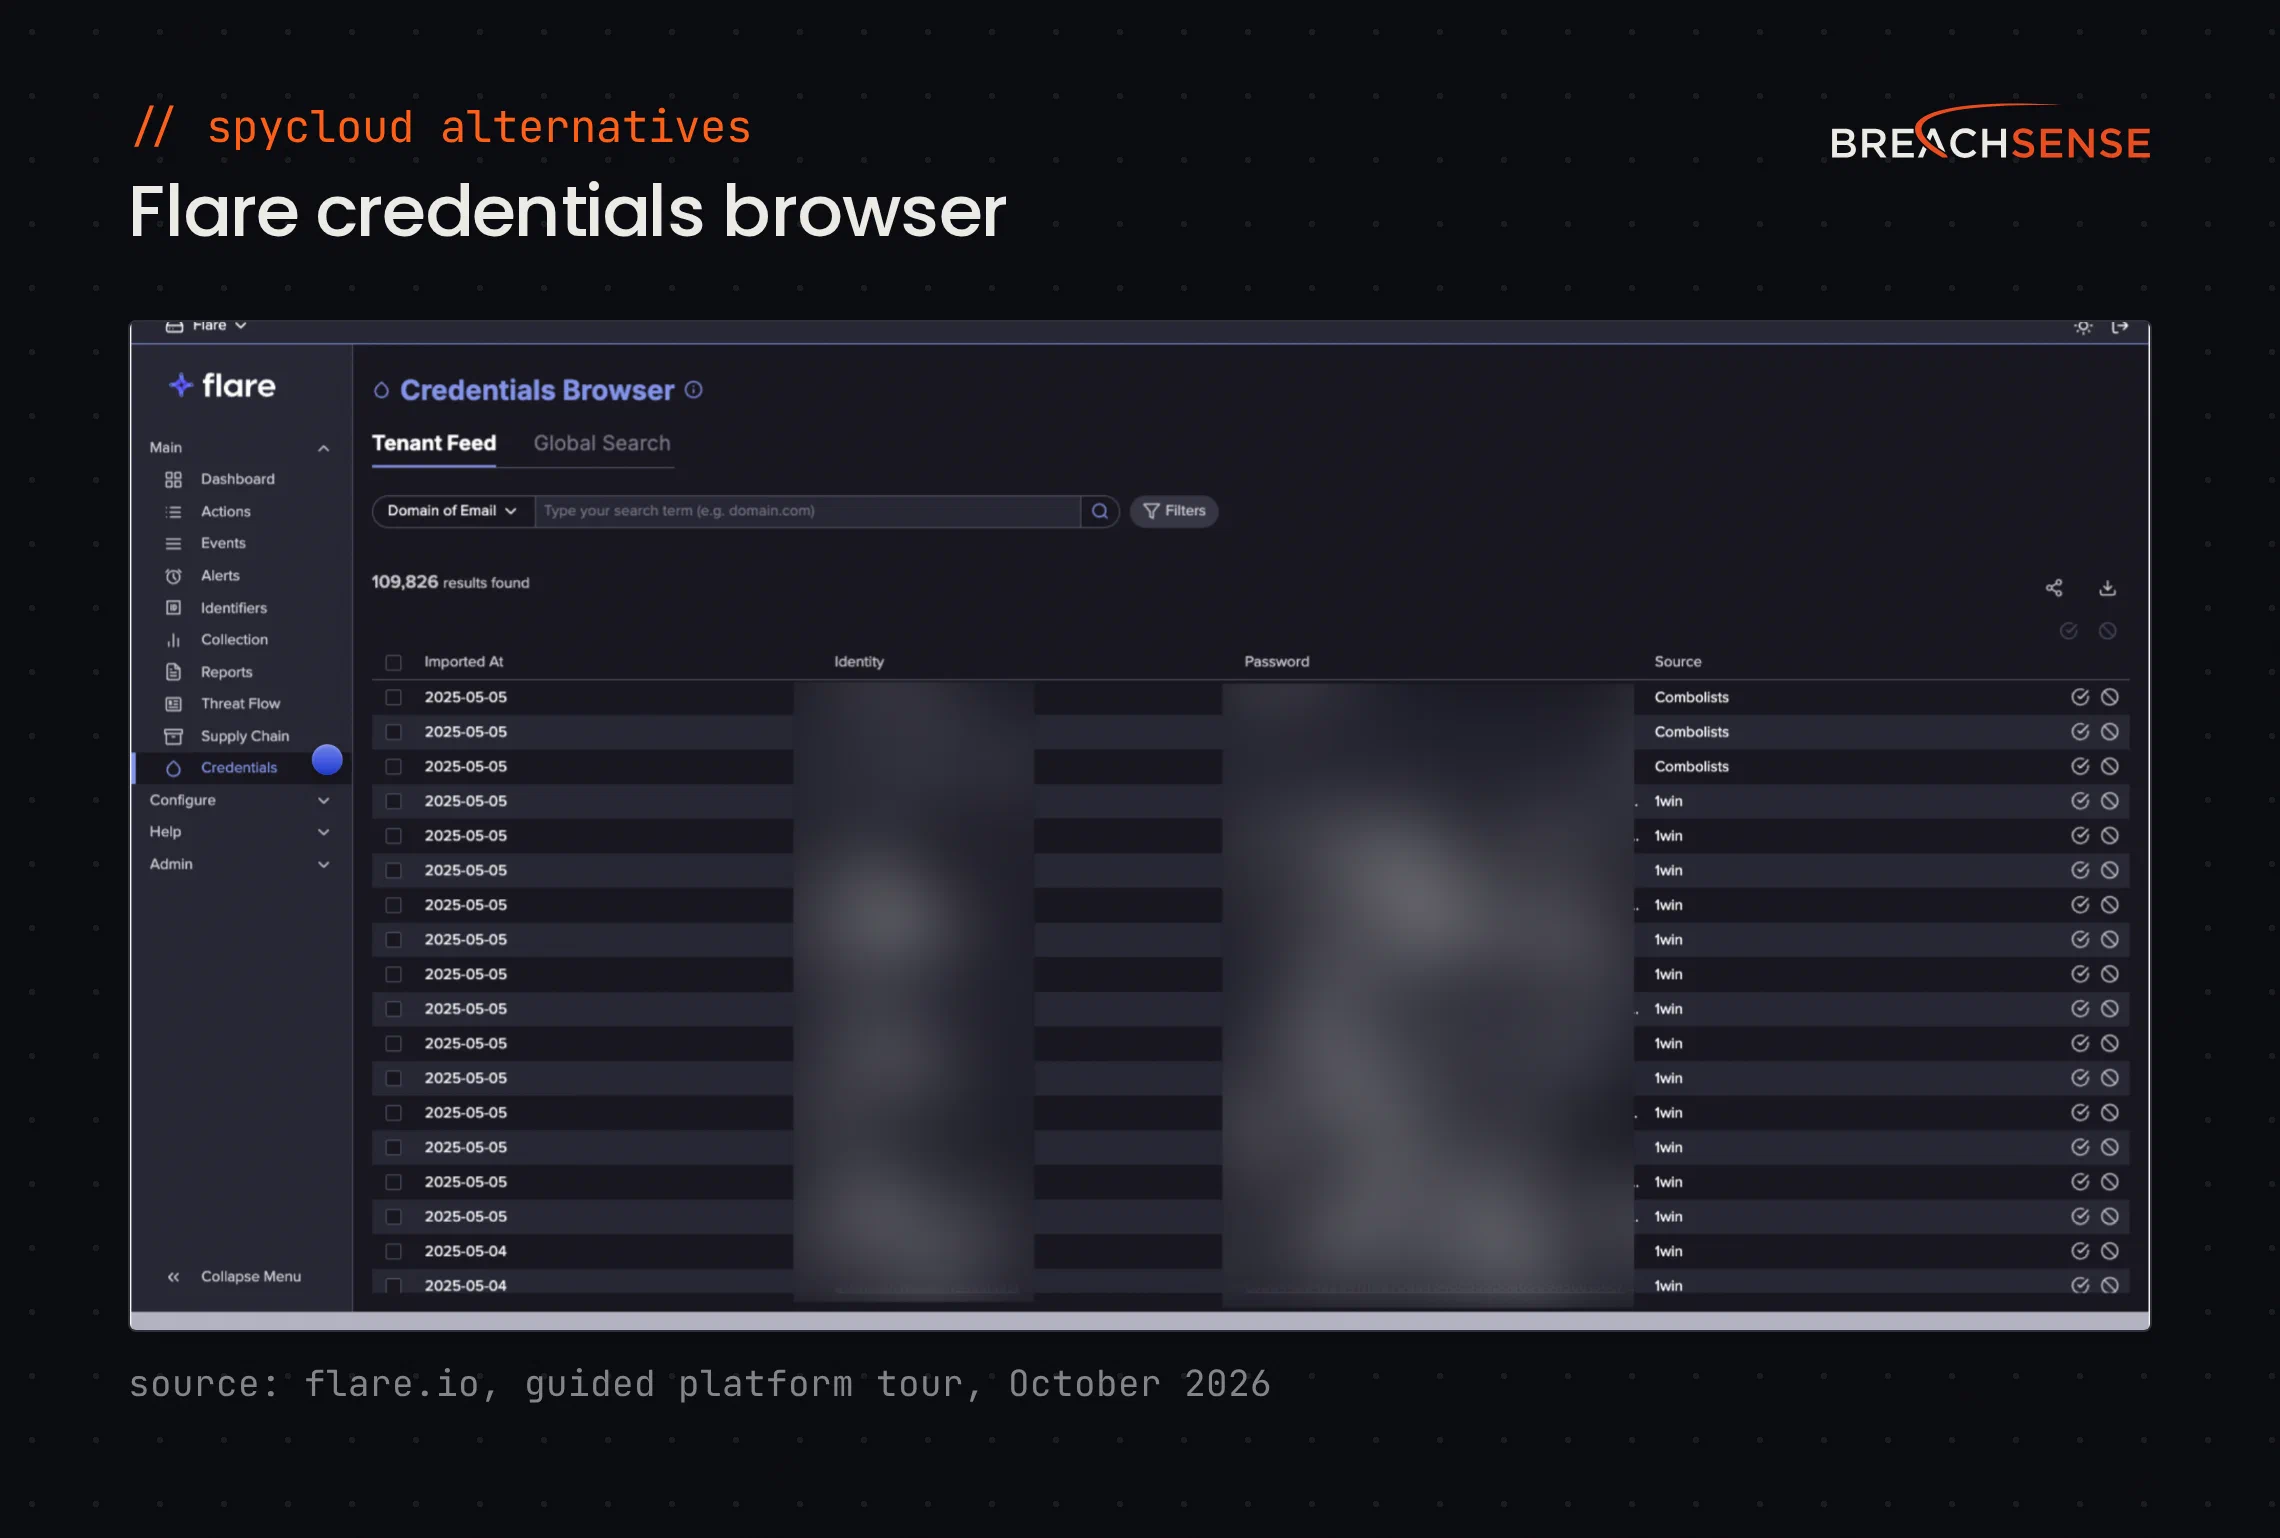
Flare focuses on external threat exposure management. It monitors dark web sources and provides continuous monitoring with a focus on mid-market and enterprise security teams. Their approach emphasizes automated alerts over manual investigation.
Flare covers dark web forums and marketplaces alongside credential monitoring. It’s positioned between identity-focused tools like SpyCloud and broad intelligence platforms like Recorded Future. For a closer look, see Flare alternatives.
Flare says it monitors over 25 billion leaked credentials.
Key features
- Identity Exposure Management. Checks whether leaked passwords still work in Microsoft Entra ID or Okta, then revokes sessions or disables the account.
- Dark web monitoring. Covers cybercrime forums on Tor and I2P (an anonymous network similar to Tor), plus Telegram channels.
- Phishing kit monitoring. Pulls stolen credentials from the Telegram groups some phishing kits send them to.
- Session cookie detection. Flags stolen session cookies and lets you revoke the sessions from Flare.
Rating: 4.7/5 on Gartner Peer Insights
Pros
- Quick to set up. Analysts without deep technical knowledge can investigate leaked credentials in Flare.
- The API covers almost everything you can do in the web console.
- Penetration testers use Flare to show clients which employees fell for real phishing attacks or appear in breach data.
Cons
- You can’t write your own rules for acting on a finding.
- Client reports are available in English only.
- A credential you dismissed can reappear later as a new finding.
Hudson Rock
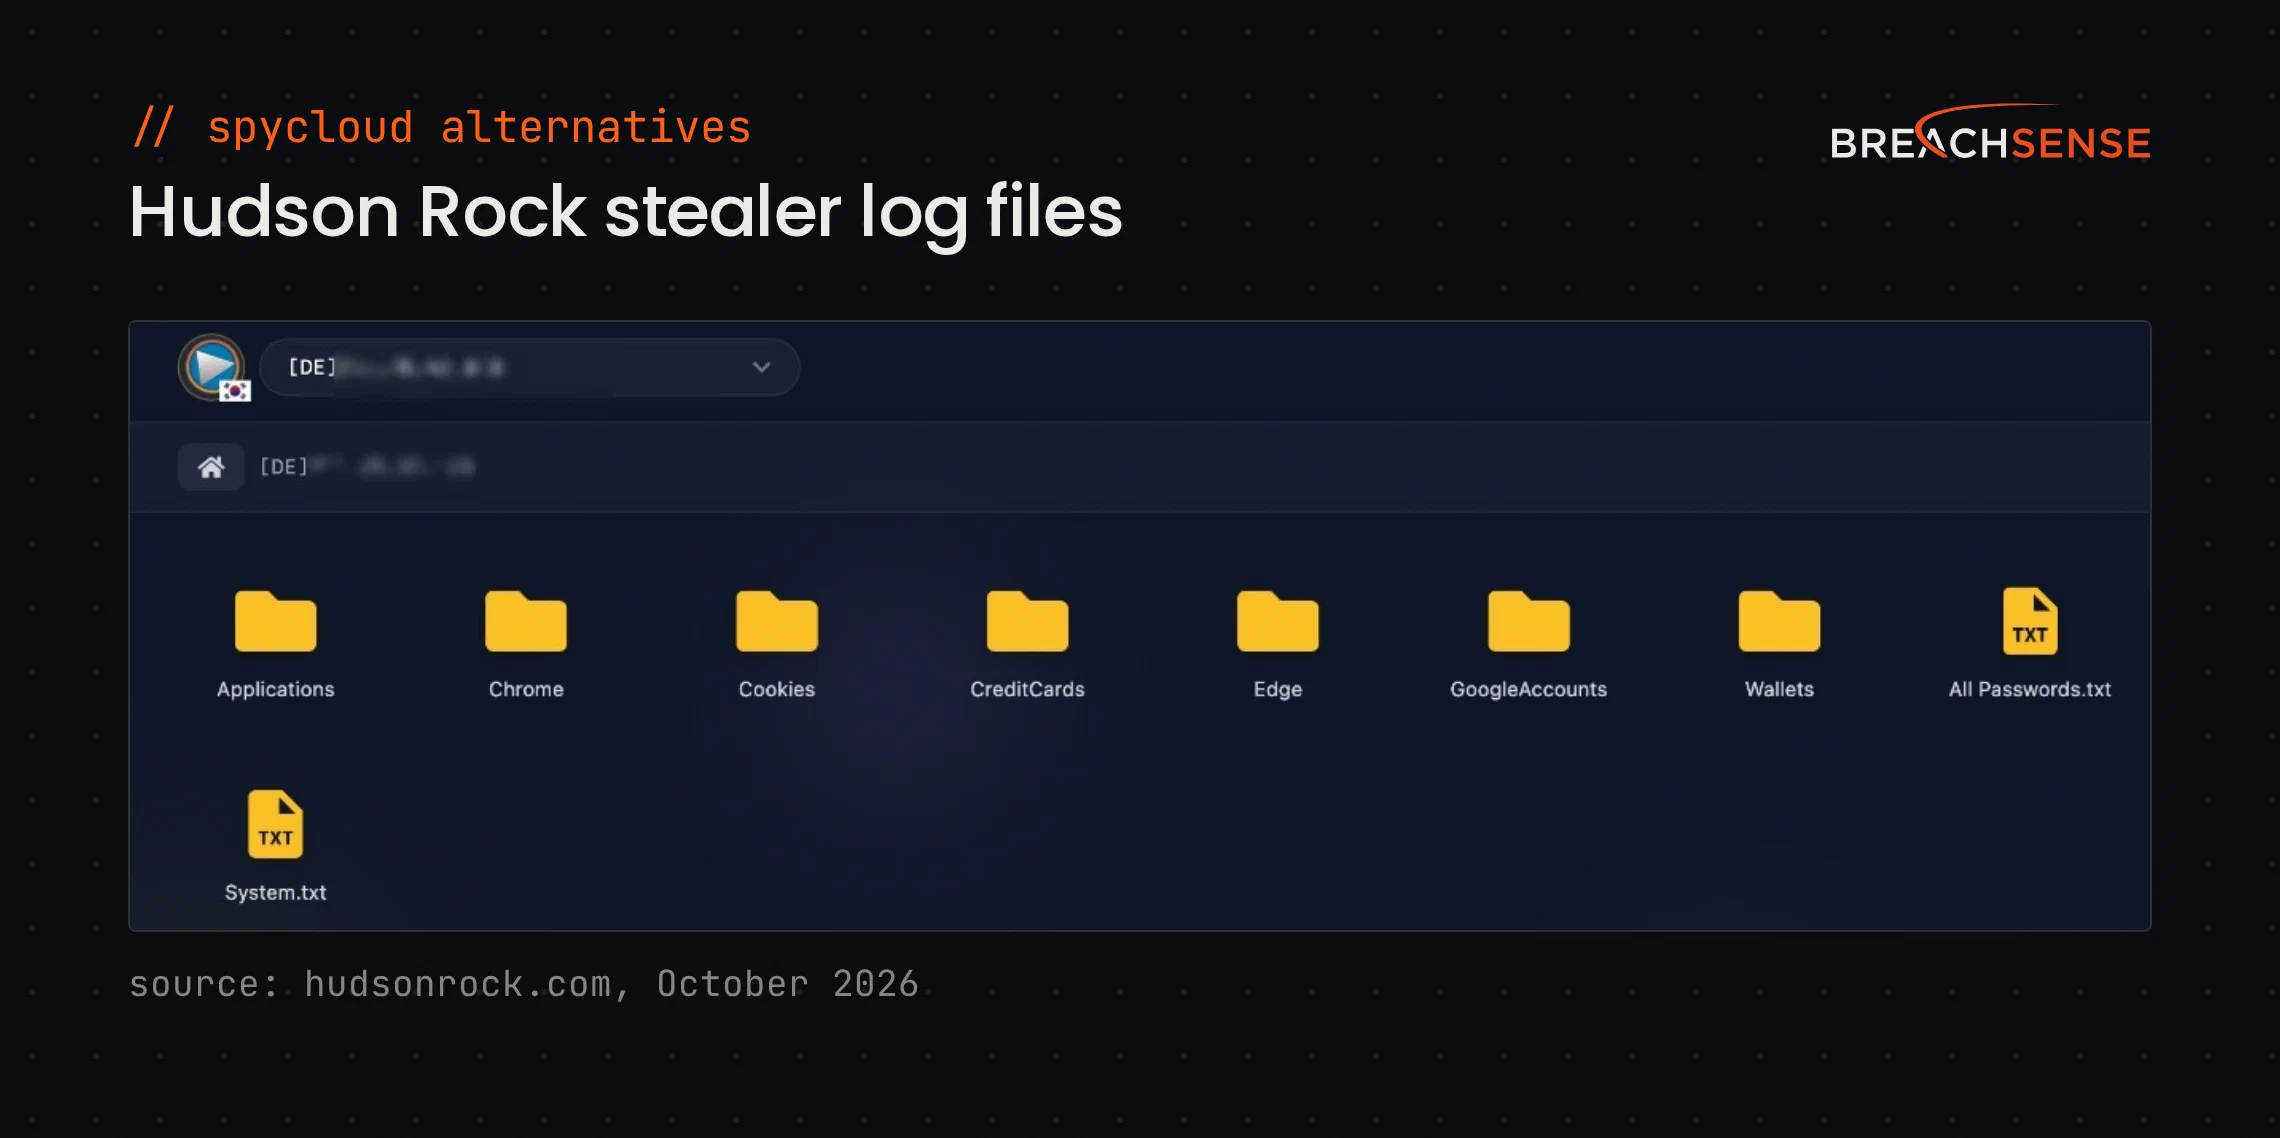
Hudson Rock focuses on infostealer intelligence. Hudson Rock’s Cavalier platform runs on data pulled from infected devices. Hudson Rock also offers free tools, including monitoring for a few emails and domains.
Hudson Rock says its data covers more than 36.8 million compromised machines, as of October 2026.
Key features
- Domain search. Lists the compromised employee, customer and third-party credentials tied to your domain.
- Account response. Ends active sessions and disables compromised accounts through Microsoft Entra ID (Azure AD), Okta or Auth0.
- Supply chain monitoring. Flags partner employees who sign in to your services from infected machines.
- Infostealer C2 Intelligence. Lists the command-and-control (C2) servers that infostealers send stolen data to, so you can block those servers.
Rating: Not enough reviews on G2.
Is Breachsense the Right SpyCloud Alternative for You?
SpyCloud is a strong credential monitoring platform. It does credential extraction and account takeover prevention well. But it’s not the right fit for every team.
Key takeaways:
- SpyCloud excels at credential extraction with a managed remediation workflow
- Breachsense adds full-text search across leaked files and monitors hacker forums for access being sold
- Alternatives like Recorded Future and Flare serve different use cases entirely
- Match the platform to what you actually need to detect, not what has the most features
If you need to search inside leaked files, Breachsense covers that. If you need identity monitoring with automatic remediation, SpyCloud does that well.
Want to see what’s exposed? Check your dark web exposure or book a demo to see how Breachsense’s full-text search works on real leaked data.